Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free CompTIA SecAI+ v1 Exam Practice Questions

Question # 31

Which of the following is the primary security risk when deploying AI models in production?

Options:

A.  

Graphics processing unit (GPU) acceleration

B.  

Model overfitting

C.  

Model encryption

D.  

Data exposure

Discussion 0
Question # 32

An analyst wants to develop a solution to review security information and event management (SIEM) logs for endpoint analytics. Which of the following is a benefit of a small language model (SLM) compared to a large language model (LLM) when cost efficiency is a consideration?

Options:

A.  

Data aggregation

B.  

Broad data set training

C.  

Domain-specific data

D.  

Data privacy

Discussion 0
Question # 33

A recent release of an AI software update exposes confidential customer information due to storage misconfiguration.

Which of the following data security controls will help maintain confidentiality despite the data leak?

Options:

A.  

Model encryption

B.  

Encryption in transit

C.  

Encryption in use

D.  

Encryption at rest

Discussion 0
Question # 34

Which of the following describes the number of training cycles used in an AI model for threat detection?

Options:

A.  

k-means clustering

B.  

Tokens

C.  

Temperature

D.  

Epoch

Discussion 0
Question # 35

Which of the following responsible AI standards refers to a principle that clearly states the reasons behind the decisions for a particular conclusion?

Options:

A.  

Accountability

B.  

Auditability

C.  

Transparency

D.  

Explainability

Discussion 0
Question # 36

Which of the following job roles in an organizational governance structure develops a model from business use cases?

Options:

A.  

Platform architect

B.  

AI risk analyst

C.  

Machine learning operations (MLOps) engineer

D.  

Data scientist

Discussion 0
Question # 37

A security analyst is aware of an active penetration test in the environment. The analyst examines SIEM log data and notices the following AI system output:
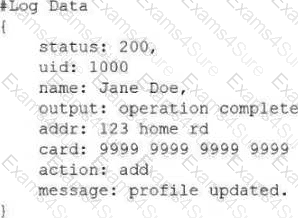
Question # 37

Which of the following is the vulnerability that has occurred and the control the analyst should implement?

Options:

A.  

The vulnerability is prompt injection, and the analyst should use endpoint detection response (EDR).

B.  

The vulnerability is model hallucinations, and the analyst should develop output validations.

C.  

The vulnerability is jailbreaking, and the analyst should utilize role-based access control.

D.  

The vulnerability is sensitive information disclosure, and the analyst should employ masking.

E.  

The vulnerability is role impersonation, and the analyst should use validation.

Discussion 0
Question # 38

A company is adopting AI and wants to create policies and procedures that include a structure for evaluating, publishing, and approving patterns for AI usage.

Which of the following should the company establish to meet this goal?

Options:

A.  

AI center of excellence

B.  

AI legal affairs office

C.  

AI audit department

D.  

AI data science division

Discussion 0
Question # 39

An organization develops a chatbot that does not provide harmful or explicit responses, must use clean and professional language, and ensures that responses are accurate.

Which of the following should the organization conduct after the chatbot is fully developed but before a customer-facing deployment?

Options:

A.  

Data labeling and classification

B.  

Model auditing and evaluation

C.  

Guardrail testing and validation

D.  

Regression modeling and minimization

Discussion 0
Question # 40

A SOC team has an AI agent that performs web searches and calls to the SOAR solution. The team is concerned about enterprise uptime and case resolution time.

Which of the following is the most appropriate use of the AI agent?
Options:

A.  

To analyze and contain offending users or hosts using SOAR playbooks

B.  

To perform research using open-source intelligence to enrich the alerts

C.  

To aggregate SOC metrics and generate reports for the leadership team

D.  

To create tabletop exercises so the team can increase its incident response speed

Discussion 0

CY0-001 PDF

CY0-001 PDF (Printable)
$46.5
$154.99

CY0-001 Testing Engine

CY0-001 PDF (Printable)
$51
$169.99

CY0-001 PDF + Testing Engine

CY0-001 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions