

Month End Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 7 - Enterprise Firewall 7.6 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every FCSS_EFW_AD-7.6 domain

Last Update 3 days ago
Total Questions : 113

Start with our free FCSS_EFW_AD-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Certified Professional Network Security exam. Each FCSS_EFW_AD-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

FCSS_EFW_AD-7.6 PDF

FCSS_EFW_AD-7.6 PDF (Printable)
$46.5
$154.99

FCSS_EFW_AD-7.6 Testing Engine

FCSS_EFW_AD-7.6 PDF (Printable)
$51
$169.99

FCSS_EFW_AD-7.6 PDF + Testing Engine

FCSS_EFW_AD-7.6 PDF (Printable)
$63.9
$212.99
Question # 1

A company ' s guest internet policy, operating in proxy mode, blocks access to Artificial Intelligence Technology sites using FortiGuard. However, a guest user accessed a page in this category using port 8443.

Which configuration changes are required for FortiGate to analyze HTTPS traffic on nonstandard ports like 8443 when full SSL inspection is active in the guest policy?

Options:

A.  

Add a URL wildcard domain to the website CA certificate and use it in the SSL/SSH Inspection Profile.

B.  

In the Protocol Port Mapping section of the SSL/SSH Inspection Profile, enter 443, 8443 to analyze both standard (443) and non-standard (8443) HTTPS ports.

C.  

To analyze nonstandard ports in web filter profiles, use TLSv1.3 in the SSL/SSH Inspection Profile.

D.  

Administrators can block traffic on nonstandard ports by enabling the SNI check in the SSL/SSH Inspection Profile.

Discussion 0
Question # 2

Why does FortiGate_B not show ICMP sessions when running: get system session list | grep icmp in an FGSP cluster?

Options:

A.  

session-pickup is disabled

B.  

session-pickup-connectionless is disabled

C.  

FGSP is misconfigured

D.  

ICMP is unsupported

Discussion 0
Question # 3

To secure your enterprise network traffic, which step does FortiGate perform first, when handling the first packets of a session? (Choose one answer)

Options:

A.  

Installation of the session key in the network processor (NP)

B.  

Decryption

C.  

A reverse path forwarding (RPF) check

D.  

IP integrity header checking

Discussion 0
Question # 4

What should be configured to provide hardware-accelerated inter-VDOM traffic?

Options:

A.  

VDOM link

B.  

NPU vlinks

C.  

VLAN

D.  

Physical link

Discussion 0
Question # 5

How can you ensure the corporate FortiGate learns the 192.168.1.0/24 network?

Options:

A.  

Add static route

B.  

Enable RIP

C.  

Implement OSPF over IPsec

D.  

Add network locally

Discussion 0
Question # 6

Refer to the exhibits.

A policy package conflict status and information from the import device wizard in the Core1 VDOM are shown. When you import a policy package, the following message appears for the Web_restrictions web filter profile and the deep-inspection SSL-SSH profile: " The following objects were found having conflicts. Please confirm your settings, then continue. " The Web_restrictions and deep-inspection profiles are used by other FortiGate devices within FortiManager. Which step must you take to resolve the issue? (Choose one answer)

Options:

A.  

Retrieve the FortiGate configuration to automatically export correct objects and policies.

B.  

Create uniquely named objects on FortiGate and reimport them into the policy package.

C.  

Select the FortiManager configuration that accepts changes on FortiManager and preserves existing configurations on FortiGate devices.

D.  

Use non-default object values because FortiManager is unable to alter default values.

Discussion 0
Question # 7

An administrator is designing an ADVPN network for a large enterprise with spokes that have varying numbers of internet links. They want to avoid a high number of routes and peer connections at the hub.

Which method should be used to simplify routing and peer management?

Options:

A.  

Deploy a full-mesh VPN topology to eliminate hub dependency.

B.  

Implement static routing over IPsec interfaces for each spoke.

C.  

Use a dynamic routing protocol using loopback interfaces to streamline peers and routes.

D.  

Establish a traditional hub-and-spoke VPN topology with policy routes.

Discussion 0
Question # 8

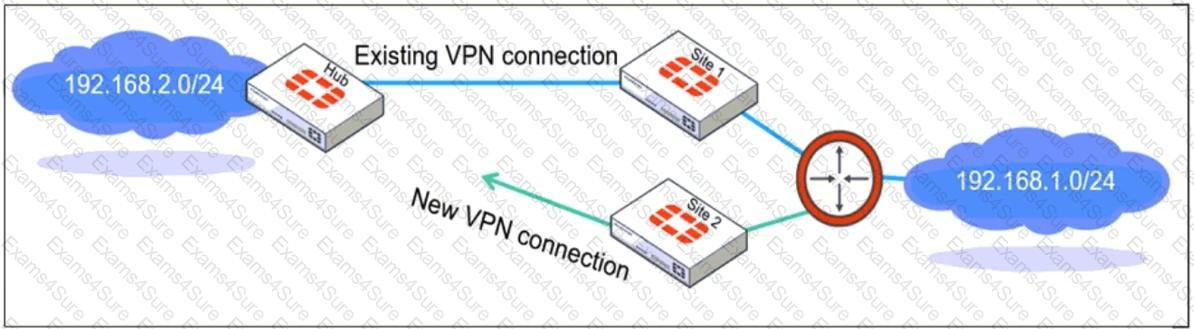
Refer to the exhibit, which shows a network diagram showing the addition of site 2 with an overlapping network segment to the existing VPN IPsec connection between the hub and site 1.
Question # 8

Which IPsec phase 2 configuration must an administrator make on the FortiGate hub to enable equal-cost multi-path (ECMP) routing when multiple remote sites connect with overlapping subnets?

Options:

A.  

Set route-overlap to either use-new or use-old

B.  

Set net-device to ecmp

C.  

Set single-source to enable

D.  

Set route-overlap to allow

Discussion 0
Question # 9

Refer to the exhibit.

An administrator is deploying a hub and spokes network and using OSPF as dynamic protocol.

Which configuration is mandatory for neighbor adjacency?

Options:

A.  

Set bfd enable in the router configuration

B.  

Set network-type point-to-multipoint in the hub interface

C.  

Set rfc1583-compatible enable in the router configuration

D.  

Set virtual-link enable in the hub interface

Discussion 0
Question # 10

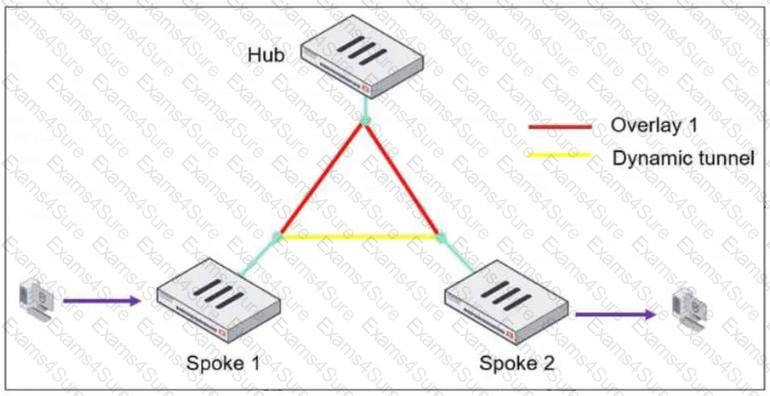
Refer to the exhibit, which shows an ADVPN network.
Question # 10

The client behind Spoke-1 generates traffic to the device located behind Spoke-2.

What is the first message that the hub sends to Spoke-1 to bring up the dynamic tunnel?

Options:

A.  

Shortcut query

B.  

Shortcut offer

C.  

Shortcut reply

D.  

Shortcut forward

Discussion 0

Free Exams Sample Questions

