Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Network Security Essentials for Locally-Managed Fireboxes Practice Questions

Question # 1

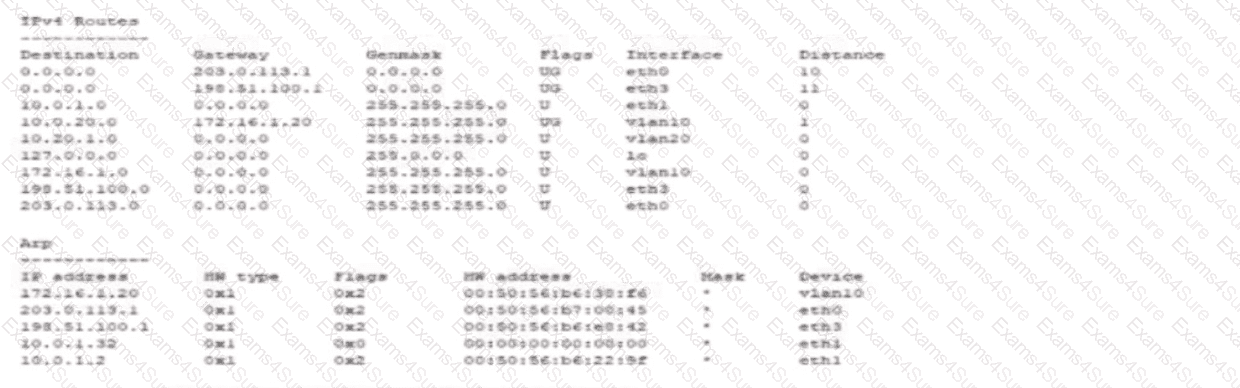
You configured your Firebox interfaces and routes and want to verify the status of the routes and connected hosts. You found this information in Firebox System Manager > Status Report. What is true about the IPv4 routes and ARP table in this deployment? (Select one.)
Question # 1

Options:

A.  

The Firebox is publicly reachable at 198.51.100.1 through the eth0 interface

B.  

10.0.20.53 can be reached through the vlan20 interface

C.  

The MAC address for the default gateway that currently routes traffic is 00:50:56:b5:e5:42

D.  

The MAC address for 172.16.1.20 is 00:50:56:b0:22:0f

E.  

The Firebox cannot resolve a MAC address for 10.0.1.32

Discussion 0
Question # 2

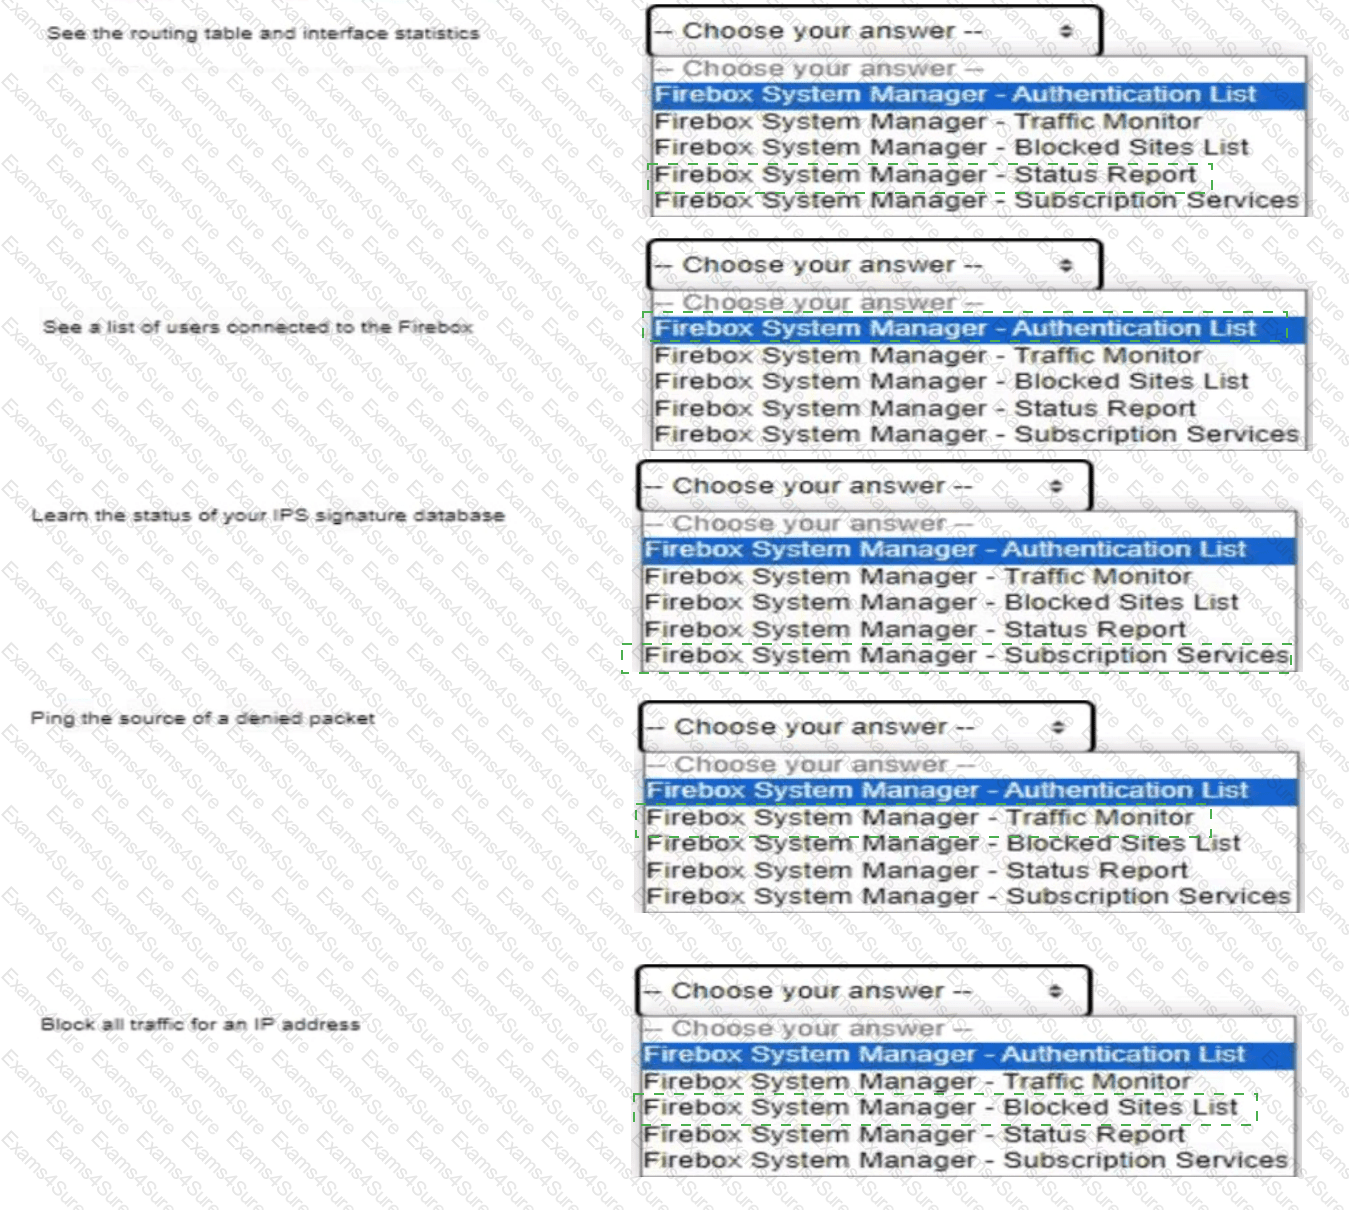
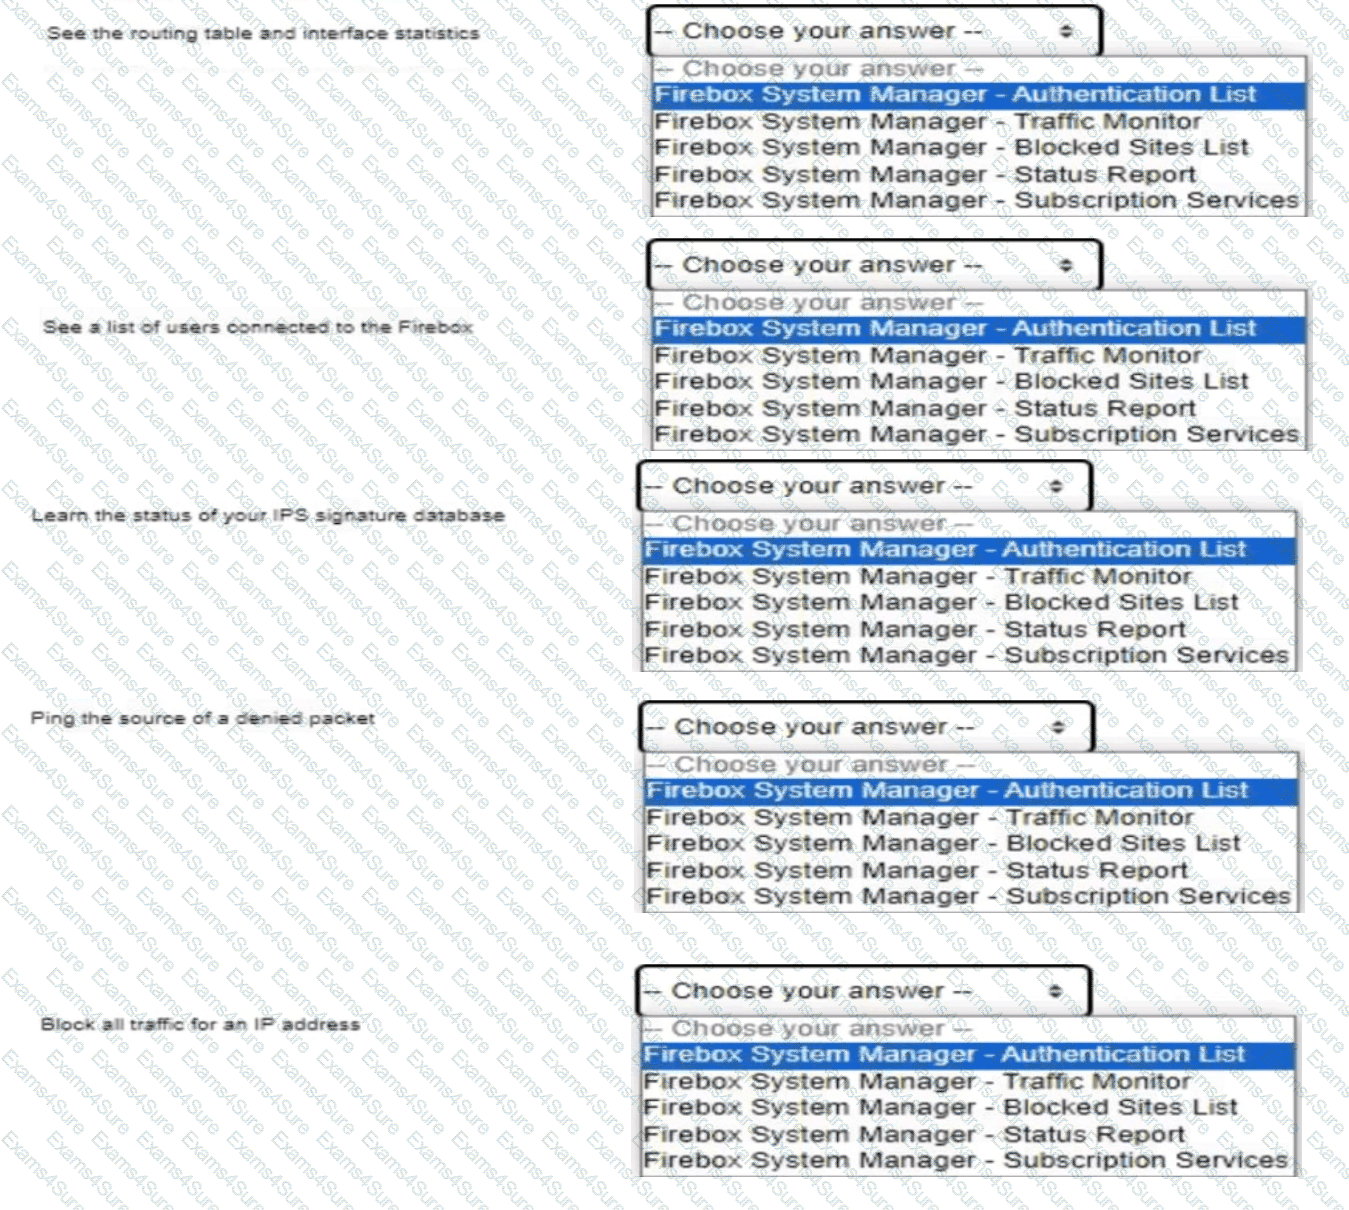
In Firebox System Manager, where can you perform each of these tasks?

Question # 2

Options:

Discussion 0
Question # 3

In the network configuration shown in this image, which aliases include Eth2 as a member? (Select three.)

Options:

A.  

Any-Trusted

B.  

Optional-1

C.  

Any-External

D.  

Any-Optional

E.  

Any

Discussion 0
Question # 4

You bought a new Firebox and want to use the configuration from an existing Firebox you already configured. The best way to migrate the configuration is to restore a backup image from the existing Firebox to the new Firebox, then add the new feature key.

Options:

A.  

True

B.  

False

Discussion 0
Question # 5

In a Mobile VPN configuration, why would you choose default-route (full tunnel) VPN instead of split tunnel VPN? (Select one.)

Options:

A.  

Default-route VPN uses less bandwidth.

B.  

Default-route VPN enables your Firebox to examine all remote user traffic.

C.  

Default-route VPN uses less processing power.

D.  

Default-route VPN automatically allows dynamic NAT.

E.  

Default-route VPN is the only option you can use to apply security services to connections routed to your internal servers.

Discussion 0
Question # 6

If you have only one public IP address, can you use Static NAT to enable inbound connections to both an email server and a web server on the private network? (Select one.)

Options:

A.  

Yes, if both servers are on different private subnets

B.  

No, you must use Dynamic NAT to route inbound connections to more than one server

C.  

No, you must assign a public IP address to each server

D.  

Yes, if both servers use different ports

Discussion 0
Question # 7

What steps must you take to send log messages from a Firebox to WatchGuard Cloud? (Select two.)

Options:

A.  

Enable WatchGuard Cloud in the Firebox configuration

B.  

Add the FQDN of your WatchGuard Cloud account as a Log Server on the Firebox

C.  

Define an Authentication Key that all your Fireboxes use to communicate with WatchGuard Cloud

D.  

Configure Dimension to synchronize log messages with WatchGuard Cloud

E.  

Use the WatchGuard Cloud Add Device wizard to add the Firebox to WatchGuard Cloud

Discussion 0
Question # 8

What is true about this log message? (Select three.)

(Log context: Outbound HTTPS connection inspected through HTTPS-proxy with Application Control enabled, matching SNI inbox.google.com under TLS v1.3 and classified as Gmail)

Options:

A.  

The Application Control service has identified the traffic as Gmail

B.  

The traffic is allowed inbound through the Firebox

C.  

The HTTPS proxy identified a TLS v1.3 connection to the inbox.google.com SNI domain

D.  

The Gateway AntiVirus service denied the email traffic because it matches the 18.254 virus signature

E.  

The traffic is allowed outbound through the Firebox

Discussion 0
Question # 9

What type of NAT enables clients on a private network to connect to servers on the Internet? (Select one.)

Options:

A.  

Static NAT

B.  

Dynamic NAT

C.  

NAT loopback

D.  

Hairpin NAT

Discussion 0
Question # 10

You can add your Firebox to WatchGuard Cloud but continue to manage it locally. When you do this, what additional features does WatchGuard Cloud provide for your locally-managed Firebox? (Select two.)
Options:

A.  

Automatic Firebox firmware updates

B.  

Ability to schedule Firebox firmware updates

C.  

Real-time network traffic data

D.  

Unified event correlation and analysis

E.  

Live status and access to reports

Discussion 0

Network-Security-Essentials PDF

Network-Security-Essentials PDF (Printable)
$46.5
$154.99

Network-Security-Essentials Testing Engine

Network-Security-Essentials PDF (Printable)
$51
$169.99

Network-Security-Essentials PDF + Testing Engine

Network-Security-Essentials PDF (Printable)
$63.9
$212.99
Exams4sure Dumps

Exam style questions across every Network-Security-Essentials domain

Last Update 1 day ago
Total Questions : 60

Start with our free Network-Security-Essentials practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Locally-Managed Fireboxes exam. Each Network-Security-Essentials exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your WatchGuard weak domains, see where you're losing marks, and build a focused study plan in minutes.
Free Exams Sample Questions