Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Splunk Core Certified Power User Exam Practice Questions

Question # 11

What commands can be used to group events from one or more data sources?

Options:

A.  

eval, coalesce

B.  

transaction, stats

C.  

stats, format

D.  

top, rare

Discussion 0
Question # 12

Select this in the fields sidebar to automatically pipe you search results to the rare command

Options:

A.  

events with this field

B.  

rare values

C.  

top values by time

D.  

top values

Discussion 0
Question # 13

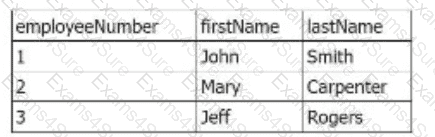
Two separate results tables are being combined using the join command. The outer table has the following values:

The inner table has the following values:
Question # 13

The line of SPL used to join the tables is: join employeeNumber type=outer

How many rows are returned in the new table?

Options:

A.  

Three

B.  

Eight

C.  

Five

D.  

Zero

Discussion 0
Question # 14

Which of the following statements describes this search?

sourcetype=access_combined I transaction JSESSIONID | timechart avg (duration)

Options:

A.  

This is a valid search and will display a timechart of the average duration, of each transaction event.

B.  

This is a valid search and will display a stats table showing the maximum pause among transactions.

C.  

No results will be returned because the transaction command must include the startswith and endswith options.

D.  

No results will be returned because the transaction command must be the last command used in the search pipeline.

Discussion 0
Question # 15

These kinds of charts represent a series in a single bar with multiple sections

Options:

A.  

Multi-Series

B.  

Split-Series

C.  

Omit nulls

D.  

Stacked

Discussion 0
Question # 16

In which Settings section are macros defined?

Options:

A.  

Fields

B.  

Tokens

C.  

Advanced Search

D.  

Searches, Reports, Alerts

Discussion 0
Question # 17

A user wants to convert numeric field values to strings and also to sort on those values.

Which command should be used first, the eval or the sort?

Options:

A.  

It doesn't matter whether eval or sort is used first.

B.  

Convert the numeric to a string with eval first, then sort.

C.  

Use sort first, then convert the numeric to a string with eval.

D.  

You cannot use the sort command and the eval command on the same field.

Discussion 0
Question # 18

When performing a regular expression (regex) field extraction using the Field Extractor (FX), what happens when the require option is used?

Options:

A.  

The regex can no longer be edited.

B.  

The field being extracted will be required for all future events.

C.  

The events without the required field will not display in searches.

D.  

Only events with the required string will be included in the extraction.

Discussion 0
Question # 19

Which of the following eval command functions is valid?

Options:

A.  

int()

B.  

count()

C.  

print()

D.  

tostring()

Discussion 0
Question # 20

In most large Splunk environments, what is the most efficient command that can be used to group events by fields/
Options:

A.  

join

B.  

stats

C.  

streamstats

D.  

transaction

Discussion 0

SPLK-1002 PDF

SPLK-1002 PDF (Printable)
$46.5
$154.99

SPLK-1002 Testing Engine

SPLK-1002 PDF (Printable)
$51
$169.99

SPLK-1002 PDF + Testing Engine

SPLK-1002 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions