
A security analyst notices that regardless of user-submitted prompts, an AI model always returns unsanitized responses. These responses are then passed to multiple plug-ins. The analyst is concerned with the potential security implications.
Which of the following Open Worldwide Application Security Project (OWASP) categories addresses this vulnerability?
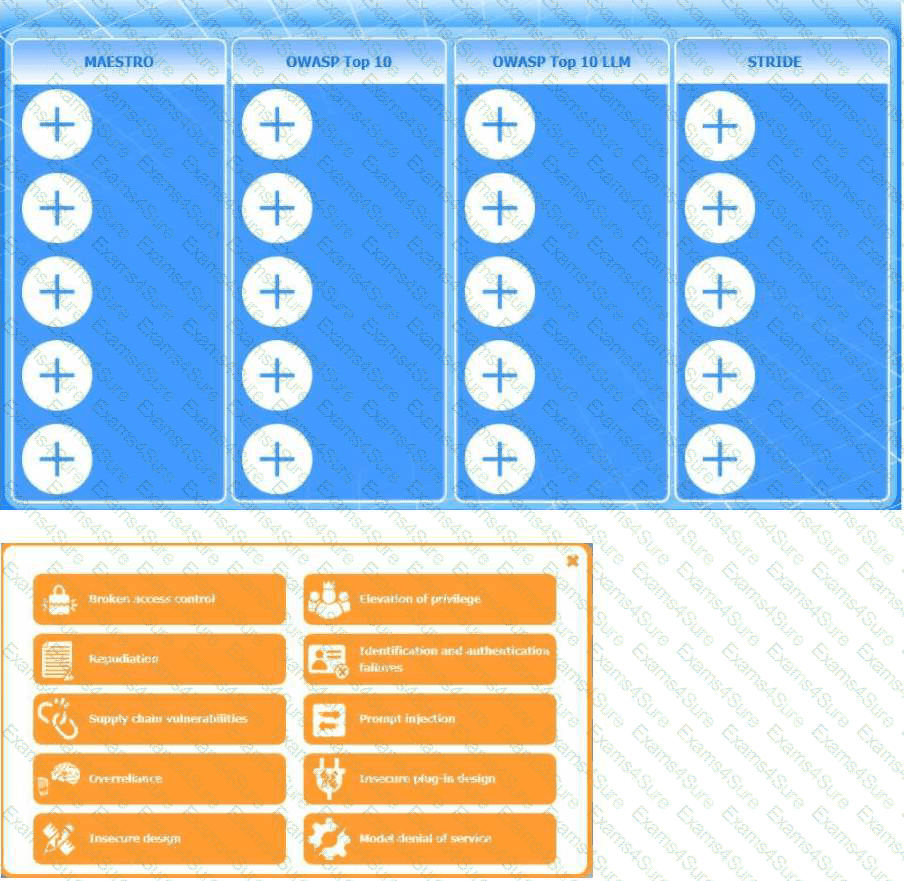
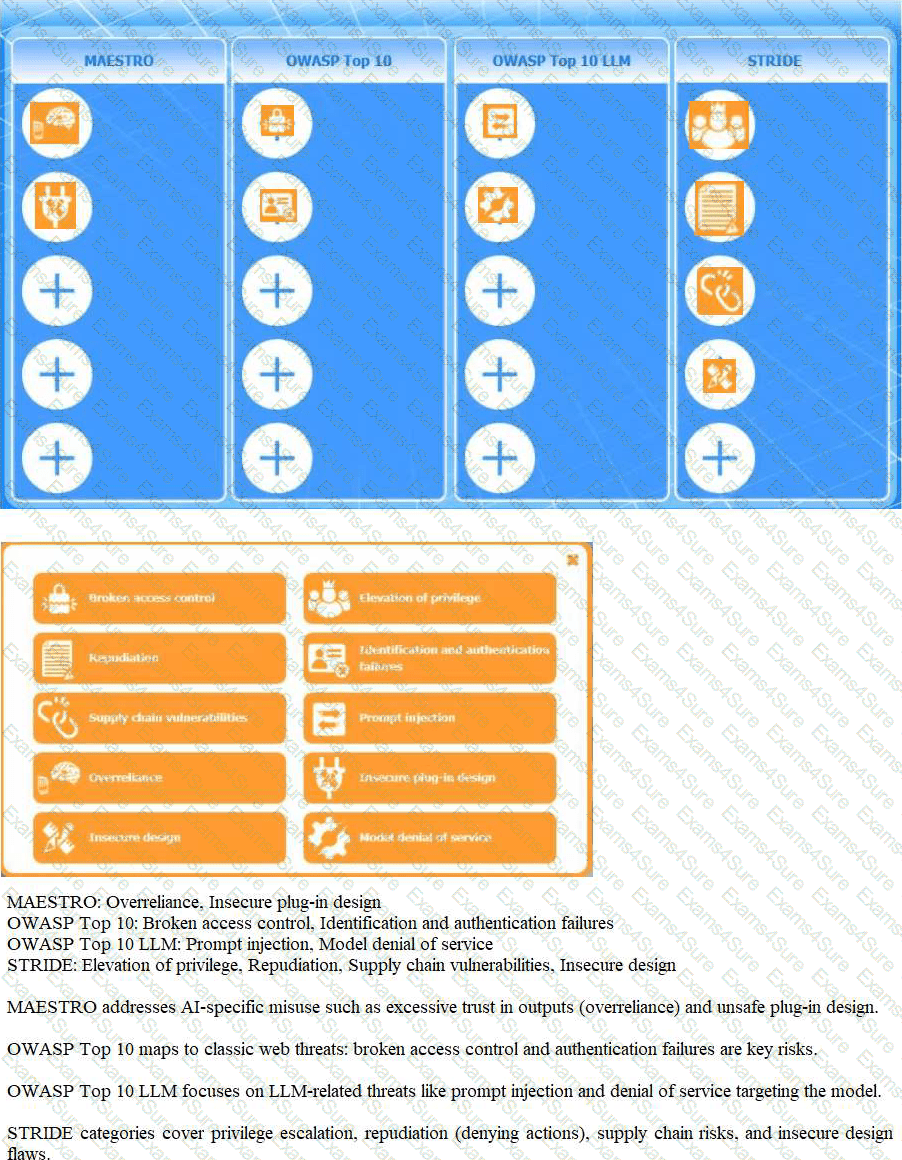
Instructions: Click the (+) to assign each threat category into its appropriate framework.
An architect is modeling an agentic system to meet security standards.
Which of the following should an auditor reference when reviewing a company ' s human resources AI systems for legal non-compliance?
An administrator, who works for a financial institution, is required to implement data security controls for data at rest within AI systems that involve data disclosure.
Which of the following is the most suitable control?
User experience is declining since the launch of a large language model (LLM) in internal networks.
Which of the following should be the highest priority for the prompt engineers?
Which of the following helps in managing potential security issues related to model training?




