

Exam style questions across every H12-841_V1.5 domain
Last Update 2 days ago
Total Questions : 104
Start with our free H12-841_V1.5 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real HCIP-Datacom exam. Each H12-841_V1.5 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Huawei weak domains, see where you're losing marks, and build a focused study plan in minutes.

(When a network device sends a registration request to iMaster NCE-Campus, which of the following is the destination port number?)
(When access authentication is deployed on a network, which of the following servers typically reside in the pre-authentication domain?)
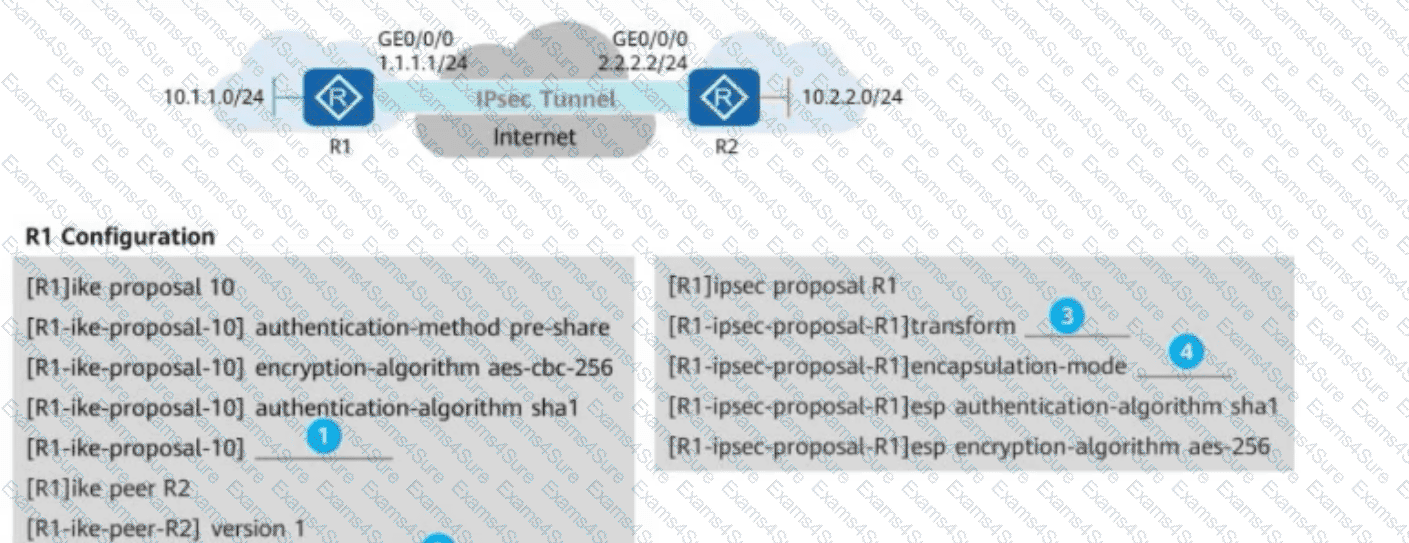
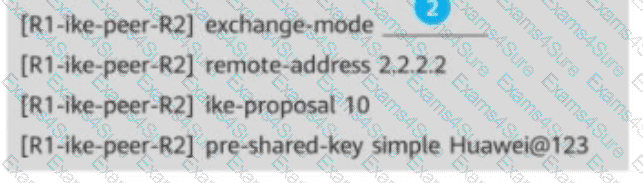
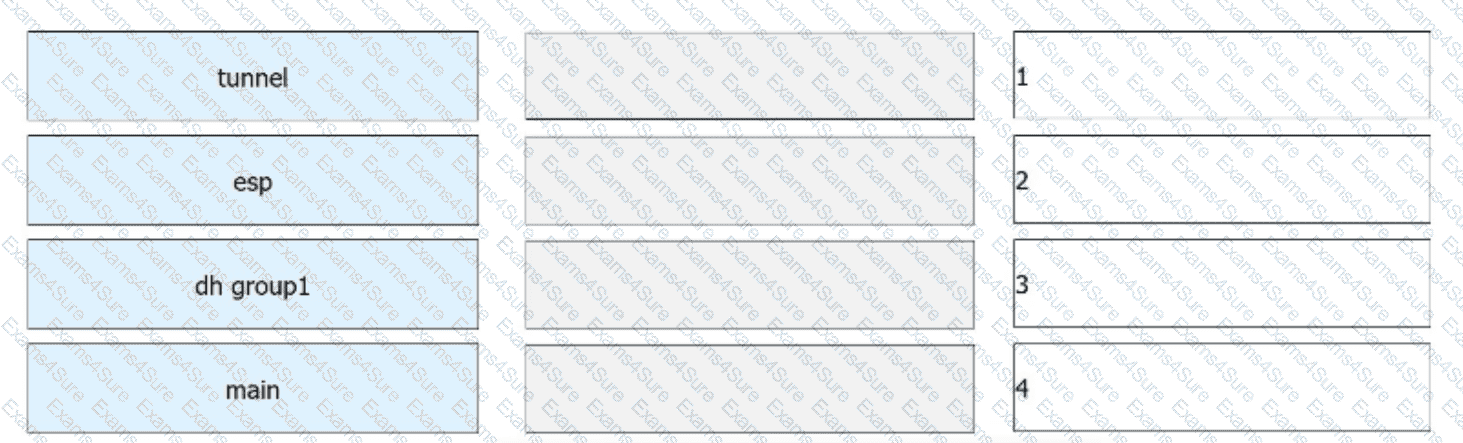
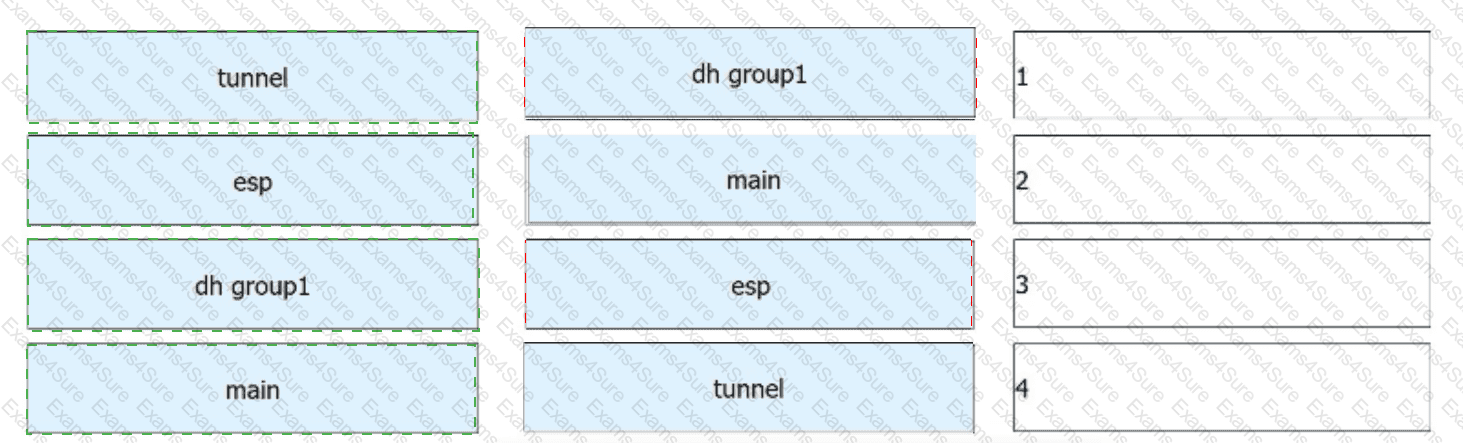
(As shown in the following figure, R1 and R2 establish an IPsec VPN in ISAKMP mode for communication. For IPsec proposals on R1 and R2, ESP is used, the encapsulation mode is set to tunnel mode, SHA1 is configured as the authentication algorithm, and AES-256 is configured as the encryption algorithm. In addition, IKEv1 is configured for IKE peers, the main mode is configured for IKEv1 negotiation phase 1, and the PSK Huawei@123 is configured for PSK authentication between IKE peers. For IKE proposals on R1 and R2, SHA1 is configured as the authentication algorithm, AES-256 is configured as the encryption algorithm, and DH group 1 is configured for IKE negotiation. Based on these configurations on R1 and R2, drag the configuration items on the left to the correct locations on the right.)
(Which of the following statements isfalseabout sites on a virtualized network deployed using iMaster NCE-Campus?)
(The egress zone is the boundary between a campus network and external networks, including the Internet and WAN. It bridges the intranet and extranet and protects the security of the campus network. Which of the following are requirements for egress zone design?)
(In the admission design for large- and medium-sized campus networks, which of the following authentication modes can be used for PCs connected to IP phones?)
(Which of the following is not one of the three roles defined in policy association?)
(On a CloudCampus virtualized campus network, which of the following modes can be used by a fabric to connect to external networks?Choose all that apply.)
(In Huawei's free mobility solution, after receiving user traffic, the policy enforcement device searches for the corresponding policy based on the information carried in the traffic, and enforces the policy to forward or discard the traffic. What is the information carried in the traffic?)
(Huawei switches support VLAN assignment based on interface, MAC address, protocol, and IP address.)



