
Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Security, Specialist (JNCIS-SEC) Practice Questions

Question # 11

Which two statements accurately describe the role of hashing in VPNs? (Choose two.)

Options:

A.  

Hashing compresses data in VPN communications.

B.  

Hashing generates a fixed-size string of characters.

C.  

Hashing encrypts data to ensure confidentiality.

D.  

Hashing verifies that data has not been altered during transmission.

Discussion 0
Question # 12

In Juniper high availability (HA) SRX Series device implementations, which interface will be used to exchange session state, configuration files, and ensure session continuity across nodes using the proprietary Trivial Network Protocol?

Options:

A.  

fab

B.  

fxp0

C.  

fxp1

D.  

swfab

Discussion 0
Question # 13

Which two statements about proxy IDs are correct? (Choose two.)

Options:

A.  

Proxy IDs cannot override default Junos behavior.

B.  

By default, for a route-based IPsec VPN, a Junos security device sets the proxy ID to 0.0.0.0/0.

C.  

Proxy IDs must match on both peers for a Phase 2 tunnel to establish.

D.  

Proxy IDs are created during IKE Phase 1.

Discussion 0
Question # 14

What are two ways to help reduce false positives for an IDP rule? (Choose two.)

Options:

A.  

Change the rule to a lower severity action.

B.  

Remove the attack object from the rule.

C.  

Create an exempt rule.

D.  

Configure a terminal rule at the end of the rule base.

Discussion 0
Question # 15

You are implementing an SRX Series device at a branch office that has low bandwidth and also uses a cloud-based VoIP solution with an outbound policy that permits all traffic.

Which service would you implement at your edge device to prioritize VoIP traffic in this scenario?

Options:

A.  

AppFW

B.  

SIP ALG

C.  

AppQoE

D.  

AppQoS

Discussion 0
Question # 16

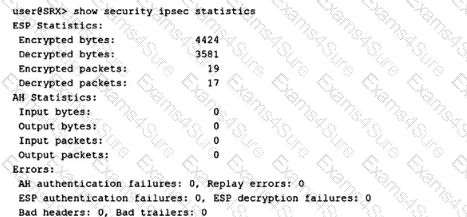
What does the exhibit indicate when you have configured a single IPsec VPN on an SRX Series Firewall?
Question # 16

Options:

A.  

The IPsec VPN has encountered errors during packet transmission.

B.  

The IPsec VPN is established, and traffic is passing through.

C.  

The IPsec VPN is not established.

D.  

The IPsec VPN is established, but no traffic is passing through.

Discussion 0
Question # 17

You need to secure communications from a mobile command center which uses a 5G mobile ISP behind CGNAT to an SRX Series Firewall at headquarters.

Which two actions should be performed on the SRX Series Firewall in this scenario? (Choose two.)

Options:

A.  

Configure the IPsec VPN to use NAT-T.

B.  

Configure the IPsec VPN to use IKEv1 aggressive mode.

C.  

Configure the IPsec VPN to use IKEv2 aggressive mode.

D.  

Configure the IPsec VPN to use DP

D.  

Discussion 0
Question # 18

An administrator decides to designate a node as the primary node for the chassis cluster.

Which statement is correct in this scenario?

Options:

A.  

Configure the burnt-in-address (BIA) to the highest value to bring the node as the primary node.

B.  

The node with the highest priority will become a primary node.

C.  

The node with the lowest priority will become a primary node.

D.  

Nodes with a priority of one are ineligible to participate in the election process.

Discussion 0
Question # 19

Which SRX Series device configuration setting must be configured first to use Juniper ATP Cloud?

Options:

A.  

Start up the anti-malware service on the SRX Series device.

B.  

Apply the firewall rules on the SRX Series device.

C.  

Enable connectivity between the SRX Series device and Juniper ATP Cloud.

D.  

Configure the anti-malware policies on the SRX Series device.

Discussion 0
Question # 20

Which two statements are correct about Juniper ATP Cloud malware analysis? (Choose two.)

Options:

A.  

If no match exists in cache, the remaining analysis features are processed with the cumulative threat score transmitted to the SRX Series device.

B.  

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis continues.

C.  

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis stops.

D.  

If no match exists in cache, the first analysis feature to generate a threat score is transmitted to the SRX Series device.

Discussion 0

JN0-336 PDF

JN0-336 PDF (Printable)
$54.25
$154.99

JN0-336 Testing Engine

JN0-336 PDF (Printable)
$59.5
$169.99

JN0-336 PDF + Testing Engine

JN0-336 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions


