Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Fortinet NSE 4 - FortiOS 7.2 Practice Questions

Exams4sure Dumps

Exam style questions across every NSE4_FGT-7.2 domain

Last Update 2 days ago
Total Questions : 170

Start with our free NSE4_FGT-7.2 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real NSE4 exam. Each NSE4_FGT-7.2 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE4_FGT-7.2 PDF

NSE4_FGT-7.2 PDF (Printable)
$54.25
$154.99

NSE4_FGT-7.2 Testing Engine

NSE4_FGT-7.2 PDF (Printable)
$59.5
$169.99

NSE4_FGT-7.2 PDF + Testing Engine

NSE4_FGT-7.2 PDF (Printable)
$74.55
$212.99
Question # 1

Refer to the exhibit.

Question # 1

Question # 1

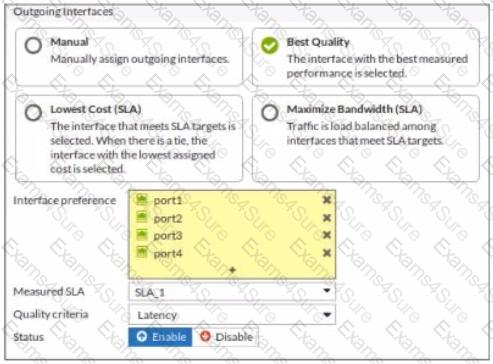
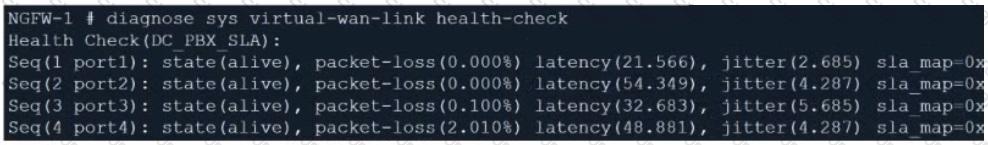
The exhibit contains the configuration for an SD-WAN Performance SLA, as well as the output of diagnose sys virtual-wan-link health-check . Which interface will be selected as an outgoing interface?

Options:

A.  

port2

B.  

port4

C.  

port3

D.  

port1

Discussion 0
Question # 2

Refer to the exhibit.

The exhibit shows the output of a diagnose command.
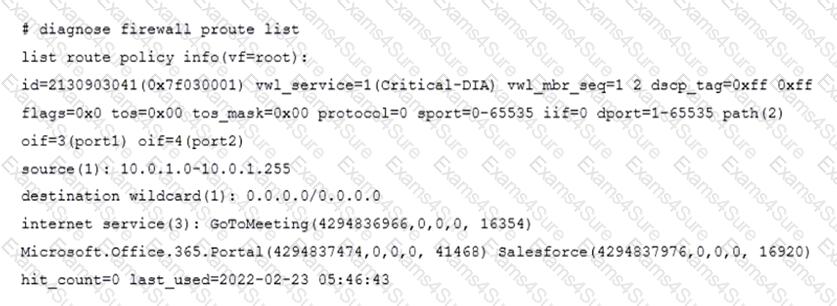
Question # 2

What does the output reveal about the policy route?

Options:

A.  

It is an ISDB route in policy route.

B.  

It is a regular policy route.

C.  

It is an ISDB policy route with an SDWAN rule.

D.  

It is an SDWAN rule in policy route.

Discussion 0
Question # 3

Options:

Discussion 0
Question # 4

Which two types of traffic are managed only by the management VDOM? (Choose two.)

Options:

A.  

FortiGuard web filter queries

B.  

PKI

C.  

Traffic shaping

D.  

DNS

Discussion 0
Question # 5

62

Which two policies must be configured to allow traffic on a policy-based next-generation firewall (NGFW) FortiGate? (Choose two.)

C.  

Security policy

D.  

SSL inspection and authentication policy

Options:

Discussion 0
Question # 6

Refer to the exhibit.

Question # 6

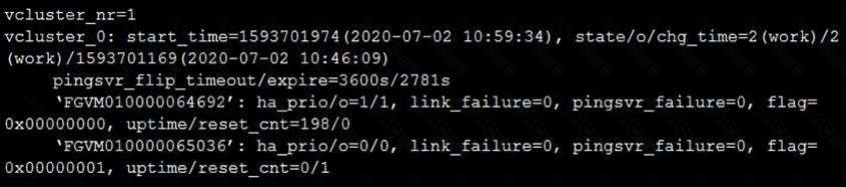
The exhibit displays the output of the CLI command: diagnose sys ha dump-by vcluster.

Which two statements are true? (Choose two.)

Options:

A.  

FortiGate SN FGVM010000065036 HA uptime has been reset.

B.  

FortiGate devices are not in sync because one device is down.

C.  

FortiGate SN FGVM010000064692 is the primary because of higher HA uptime.

D.  

FortiGate SN FGVM010000064692 has the higher HA priority.

Discussion 0
Question # 7

17

In consolidated firewall policies, IPv4 and IPv6 policies are combined in a single consolidated policy. Instead of separate policies. Which three statements are true about consolidated IPv4 and IPv6 policy configuration? (Choose three.)

Options:

A.  

The IP version of the sources and destinations in a firewall policy must be different.

B.  

The Incoming Interface. Outgoing Interface. Schedule, and Service fields can be shared with both IPv4 and IPv6.

C.  

The policy table in the GUI can be filtered to display policies with IPv4, IPv6 or IPv4 and IPv6 sources and destinations.

D.  

The IP version of the sources and destinations in a policy must match.

E.  

The policy table in the GUI will be consolidated to display policies with IPv4 and IPv6 sources and destinations.

Discussion 0
Question # 8

Refer to the exhibit to view the application control profile.
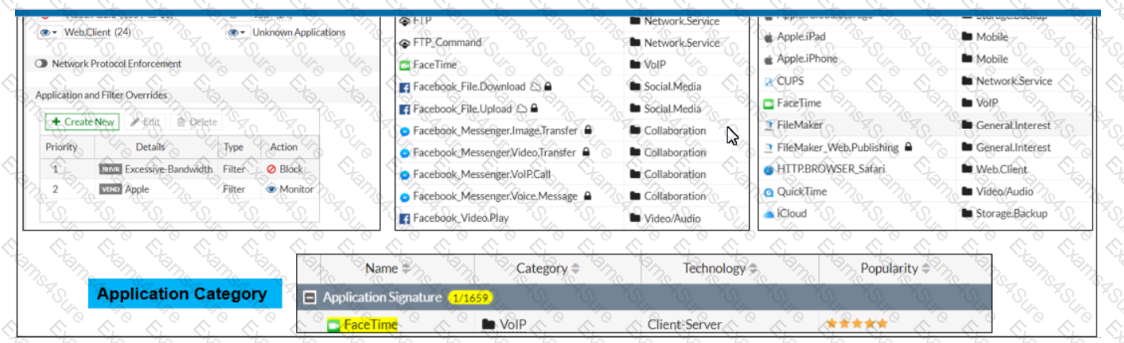
Question # 8

Based on the configuration, what will happen to Apple FaceTime?

Options:

A.  

Apple FaceTime will be blocked, based on the Excessive-Bandwidth filter configuration

B.  

Apple FaceTime will be allowed, based on the Apple filter configuration.

C.  

Apple FaceTime will be allowed only if the filter in Application and Filter Overrides is set to Learn

D.  

Apple FaceTime will be allowed, based on the Categories configuration.

Discussion 0
Question # 9

17

Refer to the exhibit.

Question # 9

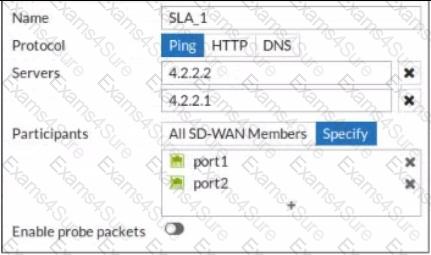
An administrator has configured a performance SLA on FortiGate, which failed to generate any traffic.

Why is FortiGate not sending probes to 4.2.2.2 and 4.2.2.1 servers? (Choose two.)

Options:

A.  

The Detection Mode setting is not set to Passive.

B.  

Administrator didn't configure a gateway for the SD-WAN members, or configured gateway is not valid.

C.  

The configured participants are not SD-WAN members.

D.  

The Enable probe packets setting is not enabled.

Discussion 0
Question # 10

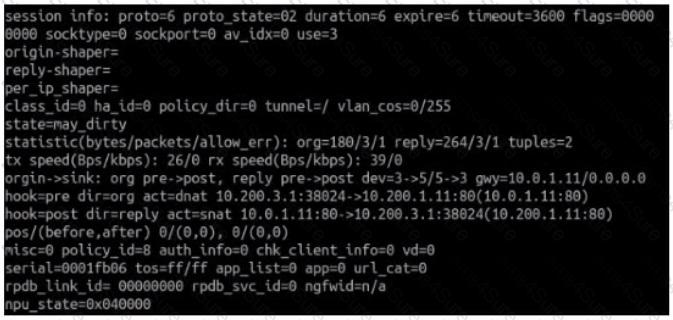
Refer to the exhibit.

Question # 10

Which contains a session diagnostic output. Which statement is true about the session diagnostic output?


Options:

A.  

The session is in SYN_SENT state.

B.  

The session is in FIN_ACK state.

C.  

The session is in FTN_WAIT state.

D.  

The session is in ESTABLISHED state.

Discussion 0

Free Exams Sample Questions