Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Fortinet NSE 5 - FortiNAC-F 7.6 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE5_FNC_AD_7.6 domain

Last Update 2 days ago
Total Questions : 59

Start with our free NSE5_FNC_AD_7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Network Security Expert exam. Each NSE5_FNC_AD_7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE5_FNC_AD_7.6 PDF

NSE5_FNC_AD_7.6 PDF (Printable)
$54.25
$154.99

NSE5_FNC_AD_7.6 Testing Engine

NSE5_FNC_AD_7.6 PDF (Printable)
$59.5
$169.99

NSE5_FNC_AD_7.6 PDF + Testing Engine

NSE5_FNC_AD_7.6 PDF (Printable)
$74.55
$212.99
Question # 1

Question # 1

Question # 1

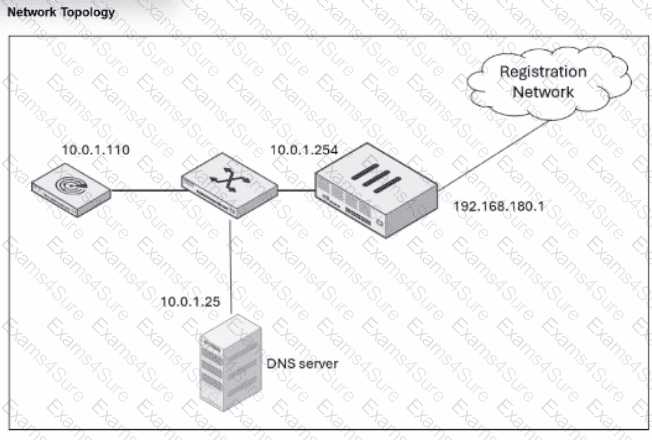
An administrator has configured the DHCP scope for a registration isolation network, but the isolation process isn ' t working.

What is the problem with the configuration?

Options:

A.  

The domain name server designation is incorrect.

B.  

The label uses a system-reserved value.

C.  

The lease pool does not contain a complete subnet.

D.  

The gateway defined for the scope is incorrect.

Discussion 0
Question # 2

As part of a company policy, all end stations must be scanned for compliance each day. The security administrators want to satisfy this requirement without any necessary interaction from the end user. Which two agents can provide that functionality? (Choose two.)

Options:

A.  

Dissolvable

B.  

Persistent

C.  

Passive

D.  

Mobile

Discussion 0
Question # 3

When configuring isolation networks in the configuration wizard, why does a layer 3 network typo allow for mora than ono DHCP scope for each isolation network typo?

Options:

A.  

The layer 3 network type allows for one scope for each possible host status.

B.  

Configuring more than one DHCP scope allows for DHCP server redundancy

C.  

There can be more than one isolation network of each type

D.  

Any scopes beyond the first scope are used if the initial scope runs out of IP addresses.

Discussion 0
Question # 4

Refer to the exhibits.

Question # 4

Question # 4

Question # 4

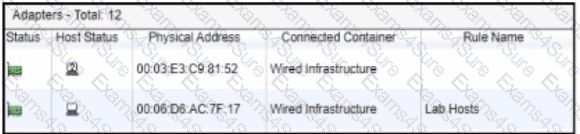
An administrator is troubleshooting visibility issues on a modeled switch The switch is configured to use link traps and to provision hosts based on network access policies. The administrator is seeing hosts on ports with no hosts connected and not seeing hosts on ports where hosts are known to be connected.

What is the most likely cause?

Options:

A.  

The logical networks are set to deny.

B.  

The host has uninstalled the FortiNAC-F agent.

C.  

The switch cannot be contacted by FortiNAC-F

D.  

The credentials are incorrect.

Discussion 0
Question # 5

Refer to the exhibit.

Question # 5

After a successful layer 2 poll, two hosts were learned on the same port The port is a member of the Role-Based Access and Forced Registration groups. The switch has been configured to leverage a single isolation VLAN.

How will FortiNAC-F manage this port?

Options:

A.  

The port will be provisioned to the isolation network

B.  

The port will be provisioned for the normal state host, but the second host will have access to only the isolation portal page.

C.  

The port will be provisioned as an uplink to a hub or unmanaged switch.

D.  

The port will be added to the Access Point Management group

Discussion 0
Question # 6

Which two statements are true about integrating a third-party device using SNMP traps from that device as input to generate an event? (Choose two.)

Options:

A.  

The sending device must be modeled in the inventory topology.

B.  

The sending device must support SNMPv3.

C.  

set allowaccess snmp must be configured using the CLI on the FortiNAC-F receiving interface.

D.  

The IP address OID and MAC address OID must be configured in the trap MIB file.

Discussion 0
Question # 7

As part of a FortiNAC-F integration with FortiGate for management of VPN users, what must be configured on FortiGate to keep FortiNAC-F up to date with VPN session information?

Options:

A.  

SNMP traps

B.  

RADIUS accounting

C.  

Security Fabric integration

D.  

Syslog messages

Discussion 0
Question # 8

Refer to the exhibit.

Question # 8

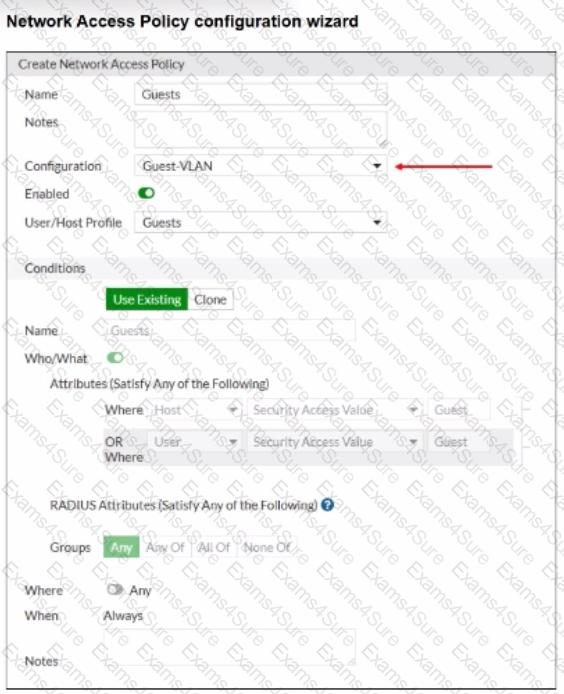
When configuring guest access using a network access policy, where would an administrator configure the Guest-VLAN value?

Options:

A.  

In the Model configuration

B.  

In the Guest template

C.  

In the User/Host profile

D.  

in the Guest portal configuration

Discussion 0
Question # 9

An administrator has created several device profiling rules and evaluated all existing devices in the database. Some of the devices appear in the profiled devices view because they matched a rule, but they remain unknown and the registration column in the profiled devices view shows " No " .

What is the most likely cause?

Options:

A.  

The confirm device profiling rule option is not enabled.

B.  

The devices match more than one device profiling rule.

C.  

The device profiling rule has registration set to manual.

D.  

The devices have persistent agents installed, and the point of connection has PA optimization enabled.

Discussion 0
Question # 10

In which three ways would deploying a FortiNAC-F Manager into a large environment consisting of several FortiNAC-F CAs simplify management? (Choose three.)


Options:

A.  

Global infrastructure device inventory

B.  

Global version control

C.  

Global authentication security policies

D.  

Pooled licenses

E.  

Global visibility

Discussion 0

Free Exams Sample Questions