Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Fortinet NSE 6 - FortiEDR 7.0 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE6_EDR_AD-7.0 domain

Last Update 11 hours ago
Total Questions : 33

Start with our free NSE6_EDR_AD-7.0 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real NSE 6 Network Security Specialist exam. Each NSE6_EDR_AD-7.0 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE6_EDR_AD-7.0 PDF

NSE6_EDR_AD-7.0 PDF (Printable)
$54.25
$154.99

NSE6_EDR_AD-7.0 Testing Engine

NSE6_EDR_AD-7.0 PDF (Printable)
$59.5
$169.99

NSE6_EDR_AD-7.0 PDF + Testing Engine

NSE6_EDR_AD-7.0 PDF (Printable)
$74.55
$212.99
Question # 1

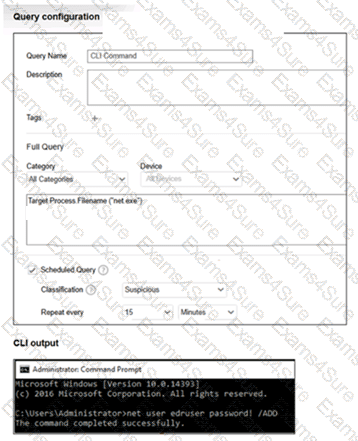
Refer to the exhibits.

Question # 1

What happens when the net user command runs on an endpoint? (Choose one answer)

Options:

A.  

It triggers an immediate endpoint alert.

B.  

It blocks CLI commands by default.

C.  

It triggers an incident when the query matches the target process (net.exe).

D.  

It triggers FortiEDR rules because the activity is not suspicious.

Discussion 0
Question # 2

A playbook is configured with two actions: terminate process and isolate device. The terminate process action fails because the process is protected by Windows. What is the expected behavior for the second action, isolate device? (Choose one answer)

Options:

A.  

The playbook execution pauses and requires administrator intervention.

B.  

The playbook generates a notification email and execution stops.

C.  

The playbook execution stops because the action fails.

D.  

The playbook continues and executes the second action.

Discussion 0
Question # 3

Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)

Options:

A.  

%upload_file

B.  

%ipconfig_all

C.  

%psexec

D.  

%timestamp

Discussion 0
Question # 4

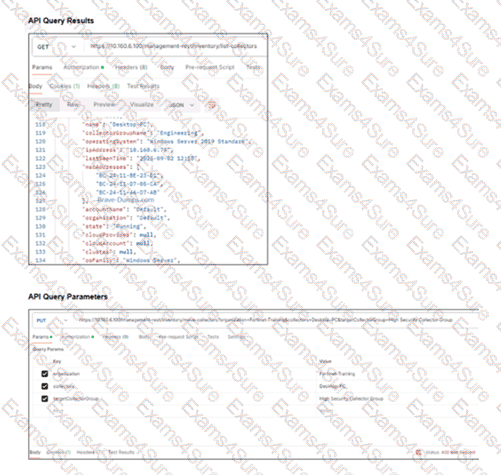
Refer to the exhibits.

Question # 4

You are attempting to move a collector into the High Security Collector Group for isolation but encounter an error in the API request as shown in the exhibit. To successfully isolate the collector, which API parameter must you correct? (Choose one answer)

Options:

A.  

Set the organization parameter to Default.

B.  

Update the authorization credentials in the API header.

C.  

Change the HTTP method in the request from PUT to POST.

D.  

Set the target collector group parameter to Engineering group.

Discussion 0
Question # 5

You discovered that a newly installed collector does not display on the Inventory tab in the central manager. Which two troubleshooting steps must you perform? (Choose two answers)

Options:

A.  

Verify that the central manager can resolve the collector hostname through DNS.

B.  

Verify that TCP ports 8081 and 555 are open between the collector and the central manager.

C.  

Check whether the FortiEDR services are running on the collector device.

D.  

Export and review the collector logs from the Central Manager for connection errors.

Discussion 0
Question # 6

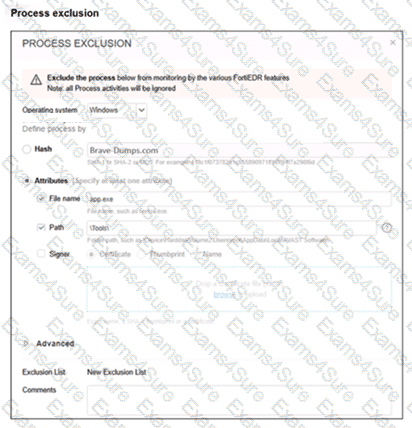
Refer to the exhibit:

Question # 6

You configured an execution prevention exclusion with both File Name = app.exe and Path = C:\Tools. What will FortiEDR do? (Choose one answer)

Options:

A.  

Exclude only signed versions of app.exe.

B.  

Exclude only app.exe when it is running from C:\Tools.

C.  

Exclude app.exe whenever it appears.

D.  

Exclude all files in C:\Tools.

Discussion 0
Question # 7

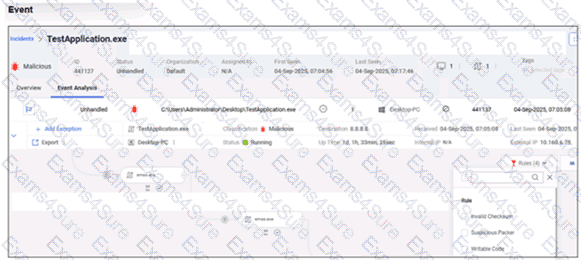
Refer to the exhibit.

Question # 7

Based on the event shown in the exhibit, which two statements about the event are true? (Choose two answers)

Options:

A.  

The event is marked as Handled.

B.  

FCS classified the event as malicious.

C.  

The user was able to launch TestApplication.exe.

D.  

TestApplication.exe is sophisticated malware.

Discussion 0
Question # 8

Within the FortiEDR architecture, which component needs JumpBox capabilities to enable authenticated and controlled communication with FortiAnalyzer? (Choose one answer)

Options:

A.  

Core

B.  

Central manager

C.  

Aggregator

D.  

Reputation Server

Discussion 0
Question # 9

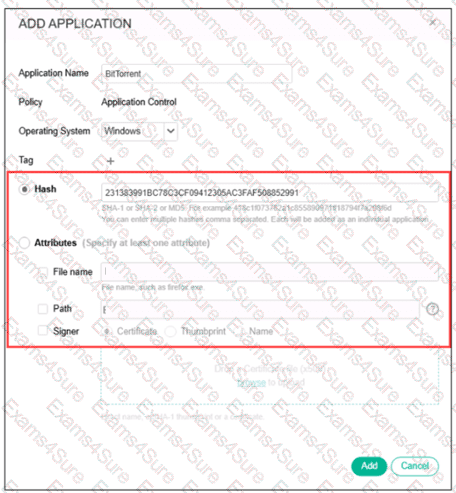
Refer to the exhibit:

Question # 9

You are asked to block applications based on hash attributes. Which two factors must you consider when applying the hash value? (Choose two answers)


Options:

A.  

Hashes must be line-separated.

B.  

Hashes must be used with at least one attribute, such as a filename or path.

C.  

Hashes must be unique to each application.

D.  

Hashes must follow supported formats.

Discussion 0

Free Exams Sample Questions