Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Fortinet NSE 6 - FortiManager 7.6 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE6_FMG_AD-7.6 domain

Last Update 2 days ago
Total Questions : 65

Start with our free NSE6_FMG_AD-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real NSE 6 Network Security Specialist exam. Each NSE6_FMG_AD-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE6_FMG_AD-7.6 PDF

NSE6_FMG_AD-7.6 PDF (Printable)
$54.25
$154.99

NSE6_FMG_AD-7.6 Testing Engine

NSE6_FMG_AD-7.6 PDF (Printable)
$59.5
$169.99

NSE6_FMG_AD-7.6 PDF + Testing Engine

NSE6_FMG_AD-7.6 PDF (Printable)
$74.55
$212.99
Question # 11

What allows FortiManager to run CLI scripts on FortiGate devices without prompting for SSH authentication each time?

Options:

A.  

FortiGate devices using the legacy login method.

B.  

The secure management tunnel between FortiManager and FortiGate devices.

C.  

The script using the Remote FortiGate Directly via CLI option.

D.  

The script on the FortiManager device database.

Discussion 0
Question # 12

What is the purpose of ADOM revisions?

Options:

A.  

ADOM revisions find unused, duplicate, and unnecessary firewall policies and objects.

B.  

ADOM revisions show specific changes in a policy package when it is installed.

C.  

ADOM revisions compare previous snapshots of the Policy Package and ADOM-level objects with the device-level database.

D.  

ADOM revisions save the current state of all policy packages and objects for an ADOM.

Discussion 0
Question # 13

Which two conditions trigger FortiManager to create a new revision history? (Choose two.)

Options:

A.  

When FortiManager installs device-level changes on a managed device

B.  

When changes to the device-level database are made on FortiManager

C.  

When FortiManager is auto-updated with configuration changes made directly on a managed device

D.  

When a provisioning template is assigned to a managed device on the device-level database

Discussion 0
Question # 14

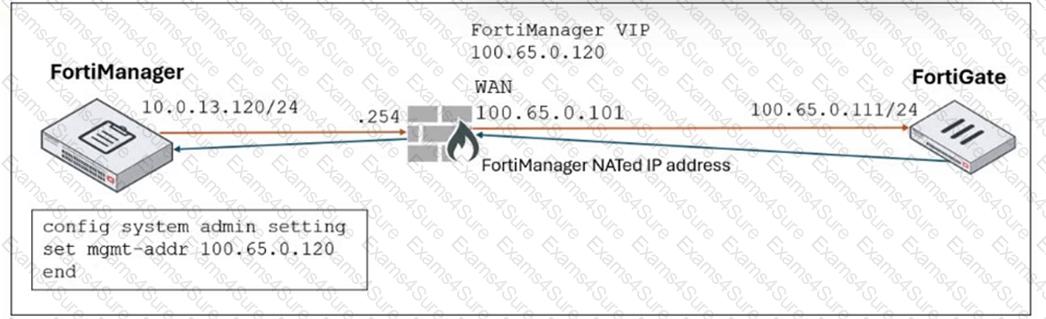
Refer to the exhibit.

Question # 14

FortiManager is operating behind a network address translation (NAT) device, and the administrator configured the FortiManager NATed IP address under the FortiManager system administration settings.

What is the expected result during discovery?

Options:

A.  

FortiManager sets both the 100.65.0.120 IP address and 10.0.13.120 IP address on FortiGate.

B.  

FortiManager sets both the 100.65.0.120 IP address and 100.65.0.101 IP address on FortiGate.

C.  

FortiManager sets the 100.65.0.101 IP address on FortiGate.

D.  

FortiManager sets the 100.65.0.120 IP address on FortiGate.

Discussion 0
Question # 15

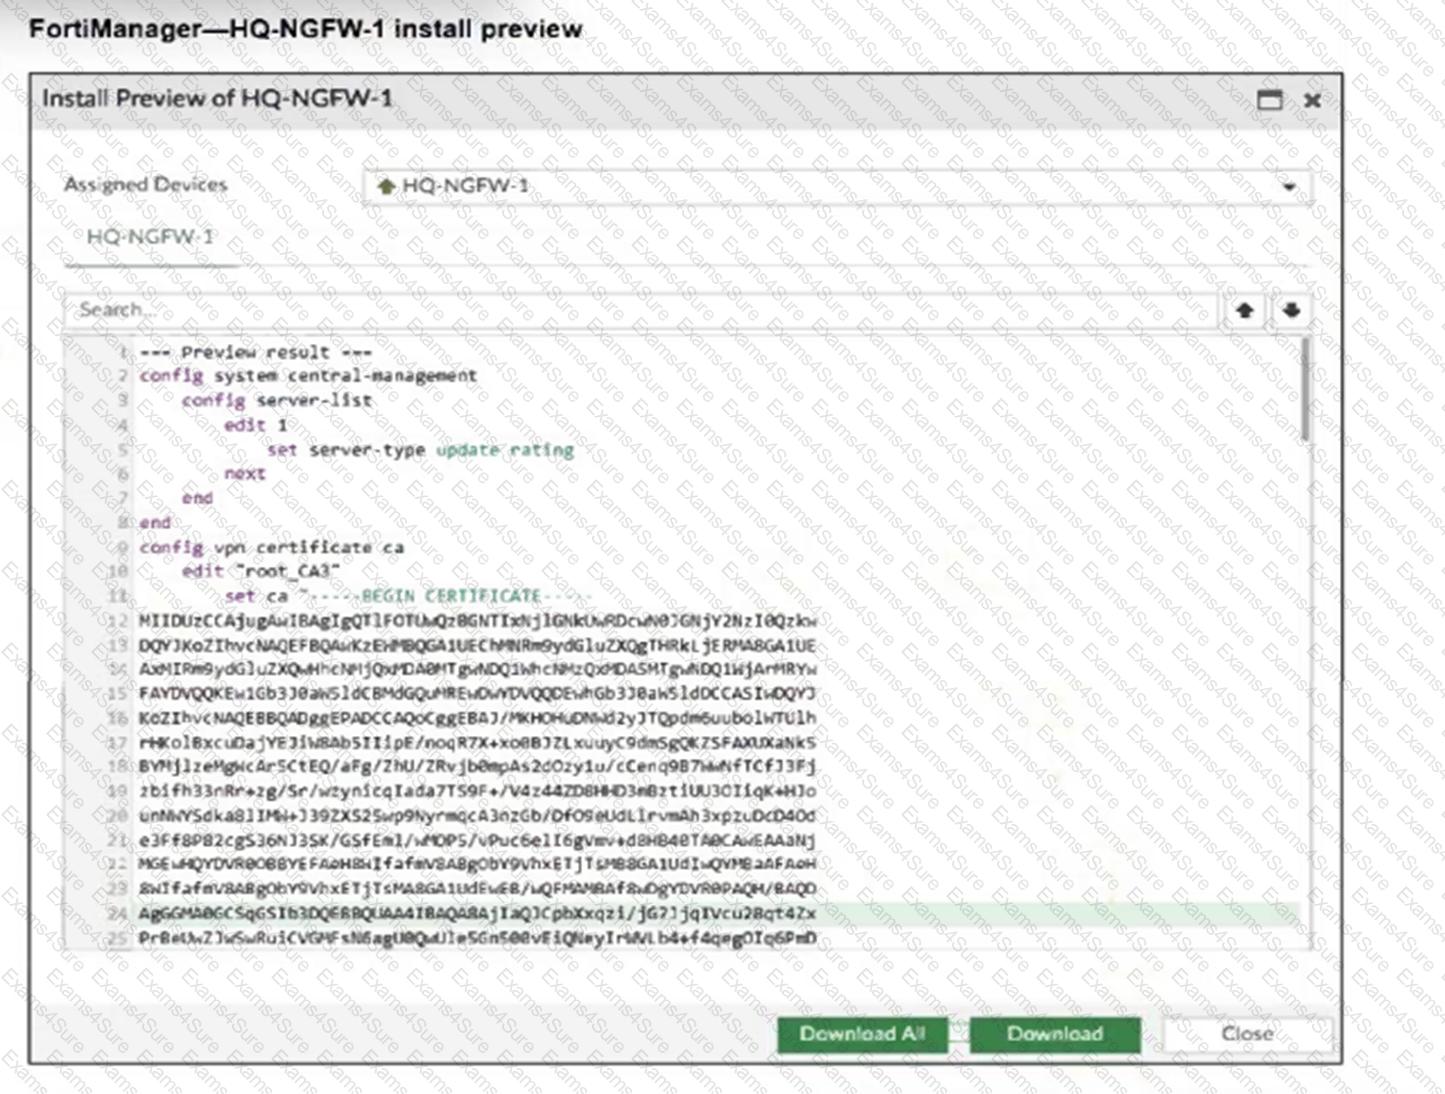
Refer to the exhibit.

Question # 15

An administrator assigned a new policy package to FortiGate HQ-NGFW-1. In the installation preview, they noticed some settings they did not modify and are unsure about the changes.

Based on the exhibit, which two things will happen if they continue with the installation? (Choose two.)

Options:

A.  

FortiGate HQ-NGFW-1 can use FortiManager firmware templates to upgrade firmware and ratings.

B.  

FortiGate HQ-NGFW-1 can contact the FortiManager acting as FortiGuard Distribution Server (FDS) to download FortiGuard updates.

C.  

FortiGate HQ-NGFW-1 will use the root_CA3 certificate in firewall address objects or policies.

D.  

FortiManager will install the CA certificate named root_CA3 to authenticate FortiGate-to-FortiManager communication protocol (FGFM) tunnel connections with FortiGate HQ- NGFW-1.

Discussion 0
Question # 16

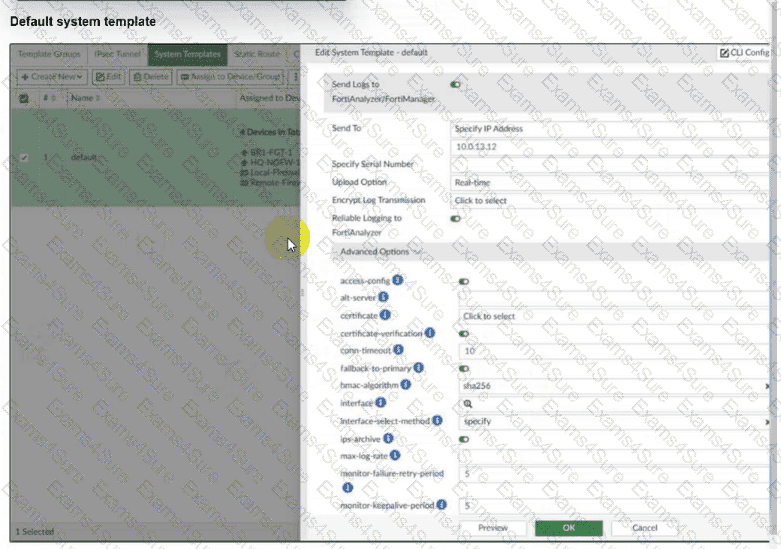
Refer to the exhibit.

Question # 16

An administrator has assigned the default system template to install all devices with the FortiAnalyzer IP address 10.0.13.12. However, not all FortiGate devices can reach FortiAnalyzer using the default interface. Some devices may use the LAN interface, while others may use the WAN interface. How can the administrator change the source interface for FortiGate devices using the default system template? Choose one answer

Options:

A.  

Use per-device dynamic object configurations at the ADOM level and apply them in the template.

B.  

Configure a metadata variable at the ADOM level and use it in the template.

C.  

Create a different system template for each FortiGate, if the configuration is different.

D.  

Create a meta field on FortiManager system settings of type Device and use it in the template.

Discussion 0
Question # 17

A service provider administrator has assigned a global policy package to a managed customer ADOM named My_ADOM. The customer administrator has access only to My_ADOM.

How can the customer administrator edit the global header policy of the global policy package?

Options:

A.  

The customer administrator can edit the header policy by using workspace mode on the global ADOM.

B.  

The customer administrator can edit the header policy by using workflow mode on the global ADOM and My_ADOM.

C.  

The service provider administrator can unlock the global policy from the global ADOM to authorize changes to the customer administrator.

D.  

The customer administrator cannot edit the global header policy; only the service provider administrator can make changes from the global ADOM.

Discussion 0
Question # 18

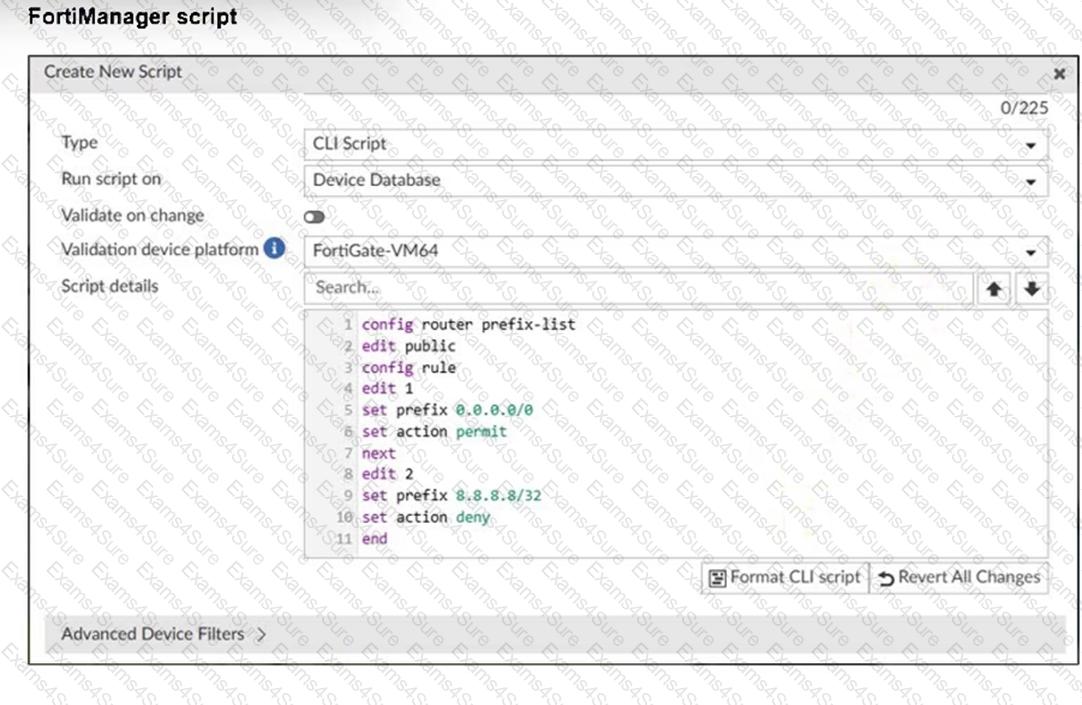
Refer to the exhibit.

Question # 18

Which two results occur if you run the script using the Device Database option? (Choose two.)

Options:

A.  

The device Config Status is tagged as Modified.

B.  

The script history shows the successful installation of the script on the remote FortiGate.

C.  

The successful execution of a script on the Device Database creates a new revision history.

D.  

The administrator must install these changes on a managed device using the Install Wizard.

Discussion 0
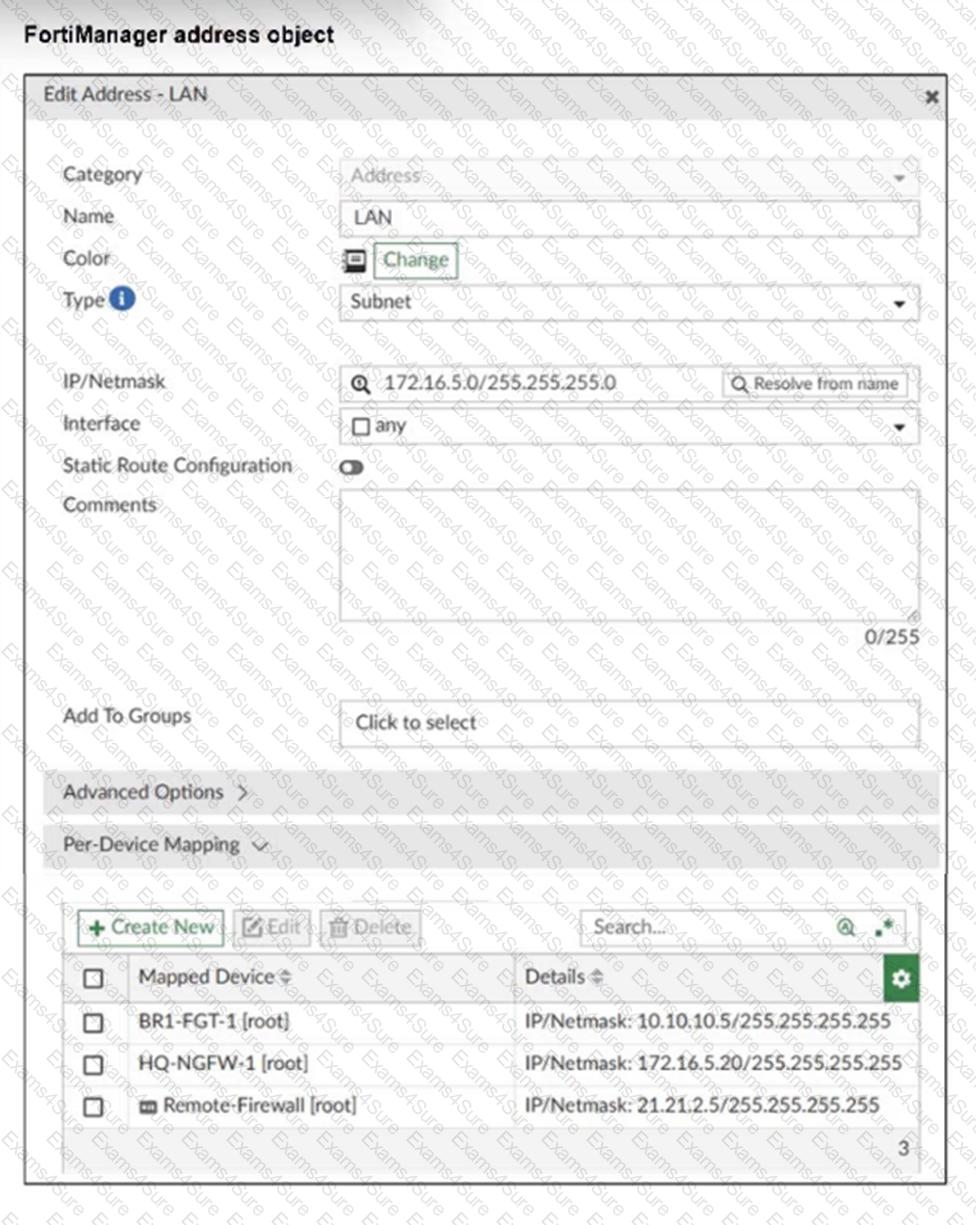
Question # 19

Refer to the exhibit.

Question # 19

An administrator has created a firewall address object that is used in multiple policy packages for multiple FortiGate devices in an ADOM.

After the installation operation is performed, which IP/netmask will be installed on Remote-Firewall [VDOM1] for the LAN firewall address object?


Options:

A.  

21.21.2.5/255.255.255.255

B.  

172.16.5.20/255.255.255.255

C.  

172.16.5.0/255.255.255.0

D.  

10.10.10.5/255.255.255.255

Discussion 0

Free Exams Sample Questions