Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE6_SDW_AD-7.6 domain

Last Update 1 day ago
Total Questions : 96

Start with our free NSE6_SDW_AD-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Network Security Expert exam. Each NSE6_SDW_AD-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE6_SDW_AD-7.6 PDF

NSE6_SDW_AD-7.6 PDF (Printable)
$46.5
$154.99

NSE6_SDW_AD-7.6 Testing Engine

NSE6_SDW_AD-7.6 PDF (Printable)
$51
$169.99

NSE6_SDW_AD-7.6 PDF + Testing Engine

NSE6_SDW_AD-7.6 PDF (Printable)
$63.9
$212.99
Question # 1

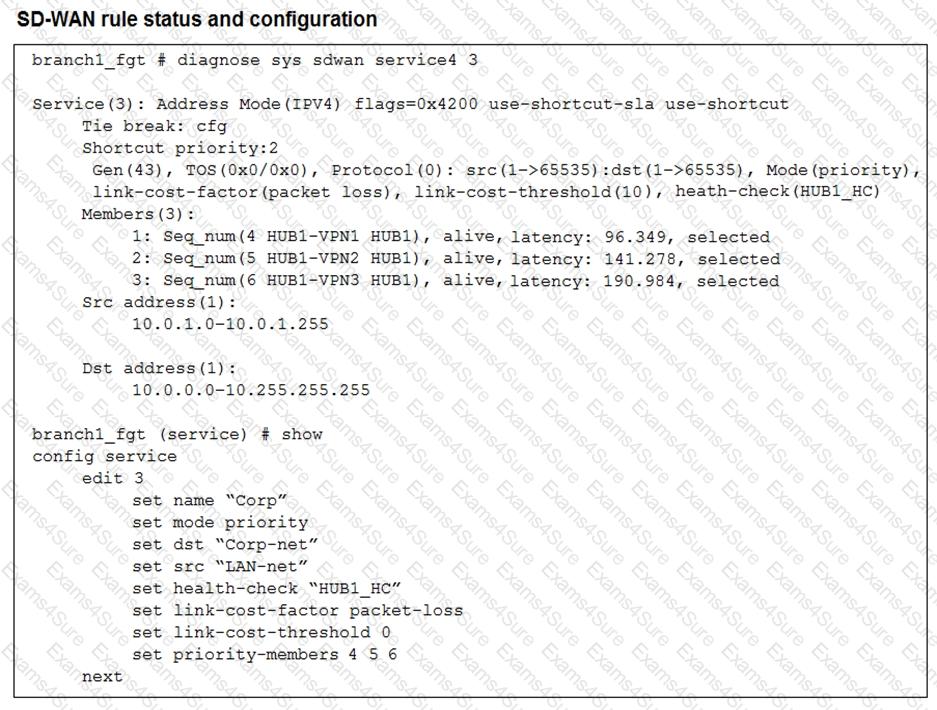
Refer to the exhibit, which shows the SD-WAN rule status and configuration.
Question # 1

Based on the exhibit, which change in the measured latency will first make HUB1-VPN3 the new preferred member?

Options:

A.  

When HUB1-VPN3 has a lower latency than HUB1-VPN1 and HUB1-VPN2

B.  

When HUB1-VPN3 has a latency of 80 ms

C.  

When HUB1-VPN3 has a latency of 90 ms

D.  

When HUB1-VPN1 has a latency of 200 ms

Discussion 0
Question # 2

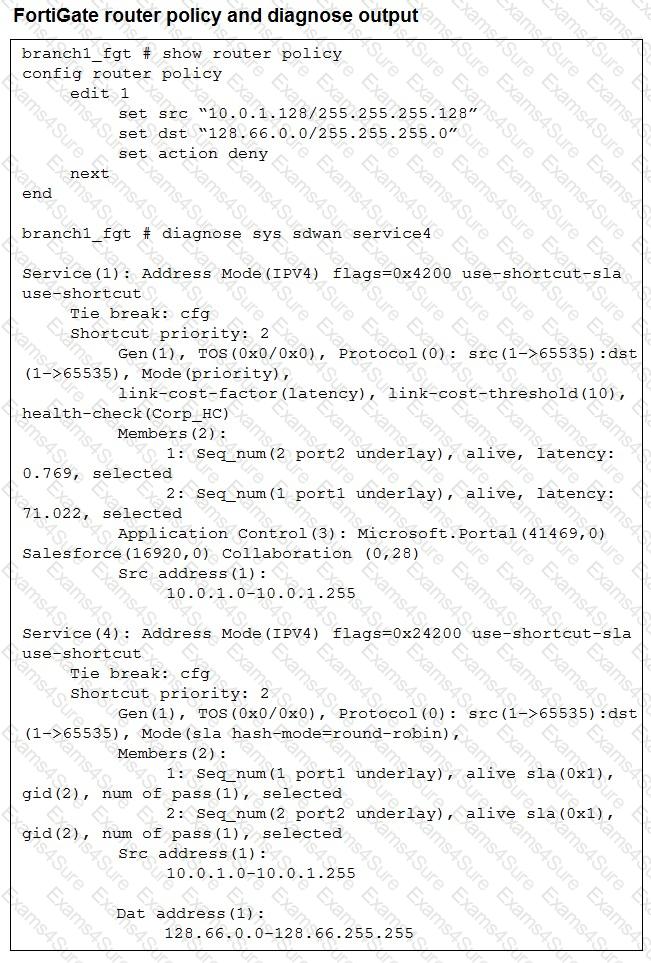
Refer to the exhibit.

Question # 2

How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0 125?

Options:

A.  

FortiGate drops the traffic flow.

B.  

FortiGate routes the traffic flow according to the forwarding information base (FIB).

C.  

FortiGate load balances the traffic flow through port7 and port8.

D.  

FortiGate steers the traffic flow through port7.

Discussion 0
Question # 3

(Which two features must you configure before FortiGate can steer traffic according to SD-WAN rules? Choose two answers.)

Options:

A.  

Security profiles

B.  

Underlay links

C.  

Overlay links

D.  

Traffic shaping

E.  

Firewall policies

Discussion 0
Question # 4

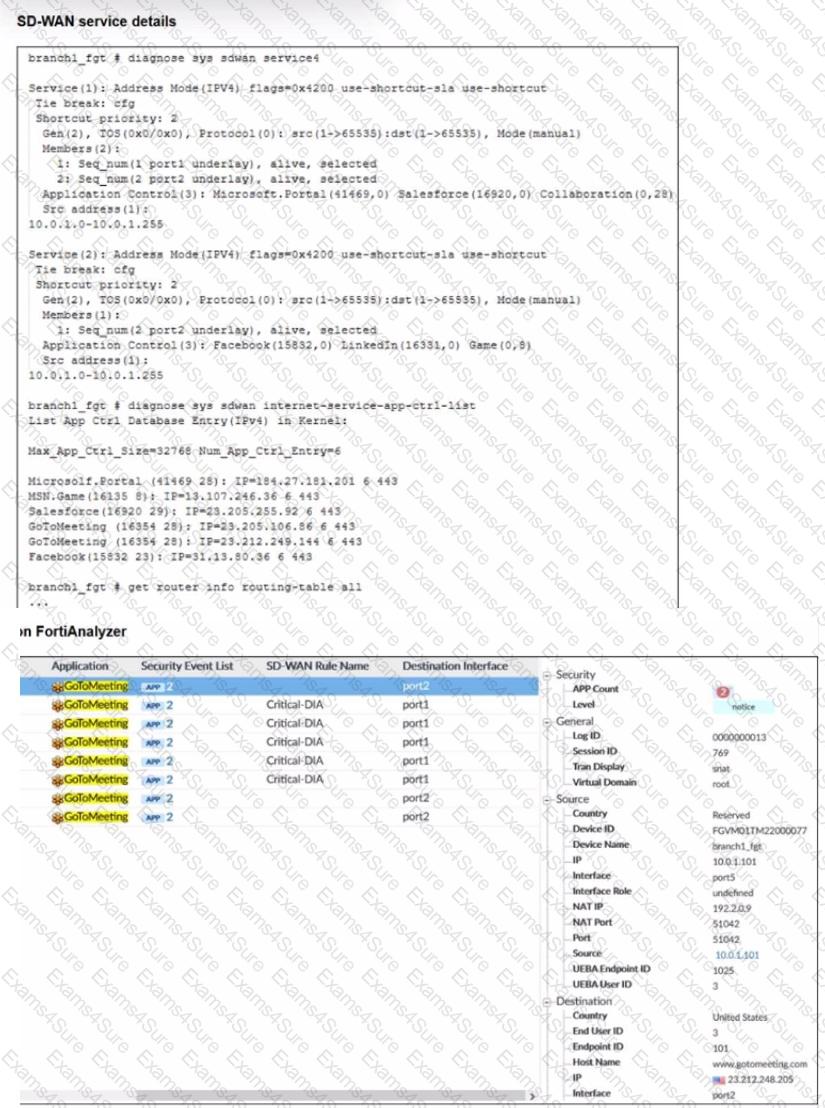
Refer to the exhibits.

Question # 4

An administrator is testing application steering in SD-WAN. Before generating test traffic, the administrator collected the information shown in the first exhibit. After generating GoToMeeting test traffic, the administrator examined the corresponding traffic log on FortiAnalyzer, which is shown in the second exhibit.

The administrator noticed that the traffic matched the implicit SD-WAN rule, but they expected the traffic to match rule ID 1.

Which two reasons explain why some log messages show that the traffic matched the implicit SD-WAN rule? (Choose two.)

Options:

A.  

Full SSL inspection is not enabled on the matching firewall policy.

B.  

The session 3-tuple did not match any of the existing entries in the ISDB application cache.

C.  

FortiGate could not refresh the routing information on the session after the application was detected.

D.  

No configured SD-WAN rule matches the traffic related to the collaboration application GoToMeeting

Discussion 0
Question # 5

Which two statements correctly describe what happens when traffic matches the implicit SD-WAN rule? (Choose two.)

Options:

A.  

The session information output displays no SD-WAN service id.

B.  

Traffic is load balanced using the algorithm set for the v4-ecmp-mode setting.

C.  

The traffic is distributed, regardless of weight, through all available static routes.

D.  

Traffic does not match any of the entries in the policy route table.

E.  

FortiGate flags the session with may_dirty and vwl_def ault.

Discussion 0
Question # 6

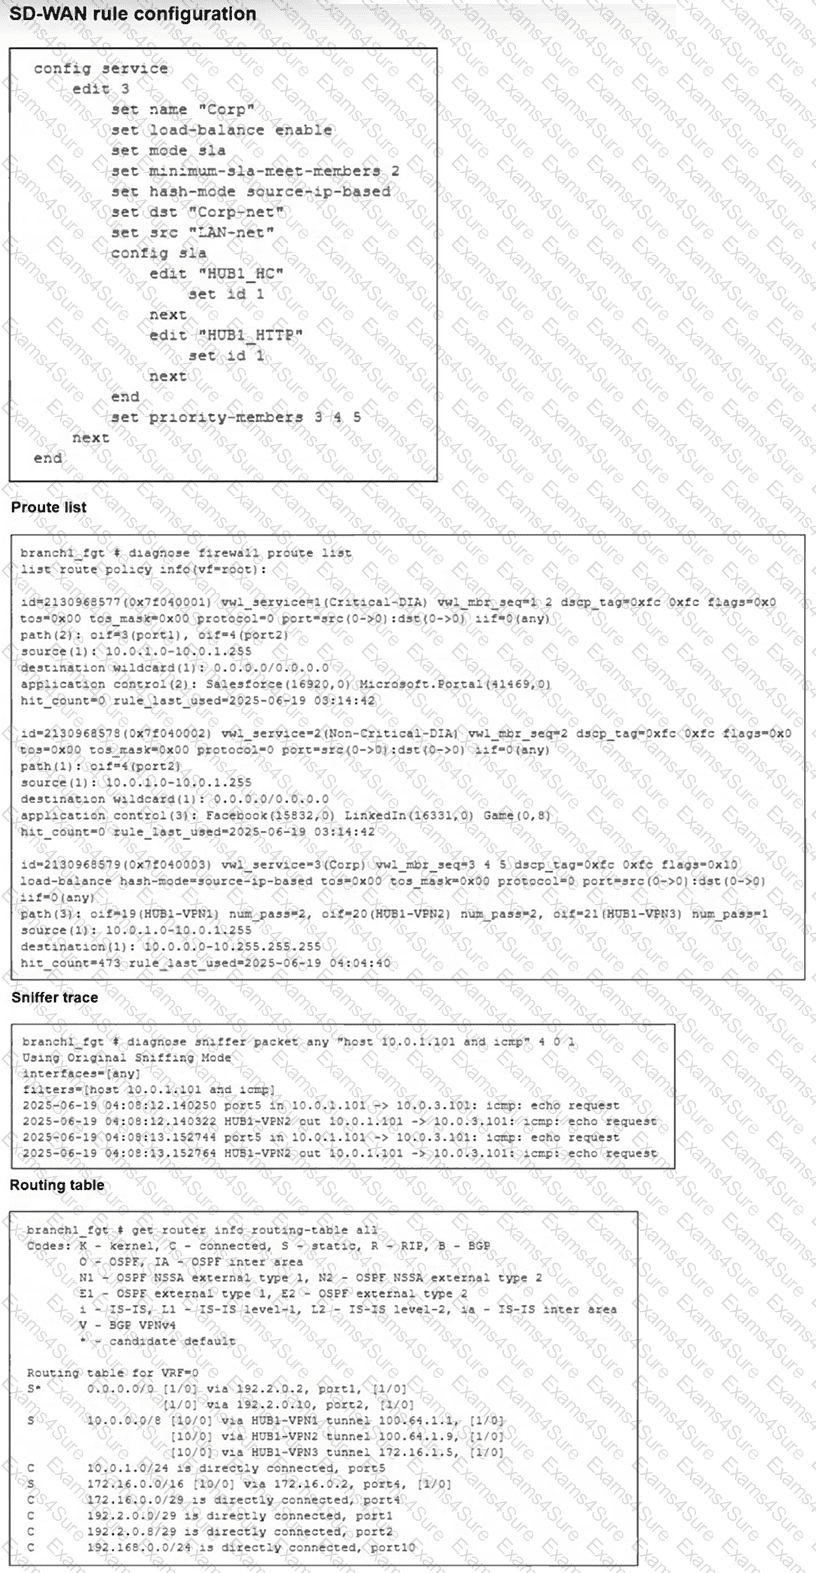
(Refer to the exhibits. You collected the output shown in the exhibits and want to know which interface TCP traffic will flow through from the user device 10.0.1.101 to the corporate file server 10.0.0.125. All SD-WAN links are stable.
Question # 6

Which interface will FortiGate use to steer the traffic? Choose one answer.)

Options:

A.  

Only HUB1-VPN1

B.  

Either HUB1-VPN1 or HUB1-VPN2

C.  

Only HUB1-VPN2

D.  

Either HUB1-VPN1, HUB1-VPN2, or HUB1-VPN3

Discussion 0
Question # 7

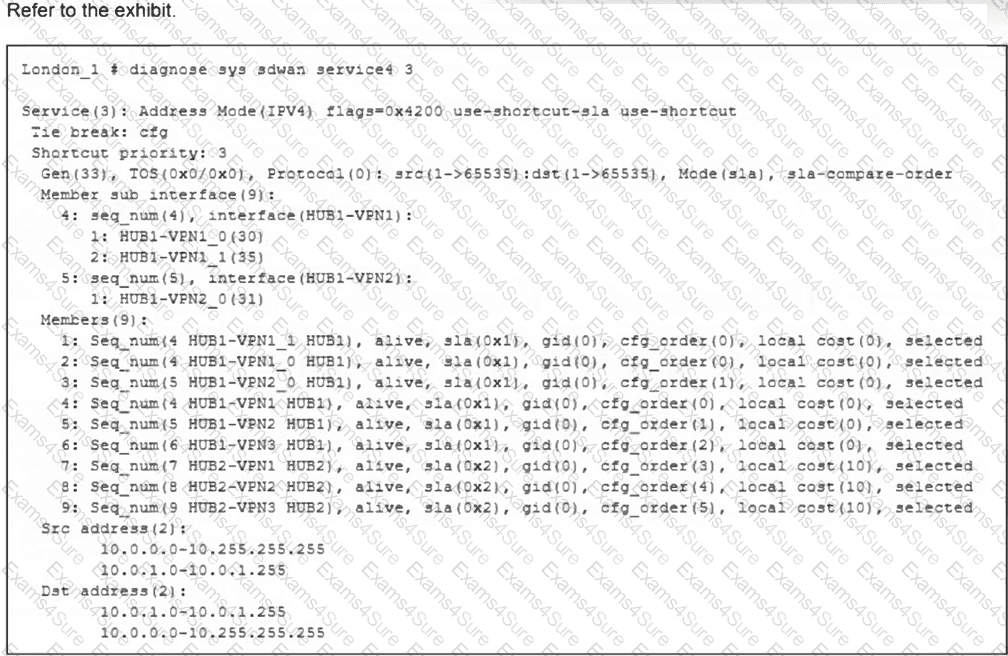
(Refer to the exhibit.

Question # 7

What can you conclude from the output shown? Choose one answer.)

Options:

A.  

It is a spoke device. SD-WAN rule 3 is configured with nine members.

B.  

It is a spoke device. The members of SD-WAN rule 3 are grouped into two zones.

C.  

It is a hub device. It allowed the establishment of three auto-discovery VPN (ADVPN) shortcuts.

D.  

It is a spoke device. SD-WAN rule 4 allows three shortcut tunnels.

Discussion 0
Question # 8

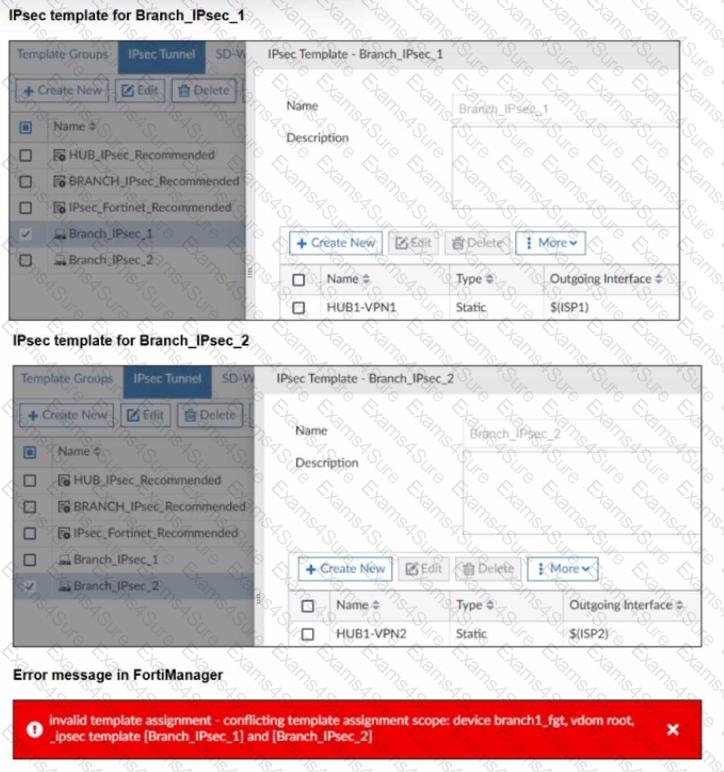
Refer to the exhibits.

Question # 8

The exhibits show two IPsec templates to define Branch IPsec 1 and Branch_IPsec_2. Each template defines a VPN tunnel. The error message that FortiManager displayed when the administrator tried to assign the second template to the FortiGate device is also shown.

Which statement best describes the cause of the issue?

Options:

A.  

You can assign only one template with a tunnel type of static to each FortiGate device.

B.  

You can assign only one IPsec template to each FortiGate device.

C.  

You should review the branch1_fgt configuration for configured tunnels in the rootVDOM.

D.  

You should use the same outgoing interface of both templates.

Discussion 0
Question # 9

An SD-WAN member is no longer used to steer SD-WAN traffic. The administrator updated the SD-WAN configuration and deleted the unused member. After the configuration update, users report that some destinations are unreachable. You confirm that the affected flow does not match an SD-WAN rule.

What could be a possible cause of the traffic interruption?

Options:

A.  

FortiGate, with SD-WAN enabled, cannot route traffic through interfaces that are not SD-WAN members.

B.  

FortiGate can remove some static routes associated with an interface when the member is removed from SD-WAN.

C.  

FortiGate removes the layer 3 settings for interfaces that are removed from the SD-WAN configuration.

D.  

FortiGate administratively brings down interfaces when they are removed from the SD-WAN configuration.

Discussion 0
Question # 10

Exhibit.

Question # 10

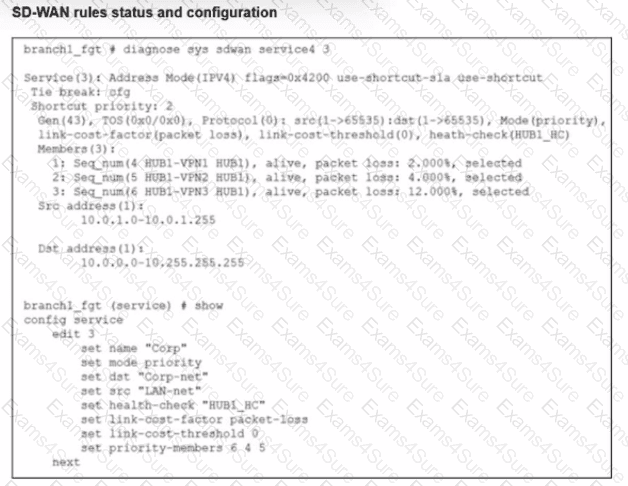
Refer to the exhibit, which shows the SD-WAN rule status and configuration.

Based on the exhibit, which change in the measured packet loss will make HUB1-VPN3 the new preferred member?


Options:

A.  

When HUB1-VPN1 has 4% packet loss

B.  

When HUB1-VPN1 has 12% packet loss

C.  

When HUB1-VPN3 has 4% packet loss

D.  

When all three members have the same packet loss

Discussion 0

Free Exams Sample Questions