
You have 500 on-premises Windows devices that are joined to a Microsoft Entra tenant named Tenant1 and enrolled in Microsoft Intune.
You have an Azure subscription named Sub1 that is linked to Tenant1.
You have a partner company that has an Azure subscription named Sub2. Sub2 contains a virtual network named VNet2 and a storage account named storage1. storage1 is secured by using an Azure Private Link endpoint on VNet2.
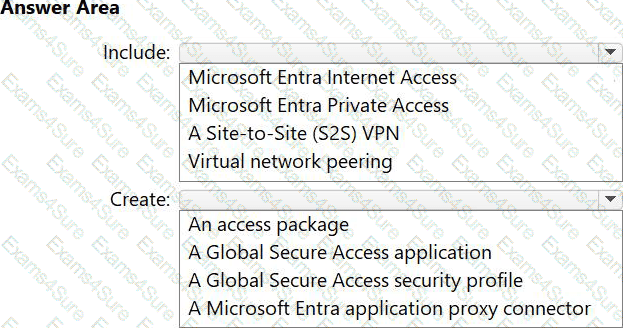
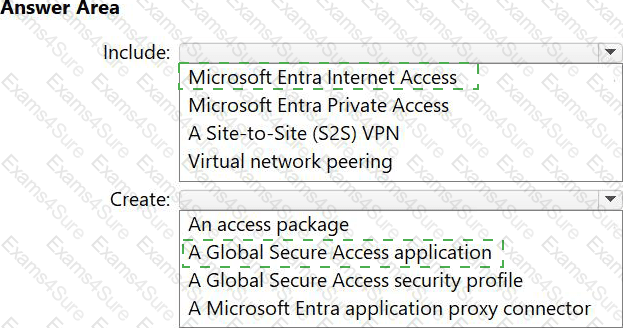
You need to recommend a solution to ensures that all the users at your company can access storage1 .
The solution must meet the following requirements:
• The users must sign in from a compliant device before accessing storage1.
• Access must NOT expose or provide connectivity to any other resources in Sub2.
What should you include in the recommendation, and what should you recommend creating in Tenant1? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains multiple apps. The apps are managed by using continuous integration and continuous deployment (CI/CD) pipelines in Azure DevOps.
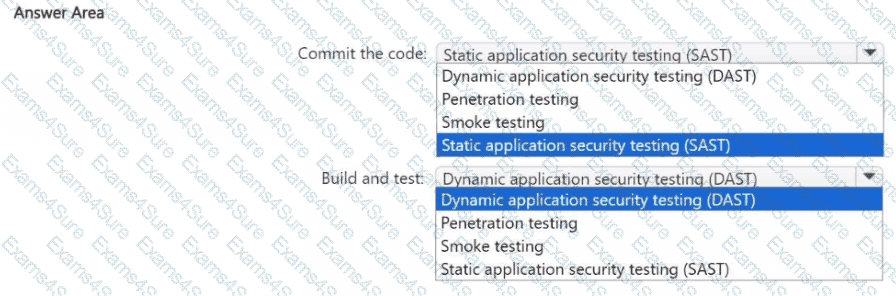
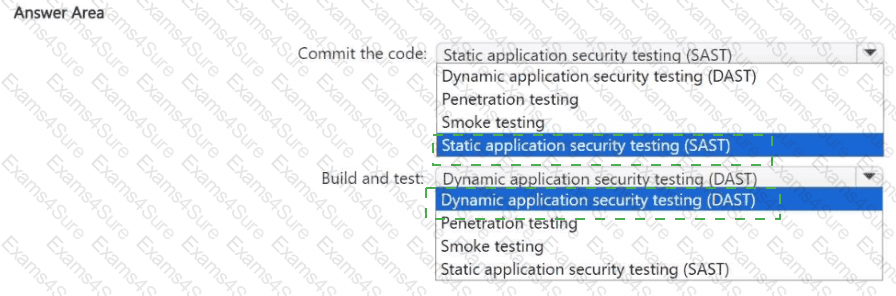
You need to recommend DevSecOps controls for the Commit the code and the Build and test CI/CD process stages based on the Microsoft Cloud Adoption Framework for Azure.
Which testing method should you recommend for each stage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company plans to provision blob storage by using an Azure Storage account The blob storage will be accessible from 20 application sewers on the internet. You need to recommend a solution to ensure that only the application servers can access the storage account. What should you recommend using to secure the blob storage?
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk
• Blocks user access to Saas apps that Microsoft has identified as high risk
Solution: From the Microsoft Defender portal, you set Web content filtering to On and create a web content filtering policy. Does this meet the goal?
Your company has an on-premises network, an Azure subscription, and a Microsoft 365 E5 subscription. The company uses the following devices:
• Computers that run either Windows 10 or Windows 11
• Tablets and phones that run either Android or iOS
You need to recommend a solution to classify and encrypt sensitive Microsoft Office 365 data regardless of where the data is stored. What should you include in the recommendation?




