

Exam style questions across every SC-500 domain
Last Update 4 days ago
Total Questions : 135
Start with our free SC-500 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Microsoft Certified: Information Security Administrator Associate exam. Each SC-500 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Microsoft weak domains, see where you're losing marks, and build a focused study plan in minutes.

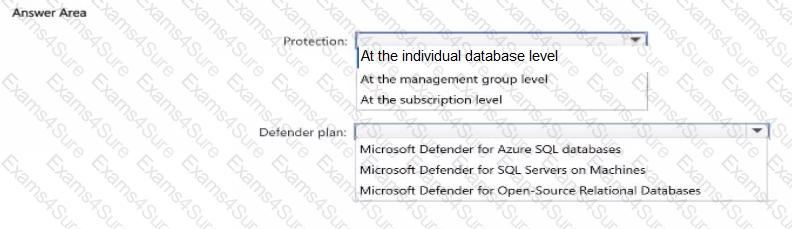
You have an Azure subscription that contains an Azure Database for PostgreSQL instance named 081.
You plan to protect OBI by using Microsoft Defender for Cloud.
You need to configure Defender for Cloud to detect anomalous activities and database exploitations for 061. The solution must NOT affect any other databases.
What should you enable? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
You have an Azure key vault named Vault1 that stores the resources shown in the following table.
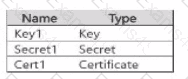
Which resources support the creation of a rotation policy?
You have an Azure subscription that contains the following servers:
•200 virtual machines that run either Windows Server or Ubuntu Server
•50 Azure Arc enabled servers
You use Azure Policy to manage compliance across all the servers.
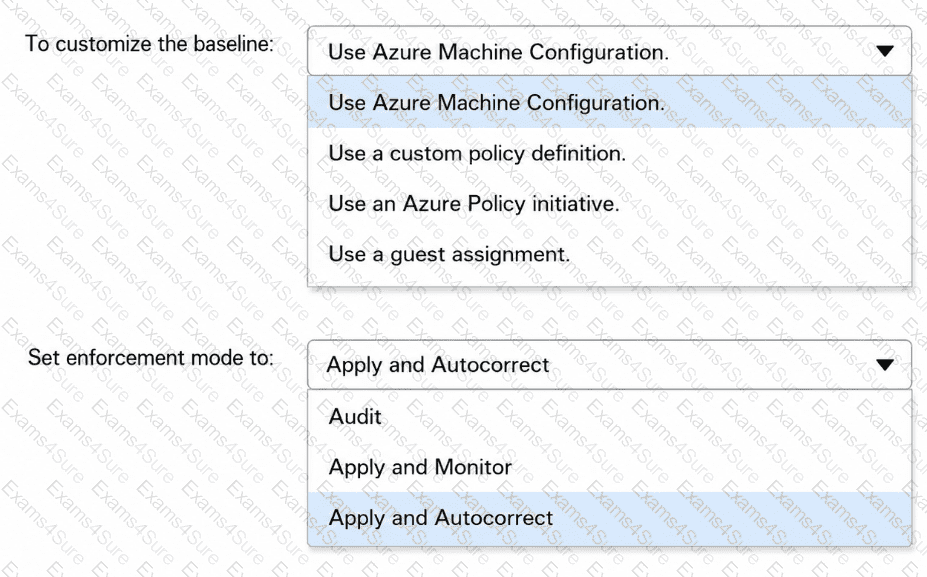
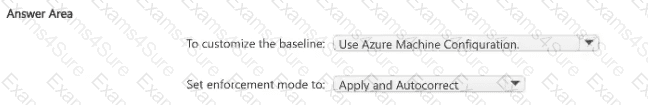
You need to enforce an organization-specific security baseline. The solution must meet the following requirements:
•Customize a built-in security baseline.
•Ensure that configuration changes to the servers are enforced automatically after the security baseline is deployed.
♦Minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

You plan to deploy Microsoft 365 Copilot
You discover that Copilot can access sensitive information in your Microsoft SharePoint Online libraries. You need to automatically identify which SharePoint Online content has be*»n shared between all internal users-What should you create?
You have an Azure Storage account named storage1 that contains Azure Files shares.
You have an application named App1 that uses a system-assigned managed identity to access the shares.
Administrators access the shares by using storage account keys.
You need to ensure that App1 access the shares without using the storage account keys.
What should you do on storage1?
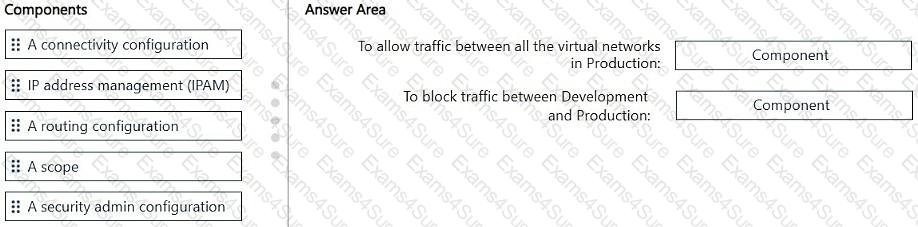
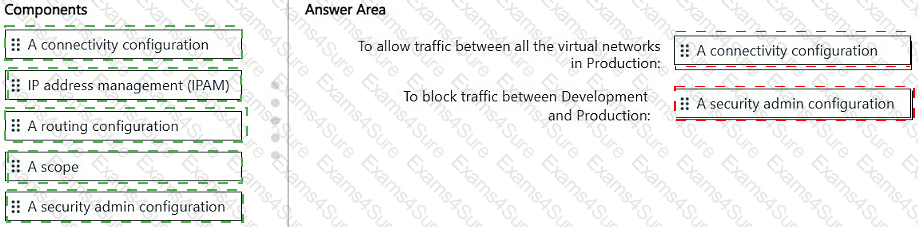
You use Azure Virtual Network Manager to manage multiple virtual networks organized into two network groups named Production and Development.
You need to configure Virtual Network Manager to meet the following requirements:
Allow traffic between all the virtual networks in Production.
Block traffic between Development and Production.
What should you use for each requirement? To answer, drag the components to the correct requirements. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure subscription named Sub1 that contains multiple virtual machines.
You have a Microsoft 365 E5 subscription that contains devices onboarded to Microsoft Defender for Endpoint.
You have an on-premises datacenter that contains multiple servers.
You plan to onboard all existing and future on-premises servers to Azure Arc.
You need to ensure that the Azure Arc-enabled servers are protected by using the same security features as the Microsoft 365 devices immediately after the servers are onboarded. The solution must minimize administrative effort.
What should you do?
You have a Microsoft 365 tenant that uses Microsoft Security Copilot and Microsoft Defender XDR.
Access to Microsoft Defender XDR is managed by using Microsoft entra global roles.
The Phishing triage Agent is available in Microsoft Defender. The required agent prerequisites and approvals are complete
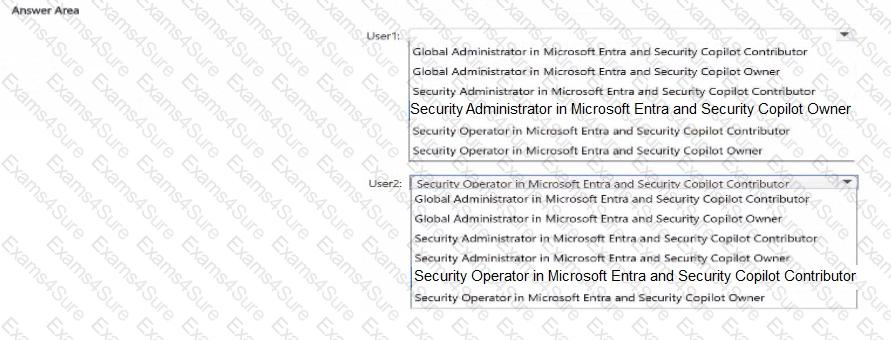
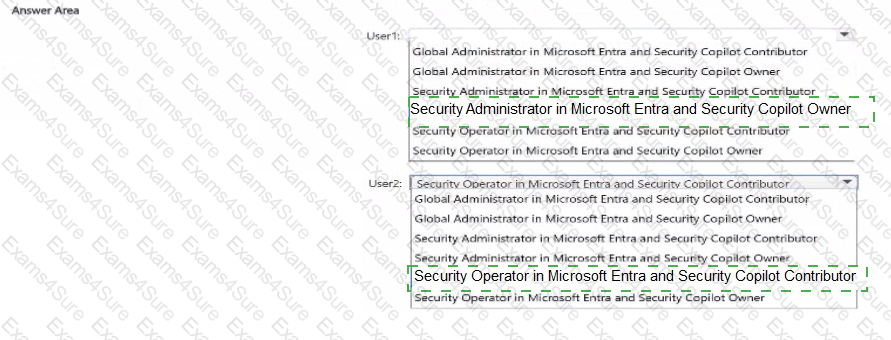
Two users will perform the following tasks:
• User1 will enable and manage the Phishing Triage Agent settings.
• User2 will use Security Copilot in Microsoft Defender XDR to manage phishing incidents identified by the agent.
You need to assign the least-privileged built in Microsoft Entra role and Security Copilot role combination to each us Which roles should you assign to each user? To answer, select the appropriate options in the answer area.
You have an Azure subscription named Sub1 that contains multiple virtual machines. Sub1 has the Microsoft Defender Cloud Security Posture Management (CSPM) plan enabled.
You discover that Defender for Cloud falls to identify plaintext connection strings and SSH keys stored on the virtual machines.
You need to ensure that secrets can be identified on the virtual machines.
What should you do?



