Exclusive Black Friday Deal: 70% Off All Exam Bundles! Use coupon code below to unlock your savings! - Ends in 0d 00h 00m 00s - Coupon code: Friday70

Free Certified Threat Protection Analyst Exam Practice Questions

Question # 11

What is a defining characteristic of Advanced Persistent Threat (APT) actors?

Options:

A.  

They primarily use social engineering to gain access.

B.  

They operate independently without government affiliation.

C.  

They focus on short-term financial scams.

D.  

They are state-sponsored and target strategic assets.

Discussion 0
Question # 12

Why do some domains generate a warning when they are added to the custom blocklist in TAP?

Options:

A.  

Because they are already blocked and restricted by default in the network system.

B.  

Because they are already blocked by other security measures, such as IPS and firewall.

C.  

Because they are less popular and low-risk domains that do not pose a threat.

D.  

Because entire domains of popular and prominent services on the web should not be blocked.

Discussion 0
Question # 13

For which two reasons should organizations customize their incident response plans based on NIST SP 800-61 or another incident response standard? (Select two.)

Options:

A.  

To make it more generic so that it can be used to respond to incidents from new attack vectors.

B.  

To document the contact information for each of the security analysts at your managed security services provider.

C.  

To change the order of operations in the Incident Response Lifecycle processes to match ISO 12035.

D.  

To meet unique requirements relating to the organization’s mission, size, structure, and functions.

E.  

To improve incident response effectiveness and efficiency by creating a repeatable process and documented handoffs.

Discussion 0
Question # 14

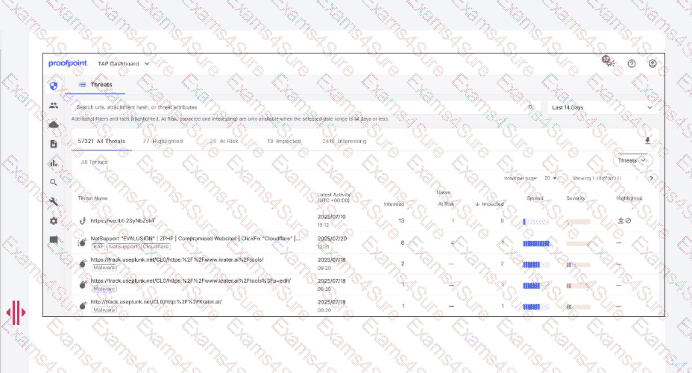
Exhibit:

Question # 14

Which column indicates the number of users targeted by a malicious campaign or threat?

Options:

A.  

Highlighted

B.  

Intended

C.  

At Risk

D.  

Impacted

Discussion 0
Question # 15

Which two factors make Business Email Compromise (BEC) attacks difficult to detect? (Select two.)
Options:

A.  

They use malicious URLs.

B.  

They use spam.

C.  

They use social engineering.

D.  

They use impersonation.

E.  

They use malware.

Discussion 0

PPAN01 PDF

PPAN01 PDF (Printable)
$46.5
$154.99

PPAN01 Testing Engine

PPAN01 PDF (Printable)
$51
$169.99

PPAN01 PDF + Testing Engine

PPAN01 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions