

Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Certified Threat Protection Analyst Exam Practice Questions

Exams4sure Dumps

Exam style questions across every PPAN01 domain

Last Update 3 days ago
Total Questions : 52

Start with our free PPAN01 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Threat Protection Analyst exam. Each PPAN01 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Proofpoint weak domains, see where you're losing marks, and build a focused study plan in minutes.

PPAN01 PDF

PPAN01 PDF (Printable)
$46.5
$154.99

PPAN01 Testing Engine

PPAN01 PDF (Printable)
$51
$169.99

PPAN01 PDF + Testing Engine

PPAN01 PDF (Printable)
$63.9
$212.99
Question # 1

Refer to Exhibit:

X-Proofpoint-Banner-Trigger: inbound

MIM-version: 1.0

Content-Type: multipart/mixed; boundary="boundary-1698346305"

X-CLX-Shades: MLX

X-Proofpoint-Virus-Version: vendor=baseguard

engine=ICAP:2.0.272,Aquarius:18.0.987,Hydra:6.0.619,FMLib:17.11.176.26 definitions=2023-10-26_22,2023-10-26_01,2023-05-22_02

X-Proofpoint-Spam-Details: rule=spam policy=default score=89 bulkscore=0 phishscore=0 mlxlogscore=-91 suspectscore=0 malwarescore=0 adultscore=0 spamscore=89 classifier=spam adjust=0 reason=mlx scancount=l engine=8.12.0-2310240000 definitions=main-2310260209

In the process of reviewing a false positive, you see the following email header. What was the reason the message was quarantined by the Proofpoint Protection Server?

Options:

A.  

A custom spam rule caused the message to be quarantined.

B.  

An anti-virus rule forced the message to be quarantined.

C.  

The recipient's personal block list forced quarantine of the message.

D.  

A content policy rule (DLP/compliance) forced quarantine of the message.

Discussion 0
Question # 2

Which TAP condemnation results from an analysis of emails submitted via Proofpoint ZenGuide Report Suspicious (formerly PhishAlarm)?

Options:

A.  

Anomalous Traffic Detection

B.  

Proofpoint Threat Analyst

C.  

End User via CLEAR

D.  

Customer Administrator via Blocklist

Discussion 0
Question # 3

What are two unique benefits of submitting false positives via the support portal? (Select two.)

Options:

A.  

Automatic correction to label the threat as a false positive

B.  

Generating a complaint to the TAP product manager

C.  

Human review of the false positive claim

D.  

Feedback on the false positive submission

E.  

Quick reputation check on the message contents

Discussion 0
Question # 4

Which Proofpoint product quarantines malicious email after delivery?

Options:

A.  

CASB

B.  

TAP

C.  

CLEAR

D.  

TRAP

Discussion 0
Question # 5

Which of the following is an item that should be included in an incident report as part of the post-incident debrief?

Options:

A.  

Network diagrams

B.  

Incident response plan

C.  

Adversary tactics and techniques

D.  

Proofpoint threat landscape reporting

Discussion 0
Question # 6

What is the first action a security analyst should take when beginning to review and prioritize alerts from Targeted Attack Protection (TAP)?

Options:

A.  

Use filtering options on the TAP Threats page to organize and prioritize threat alerts.

B.  

Assess claims of false positives by analyzing forensic details and threat indicators.

C.  

Open and examine the contents of an email using the associated .eml file.

D.  

Investigate false negatives by identifying root causes in source policy configurations.

Discussion 0
Question # 7

Which two threat protection capabilities are available as part of Proofpoint’s Targeted Attack Protection (TAP)? (Select two.)
Options:

A.  

Cloud-based solution that remediates threats post-delivery

B.  

Training solution that drives user behavioral change

C.  

Provides protection against URL-based email threats

D.  

Pulls malicious emails from user inbox after delivery

E.  

Protects users against threats in email attachments

Discussion 0
Question # 8

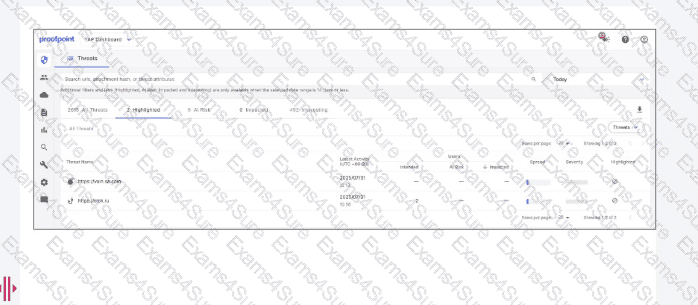
Exhibit:

Question # 8

What is indicated by the icon shown in the “Highlighted” column?

Options:

A.  

The threat has been added to a custom blocklist.

B.  

The threat has been reported as a false negative.

C.  

The threat has been reported as a false positive.

D.  

The threat has been cleared and considered safe.

Discussion 0
Question # 9

An analyst has been tasked with providing a report that can be used to prioritise investigations based on a user's Attack Index score. Which report would be most suitable for this purpose?


Options:

A.  

VIP Activity

B.  

Top 10 Recipients

C.  

Very Attacked People

D.  

Top 10 Clickers

Discussion 0
Question # 10

Which scenario would prevent URL Defense from rewriting a URL?

Options:

A.  

The URL is contained in a PDF attachment.

B.  

The user has clicked the URL before.

C.  

The URL is hosted on a secure HTTPS domain.

D.  

The email was not flagged as malicious.

Discussion 0

Free Exams Sample Questions
