Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Splunk Certified Cybersecurity Defense Engineer Practice Questions

Question # 11

What framework in Enterprise Security allows engineers to build detections using known malicious IOCs, comparing them to event logs to find suspicious behavior?

Options:

A.  

Asset & Intelligence Framework

B.  

Incident Management Framework

C.  

Threat Intelligence Framework

D.  

OSINT Framework

Discussion 0
Question # 12

A cyber defense engineer plays a role in maintaining a secure SOAR Cloud configuration. Which network security statement is correct about SOAR Cloud?

Options:

A.  

Splunk Cloud initiates an outbound SSL connection to both the Automation Broker and managed endpoints.

B.  

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

C.  

The Automation Broker initiates an inbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

D.  

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and the managed endpoint initiates an outbound connection to the Automation Broker.

Discussion 0
Question # 13

Which Splunk Enterprise Security add-on facilitates the ingestion of Threat Intelligence data?

Options:

A.  

TA-ThreatIntel

B.  

ESS-Intel

C.  

SA-ThreatIntelligence

D.  

SA-ESSIntel

Discussion 0
Question # 14

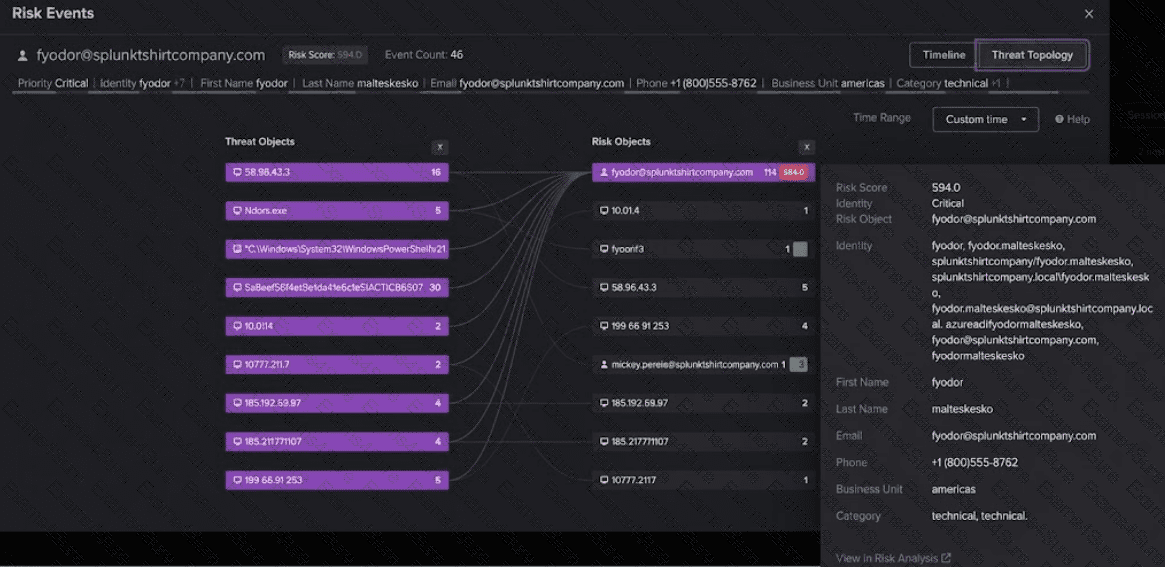
Based on the provided screenshot, it ' s discovered that different machines or accounts have been associated with the shown threat objects.
Question # 14

Enterprise Security has identified that these machines and accounts all point back to one owner - Fyodor. Which two frameworks in ES are responsible for programmatically associating this information together?

Options:

A.  

Threat Intelligence, Assets & Identities

B.  

Risk, Incident Review

C.  

Risk, Assets & Identities

D.  

Threat Intelligence, Risk

Discussion 0
Question # 15

An engineer receives a report that the “Traffic over time by action” dashboard is not populating. It has been confirmed that the relevant logs are being ingested properly and they are CIM compliant. What other configuration may be missing?

Options:

A.  

The Network Sessions data model should be accelerated.

B.  

The Performance data model is missing the network dataset.

C.  

The Network Traffic data model should be accelerated.

D.  

The Network Sessions data model has been deleted.

Discussion 0
Question # 16

For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?

Options:

A.  

The data model ' s constraint macro.

B.  

The data model ' s index list.

C.  

The data model ' s root expression.

D.  

The data model ' s dataset hierarchy.

Discussion 0
Question # 17

Which practices strengthen the development of Standard Operating Procedures (SOPs)? (Choose three)

Options:

A.  

Regular updates based on feedback

B.  

Focusing solely on high-risk scenarios

C.  

Collaborating with cross-functional teams

D.  

Including detailed step-by-step instructions

E.  

Excluding historical incident data

Discussion 0
Question # 18

Which field in the risk index is used to describe the activity within a finding?

Options:

A.  

risk_message

B.  

risk_description

C.  

risk_object

D.  

risk_reason

Discussion 0
Question # 19

If a correlation search cannot be run at the configured time, which scheduling option should an engineer use to ensure there are no backfill gaps in data?

Options:

A.  

Default

B.  

Continuous

C.  

Real-time

D.  

Auto

Discussion 0
Question # 20

MITRE D3FEND is designed to compliment MITRE ' s list of adversarial tactics, techniques, and common knowledge (ATT & CK). Which tactics are associated with MITRE D3FEND in order to detect, deny, and disrupt adversarial efforts?
Options:

A.  

Harden, Detect, Exclude, Deceive, Eradicate

B.  

Harden, Detect, Isolate, Disrupt, Evict

C.  

Harden, Detect, Exclude, Define, Eradicate

D.  

Harden, Detect, Isolate, Deceive, Evict

Discussion 0

SPLK-5002 PDF

SPLK-5002 PDF (Printable)
$46.5
$154.99

SPLK-5002 Testing Engine

SPLK-5002 PDF (Printable)
$51
$169.99

SPLK-5002 PDF + Testing Engine

SPLK-5002 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions