Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free CrowdStrike Certified SIEM Engineer Practice Questions

Exams4sure Dumps

Exam style questions across every CCSE-204 domain

Last Update 1 day ago
Total Questions : 62

Start with our free CCSE-204 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CrowdStrike CCSE exam. Each CCSE-204 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your CrowdStrike weak domains, see where you're losing marks, and build a focused study plan in minutes.

CCSE-204 PDF

CCSE-204 PDF (Printable)
$54.25
$154.99

CCSE-204 Testing Engine

CCSE-204 PDF (Printable)
$59.5
$169.99

CCSE-204 PDF + Testing Engine

CCSE-204 PDF (Printable)
$74.55
$212.99
Question # 1

You notice that the format of incoming logs suddenly changes from JSON format to key-value pairs during log collection.

What action would you take to parse the data correctly?

Options:

A.  

Use a multi-source configuration with different parsers per source

B.  

Switch to fleet mode and monitor the logs

C.  

Restart the log collector in debug mode

D.  

Disable parsing entirely

Discussion 0
Question # 2

You are reviewing a lookup file to determine whether an event was successfully parsed during ingestion.

Which metadata field indicates the event’s parsing status?

Options:

A.  

@ingesttimestamp

B.  

@rawstring

C.  

@error_msg

D.  

@event_parsed

Discussion 0
Question # 3

You are creating a dashboard in Next-Gen SIEM and want to change the visualization used by a widget.

What must be selected to make this change?

Options:

A.  

Interactions options

B.  

Edit in Search view

C.  

Styling options

Discussion 0
Question # 4

The parseJson() function would be used to parse which log message format from the list below?

Options:

A.  

level=debug msg="Disconnected" host=app01

B.  

192.168.1.1 [192.168.1.1] - - [10/May/2024:14:23:11 +0000] "GET/index.html"

C.  

{ "level": "info", "msg": "User login", "user": "john_doe" }

D.  

2024-05-10T14:23:11Z INFO Service started

Discussion 0
Question # 5

What is the recommended order of the three required activities to build an efficient CQL query?

Options:

A.  

Filter > Format > Aggregate

B.  

Filter > Aggregate > Format

C.  

Format > Filter > Aggregate

D.  

Aggregate > Filter > Format

Discussion 0
Question # 6

A correlation rule is generating a high volume of detections. You have been asked to temporarily deactivate it so your team can investigate.

What will happen to previously generated detections while the rule is in a deactivated state?

Options:

A.  

They will not be impacted and will remain within the console

B.  

Their status will change to closed and tagged as true positives in the console

C.  

Their status will change to closed and tagged as false positives in the console

D.  

They will be immediately deleted from the console

Discussion 0
Question # 7

When deploying the Falcon Log Collector using the commands in the CrowdStrike Fleet Management interface, what is the correct service name?

Options:

A.  

flc-api

B.  

humio-collector

C.  

logscale-collector

D.  

flc-collector

Discussion 0
Question # 8

Review the log event below:

{"ts": "2018/11/01 14:31:10", "server": "web01", "message": "Out of memory"}

Which parsing function is correct to add a missing timezone field?

Options:

A.  

parseJson() | parseTimestamp("dd/MMM/yyyy:HH:mm:ss Z", timezone="Europe/Paris", field=ts)

B.  

kvParse() | findTimestamp(field=ts, timezone="Europe/London")

C.  

kvParse() | findTimestamp(timezone="America/New_York")

D.  

parseJson() | parseTimestamp("yyyy/MM/dd HH:mm:ss", timezone="Europe/Paris", field=ts)

Discussion 0
Question # 9

What is the primary benefit of utilizing Next-Gen SIEM’s built-in dashboards?

Options:

A.  

Direct access to raw log data

B.  

Custom queries for specific events

C.  

Quick insights without manual setup

D.  

Capability to modify dashboard source code

Discussion 0
Question # 10

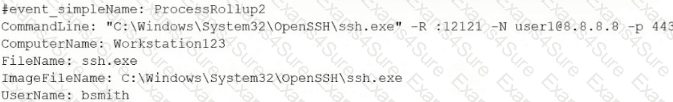
An event has the following fields:

Question # 10

Which CQL query will output the frequency of a unique set of ComputerName, UserName, CommandLine?


Options:

A.  

#event_simpleName = ProcessRollup2 FileName = ssh.exe CommandLine = /\s-R\s.+\s-p/ | table([ComputerName, UserName, CommandLine]) | count()

B.  

#event_simpleName = ProcessRollup2

| FileName = ssh.exe

| CommandLine = /\s-R\s.+\s-p/

| table([ComputerName, UserName, CommandLine], function=count())

C.  

#event_simpleName = ProcessRollup2

| FileName = ssh.exe

| CommandLine = /\s-R\s.+\s-p/

| groupBy([ComputerName, UserName, CommandLine], function=count())

D.  

#event_simpleName = ProcessRollup2 FileName = ssh.exe CommandLine = /\s-R\s.+\s-p/ | groupBy([ComputerName, UserName, CommandLine])

Discussion 0

Free Exams Sample Questions