Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Developing in Agentic AI Systems Practice Questions

Exams4sure Dumps

Exam style questions across every GH-600 domain

Last Update 3 hours ago
Total Questions : 106

Start with our free GH-600 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real GitHub Administrator exam. Each GH-600 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Microsoft weak domains, see where you're losing marks, and build a focused study plan in minutes.

GH-600 PDF

GH-600 PDF (Printable)
$46.5
$154.99

GH-600 Testing Engine

GH-600 PDF (Printable)
$51
$169.99

GH-600 PDF + Testing Engine

GH-600 PDF (Printable)
$63.9
$212.99
Question # 11

You have a GitHub Enterprise Cloud repository that uses the GitHub Copilot coding agent to implement changes by creating draft pull requests in a firewalled GitHub Actions environment.

Repository administrators add a Model Context Protocol (MCP) server configuration so that the agent can query an external system while it executes issues. The MCP server requires an API key, and the key must be provided to the MCP server as an environment variable when the server starts.

You create an environment secret named copilot_mcp_api_key that contains the API key.

You need to configure the repository to ensure that the MCP server receives the API key at runtime. The solution must ensure that only the intended secret is available to the MCP configuration.

What is the best option to use to achieve the goal?

Options:

A.  

A default environment variable

B.  

An environment variable

C.  

An Actions repository secret

D.  

An environment variable mapping

E.  

The JSON configuration

Discussion 0
Question # 12

You need to configure agent1 to support the planned changes.

What should you do?

Options:

A.  

Add Use all available tools to the instructions in the agent configuration.

B.  

Add the mcp-servers property to the agent configuration.

C.  

In the agent configuration, replace line 05 with the following: tools: []

D.  

Add Use all available tools to the .github/copilot-instructions.md file.

E.  

Delete line 05 from the agent configuration.

Discussion 0
Question # 13

You need to resolve the scoping issue associated to agent1.

What should you do?

Options:

A.  

To the profile of agent1, add a custom instruction specifying that the agent must NOT access billing-service or infra-terraform.

B.  

Add a permissions block to the agent1 workflow in product-api.

C.  

Create a fine-grained personal access token (PAT) scoped to product-api and store the PAT as a GitHub Actions secret for agent1 to use.

D.  

Create a ruleset for billing-service and infra-terraform that blocks push access from the github-actions bot account.

Discussion 0
Question # 14

You need to resolve the issue of the agents generating conflicting output. The solution must meet the implementation guidelines.

What should you do?

Options:

A.  

Configure each agent to work on a separate branch and add a required status check that detects file-level overlap before either pull request can be merged.

B.  

Configure tools: [ ' read ' , ' search ' ] in both agent profiles to prevent either agent from writing files.

C.  

Add shared/config.yaml to a CODEOWNERS file that requires SG_Review approval before any changes can be merged.

D.  

Configure a concurrency group on both agent workflows so that only one workflow runs at a time.

Discussion 0
Question # 15

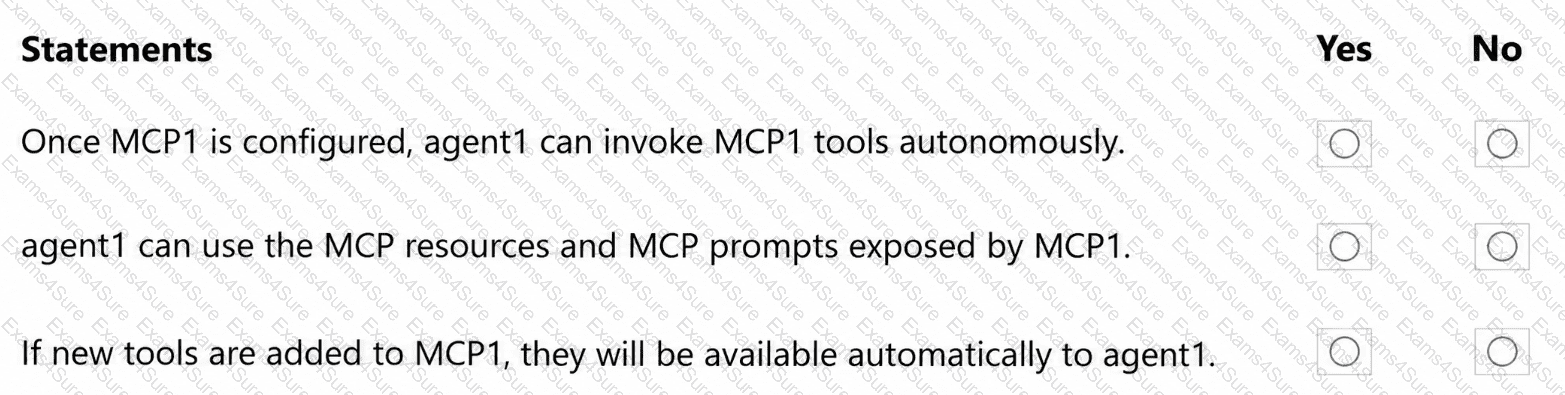
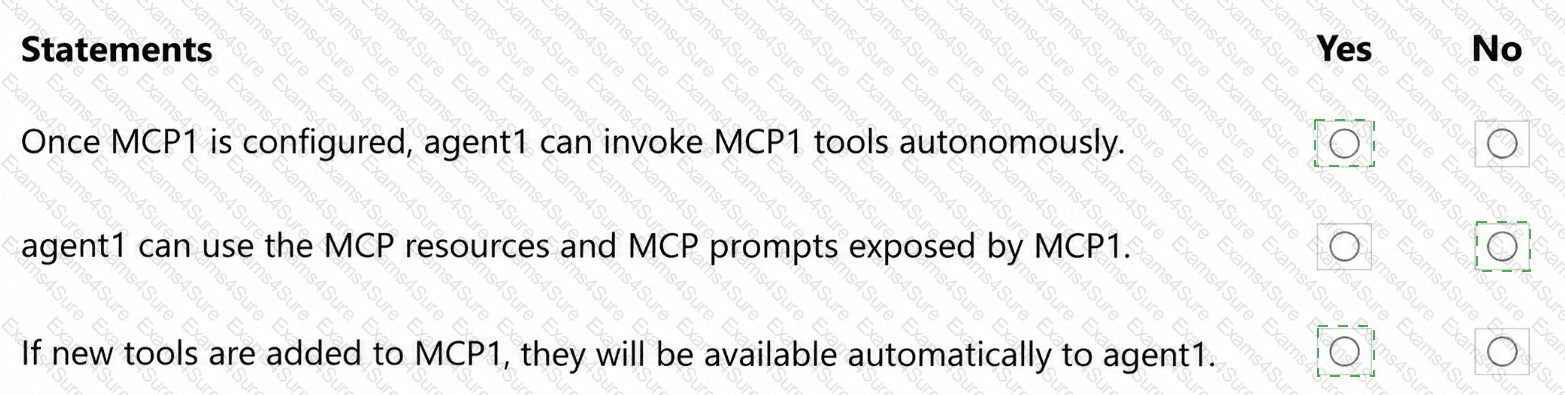
You are evaluating how agent1 will behave after you implement the planned changes.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

NOTE: Each correct selection is worth one point.
Question # 15

Options:

Discussion 0
Question # 16

You need to provide access to the API key of MCP1. The solution must meet the security requirements.

What should you do?

Options:

A.  

Store the API key as a secret in the Copilot environment of product-api by using a name prefix of COPILOT_MCP_, and then reference the variable name in the mcp.json configuration.

B.  

In the product-api repository settings, add the API key directly to the .mcp/server.json file by using a plaintext apiKey field.

C.  

Store the API key as a GitHub Codespaces user secret scoped to product-api.

D.  

In product-api, add the API key as a GitHub Actions encrypted secret and reference the secret by using ${{ secrets.KEY }} in the workflow YAML of agent1.

Discussion 0
Question # 17

You need to enable Copilot memory to support the planned changes.

What should you configure?

Options:

A.  

The personal Copilot settings of each developer

B.  

The Copilot settings of each repository

C.  

The agent profile of agent1

D.  

The Copilot settings of the organization

Discussion 0
Question # 18

You need to make changes to repo1 to support the planned changes for the agents.

What should you modify?

Options:

A.  

< project > /.mcp/server.json

B.  

.vscode/settings.json

C.  

.github/agents/*.agent.md

D.  

.vscode/mcp.json

Discussion 0
Question # 19

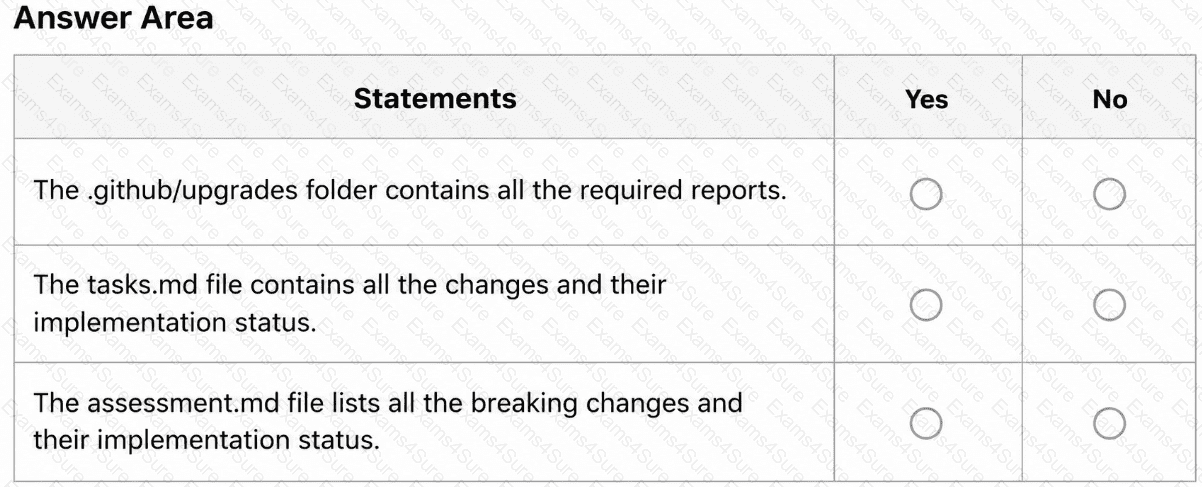
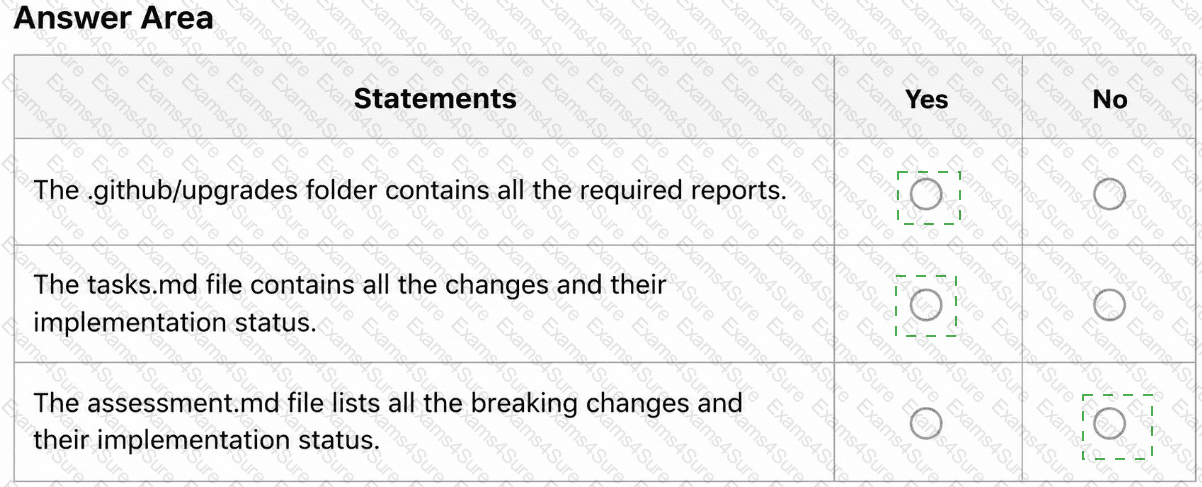
After App1 is upgraded to meet the technical requirements, you need to validate the output.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

NOTE: Each correct selection is worth one point.
Question # 19

Options:

Discussion 0
Question # 20

You need to troubleshoot the issue reported by Dev1.

What should you review?

Options:

A.  

The GitHub Actions usage metrics of repo1.

B.  

The agent session log in the Agents panel.

C.  

The GitHub Actions runner log for the session job.

D.  

The GITHUB_TOKEN permissions block in the agent1 workflow.

Discussion 0

Free Exams Sample Questions