
Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Huawei Certified ICT Professional - Constructing Service Security Network (HCIP-Security-CSSN V3.0) Practice Questions

Question # 11

In the penetration stage of an APT attack, which of the following attack behaviors will the attacker generally have?

Options:

A.  

Long-term latency and collection of key data.

B.  

Leak the acquired key data information to a third party of interest

155955cc-666171a2-20fac832-0c042c044

C.  

Through phishing emails, attachments with 0day vulnerabilities are carried, causing the user's terminal to become a springboard for attacks.

D.  

The attacker sends a C&C attack or other remote commands to the infected host to spread the attack horizontally on the intranet.

Discussion 0
Question # 12

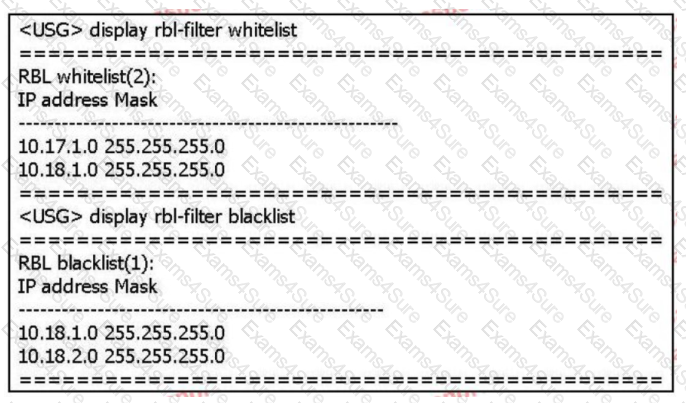
The results of the RBL black and white list query on the firewall are as follows:
Question # 12

Based on the above information only, which of the following statements is correct? (multiple choice)

Options:

A.  

Mail with source address 10.17.1.0/24 will be blocked

B.  

Mail with source address 10.18.1.0/24 will be blocked

C.  

Mail with source address 10.17.1.0/24 will be released

D.  

Mail with source address 10.18.1.0/24 will be released

Discussion 0
Question # 13

The processing flow of IPS has the following steps;

1. Reorganize application data

2. Match the signature

3. Message processing

4. Protocol identification

Which of the following is the correct order of the processing flow?

Options:

A.  

4-1-2-3

B.  

1-4-2-3

C.  

1-3-2-4

D.  

2-4-1-3:

Discussion 0
Question # 14

Which of the following attacks are attacks against web servers? (multiple choices)

Options:

A.  

Website phishing deception

B.  

Website Trojan

C.  

SQL injection

D.  

Cross-site scripting attacks 2335

Discussion 0
Question # 15

Huawei's USG000 product can identify the true type of common files and over-check the content. Even if the file is hidden in a compressed file, or change the extension

The name of the exhibition can't escape the fiery eyes of the firewall.

Options:

A.  

True

B.  

False

Discussion 0
Question # 16

In the following options, which of the two attacks use similar attack methods, they will generate a large number of useless response packets, occupying network bandwidth,

Consume equipment resources?

Options:

A.  

Fraggle and Smurt

B.  

Land and Smurf

C.  

Fraggle and Land

155955cc-666171a2-20fac832-0c042c0423

D.  

Teardrop and Land35

Discussion 0
Question # 17

Which of the following files can the sandbox detect? (multiple choice)

Options:

A.  

www file

B.  

PE file

C.  

Picture file

D.  

Mail

Discussion 0
Question # 18

Intrusion detection is a network security technology used to detect any damage or attempt to damage the confidentiality, integrity or availability of the system. Which of the following

What is the content of the intrusion detection knowledge base?

Options:

A.  

Complete virus sample

B.  

Complete Trojan Horse

C.  

Specific behavior patterns

D.  

Security Policy

Discussion 0
Question # 19

In the big data intelligent security analysis platform, it is necessary to collect data from data sources, and then complete a series of actions such as data processing, detection and analysis, etc.

do. Which of the following options does not belong to the action that needs to be completed in the data processing part?

155955cc-666171a2-20fac832-0c042c0422

Options:

A.  

Data preprocessing

B.  

Threat determination

C.  

Distributed storage

D.  

Distributed index

Discussion 0
Question # 20

Which of the following types of attacks are DDoS attacks? 2I

Options:

A.  

Single packet attack

B.  

Floating child attack

C.  

Malformed message attack

D.  

Snooping scan attack

Discussion 0

H12-722 PDF

H12-722 PDF (Printable)
$46.5
$154.99

H12-722 Testing Engine

H12-722 PDF (Printable)
$51
$169.99

H12-722 PDF + Testing Engine

H12-722 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions


