Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 5 - FortiSwitch 7.6 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE5_FSW_AD-7.6 domain

Last Update 1 day ago
Total Questions : 114

Start with our free NSE5_FSW_AD-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Network Security Expert exam. Each NSE5_FSW_AD-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE5_FSW_AD-7.6 PDF

NSE5_FSW_AD-7.6 PDF (Printable)
$46.5
$154.99

NSE5_FSW_AD-7.6 Testing Engine

NSE5_FSW_AD-7.6 PDF (Printable)
$51
$169.99

NSE5_FSW_AD-7.6 PDF + Testing Engine

NSE5_FSW_AD-7.6 PDF (Printable)
$63.9
$212.99
Question # 11

How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?

Options:

A.  

Only high-end FortiSwitch models support ACL.

B.  

ACL can be used only at the prelookup stage in the traffic processing pipeline.

C.  

Classifiers enable matching traffic based only on the VLAN I

D.  

D.  

FortiSwitch checks ACL policies only from top to bottom.

Discussion 0
Question # 12

Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

Options:

A.  

You must add port24 native VLAN as an allowed VLAN on internal.

B.  

You must add VLAN ID 200 to the allowed VLANS on internal.

C.  

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.  

You should use VLAN ID 4094 as the native VLAN on port24.

Discussion 0
Question # 13

Which statement about the use of the switch port analyzer (SPAN) packet capture method is true?

Options:

A.  

Mirrored traffic can be sent across multiple switches.

B.  

SPAN can be configured only on a standalone FortiSwitch.

C.  

Traffic on the management interface can be mirrored and captured by the monitoring device.

D.  

The monitoring device must be connected to the same switch where the traffic is being mirrored

Discussion 0
Question # 14

(Full question statement start from here)

When you change FortiSwitch management mode fromstandalonetomanaged, what happens to the existing standalone configuration? (Choose one answer)

Options:

A.  

FortiSwitch registers to FortiSwitch Cloud to save a copy before managing with FortiGate.

B.  

FortiSwitch merges the existing standalone configuration with the default FortiLink configuration.

C.  

FortiSwitch saves the standalone configuration and changes to the default FortiLink configuration.

D.  

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

Discussion 0
Question # 15

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.  

Use a migration tool based on python script to convert the configuration

B.  

Enable the Forti-link setting on FortiSwitch before the authorization process

C.  

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.  

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Discussion 0
Question # 16

You are designing a FortiSwitch backbone where every FortiSwitch device must connect to every other FortiSwitch for maximum redundancy. To maintain connectivity while preventing loops, which protocol or feature must you configure on the switches? (Choose one answer)

Options:

A.  

Multichassis link aggregation group (MCLAG)

B.  

Spanning Tree Protocol (STP)

C.  

Full mesh high availability (HA)

D.  

Link aggregation group (LAG)

Discussion 0
Question # 17

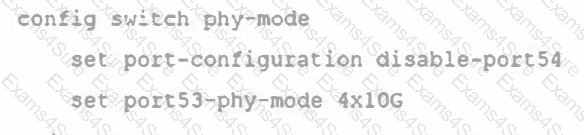
Exhibit.

Question # 17

What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.  

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.  

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.  

The port full speed prior the split was 100G SFP+

D.  

The split port can be assigned to native VLAN

Discussion 0
Question # 18

Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)

Options:

A.  

Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.

B.  

switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.

C.  

By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.

D.  

Settings related to DHCP option 82 are only configurable through the CLI

Discussion 0
Question # 19

An administrator needs to deploy managed FortiSwitch devices in a remote location where multiple VLANs must be utilized to segment devices. No Layer 3 switch or router is present. The the only WAN connectivity is the router provided by the ISP connected to the public internet.

Which two items will the administrator need to use? (Choose two.)

Options:

A.  

A FortiSwitch interface connected to the ISP router configured with fortilink-13-mode enabled.

B.  

FortiSwitch and FortiGate devices configured with VXLAN interfaces.

C.  

FortiSwitch devices configured with NAT disabled.

D.  

FortiSwitch devices that have the required internal hardware for this configuration.

E.  

FortiSwitch and FortiGate devices configured with IPsec interfaces.

Discussion 0
Question # 20

Refer to the exhibit.

What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)

Options:

A.  

Maximum value to accept clients DHCP request is configured as per DHCP server range.

B.  

FortiSwitch is configured to trust DHCP replies coming on FortiLink interface.

C.  

DHCP clients that are trusted by DHCP snooping configured is only one.

D.  

Global configuration for DHCP snooping is set to forward DHCP client requests on all ports in the VLAN.

Discussion 0

Free Exams Sample Questions