Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 5 - FortiSwitch 7.6 Administrator Practice Questions

Exams4sure Dumps

Exam style questions across every NSE5_FSW_AD-7.6 domain

Last Update 1 day ago
Total Questions : 114

Start with our free NSE5_FSW_AD-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Network Security Expert exam. Each NSE5_FSW_AD-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.

NSE5_FSW_AD-7.6 PDF

NSE5_FSW_AD-7.6 PDF (Printable)
$46.5
$154.99

NSE5_FSW_AD-7.6 Testing Engine

NSE5_FSW_AD-7.6 PDF (Printable)
$51
$169.99

NSE5_FSW_AD-7.6 PDF + Testing Engine

NSE5_FSW_AD-7.6 PDF (Printable)
$63.9
$212.99
Question # 21

Refer to the exhibit.

Question # 21

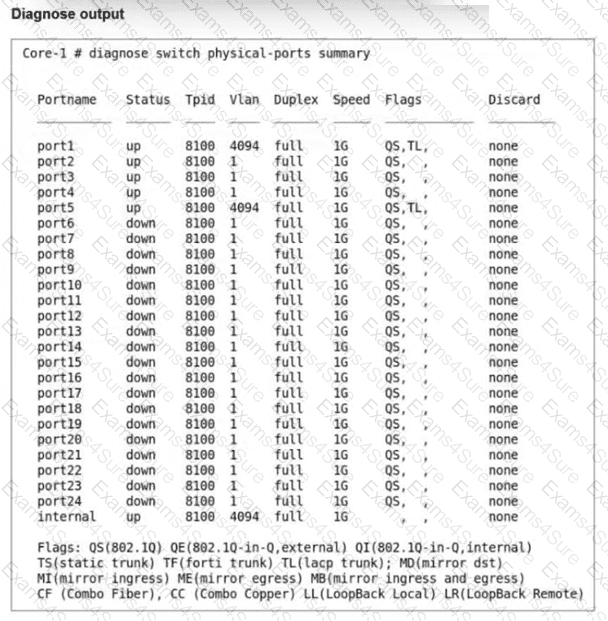
The command diagnose switch physical-ports summary is executed on FortiSwitch.

Based on the VLAN assignments shown in the output, what is the most likely management configuration of this FortiSwitch? (Choose one answer)

Options:

A.  

FortiSwitch is managed by FortiSwitch Cloud.

B.  

FortiSwitch is managed by FortiGate.

C.  

FortiSwitch is operating in standalone mode.

D.  

FortiSwitch is operating in local mode.

Discussion 0
Question # 22

Refer to the exhibits.

Question # 22

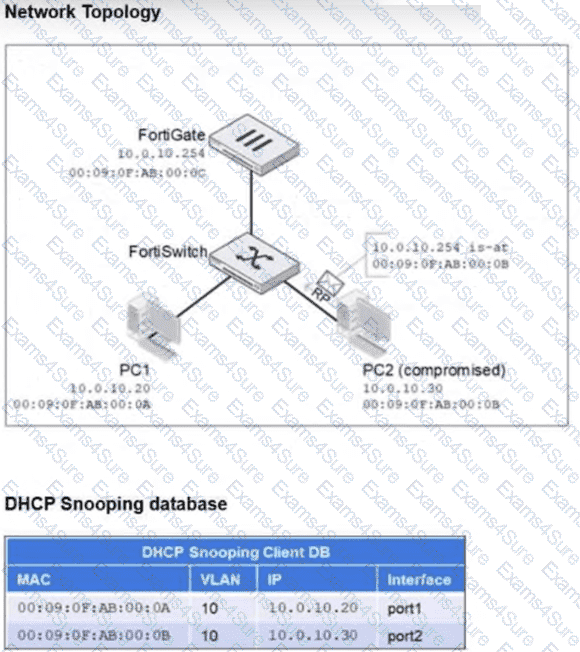
All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)

Options:

A.  

Forward the ARP replies because there are no IPSG bindings blocking them.

B.  

Accept the ARP replies because the VLAN has DAI enabled and FortiGate is a trusted DHCP server.

C.  

Forward the ARP replies to all VLAN 10 ports because DAI is only active on trusted ports.

D.  

Drop the ARP replies because they fail DAI validation against the DHCP snooping database.

Discussion 0
Question # 23

Which is a requirement to enable SNMP v2c on a managed FortiSwitch?

Options:

A.  

Create an SNMP user to use for authentication and encryption.

B.  

Specify an SNMP host to send traps to.

C.  

Enable an SNMP v3 to handle traps messages with SNMP hosts.

D.  

Configure SNMP agent and communities.

Discussion 0
Question # 24

FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?

Options:

A.  

The handshake process timed out before FortiSwitch responded.

B.  

DTLS client hello had the incorrect pre-shared key.

C.  

The CAPWAP tunnel failed to come up due to a mismatch in time.

D.  

FortiSwitch has disabled FortiLink and is only managed as a standalone.

Discussion 0
Question # 25

Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three answers)

Options:

A.  

Assign the VLAN ID

B.  

Quarantine devices

C.  

Traffic processing

D.  

Set outer VLAN tags

E.  

QoS

Discussion 0
Question # 26

(Full question statement start from here)

How does enabling an IGMP snooping proxy on FortiSwitch help reduce the number of IGMP reports processed by the IGMP querier? (Choose one answer)

Options:

A.  

By converting IGMP reports into broadcast packets to reach all VLAN members

B.  

By converting IGMP traffic to unicast

C.  

By suppressing duplicate IGMP reports within the VLAN

D.  

By forwarding IGMP reports only when the first member joins and the last member leaves

Discussion 0
Question # 27

You are deploying a small office network with a single FortiGate and a single FortiSwitch. The office currently has moderate traffic, but the IT team expects the network to grow in the near future, adding more FortiSwitch devices and endpoints. Which FortiLink configuration should you deploy to provide the best combination of current performance and scalability for future growth? (Choose one answer)

Options:

A.  

Configure FortiLink using hardware-based switch interfaces.1

B.  

Configure FortiLink using software-based switch interfaces.

C.  

Configure FortiLink as a link aggregation group (LAG) interface.

D.  

Configure FortiLink as a multichassis LAG (MCLAG) interface.2

Discussion 0
Question # 28

What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)

Options:

A.  

FortiSwitch does not retain its time after a reboot, which gets reset after each reboot.

B.  

FortiSwitch will not be able to become an NTP server for downstream devices.

C.  

FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel.

D.  

FortiSwitch will not allow other FortiSwitch devices in the chain be discovered by FortiGate.

Discussion 0
Question # 29

What happens if FortiSwitch fails to discover either FortiEdge Cloud or a FortiGate with FortiLink?

Options:

A.  

It switches to FortiLink mode by default.

B.  

It remains in local management mode.

C.  

It requires manual reimaging.

D.  

It disables auto-network.

Discussion 0
Question # 30

(Full question statement start from here)

Refer to the exhibits.
Question # 30

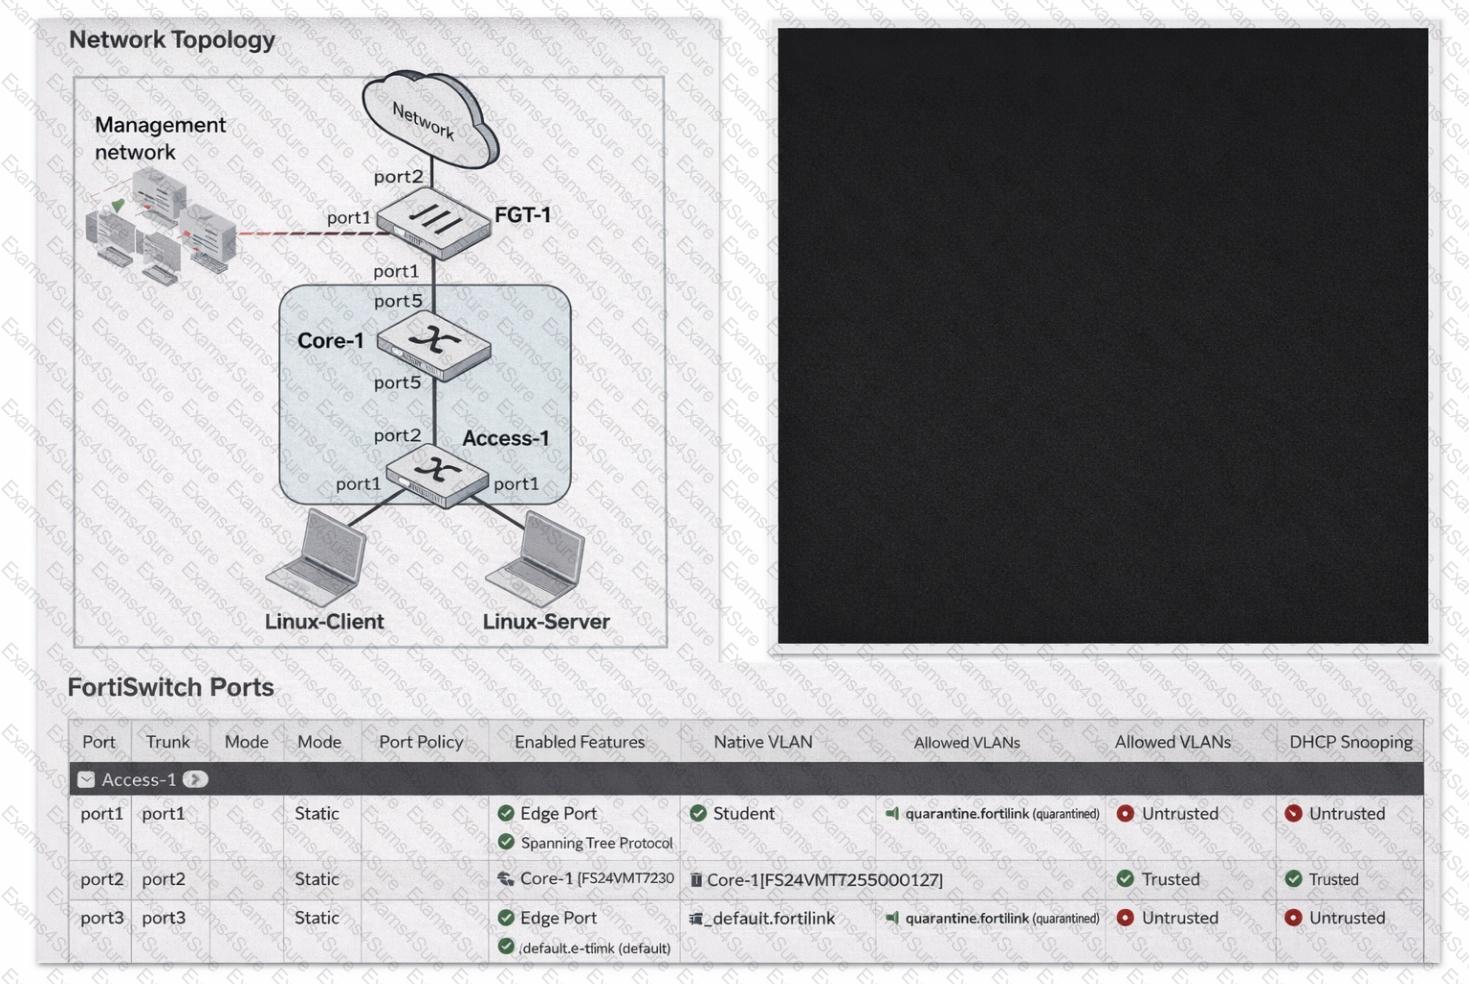
You enable Dynamic Host Configuration Protocol (DHCP) snooping on the VLAN,Student. The Linux-Client VM sends DHCP requests, and tcpdump confirms the broadcasts. However, the Linux-Server VM, acting as a DHCP server, receives no DHCP traffic. What is the most likely cause of this intra-VLAN traffic being blocked? (Choose one answer)


Options:

A.  

The DHCP requests are being sent on the wrong VLAN.

B.  

Port1 is configured as an untrusted port.

C.  

Port4 is not configured as a trusted port.

D.  

The Student VLAN must be configured as an allowed VLAN on port1.

Discussion 0

Free Exams Sample Questions