
Question # 11
Refer to the exhibit.
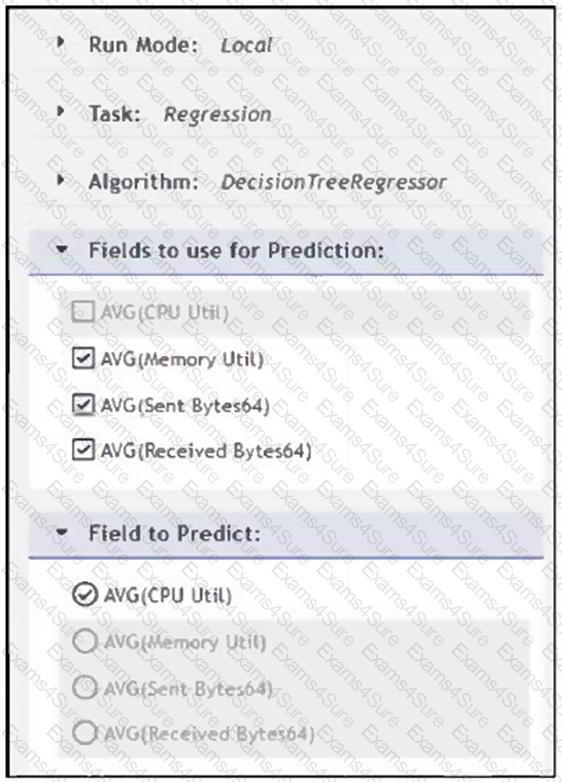
What will happen when a device being analyzed by the machine learning configuration shown in the exhibit has consistently high memory utilization?
Question # 13
When configuring anomaly detection machine learning, in which step must you select the fields to analyze?
Question # 14
Refer to the exhibit.

A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword " udp " . However, they are getting no results from the search, which they know should be available. Based on the filter shown in the exhibit, why are there no search results?




