Easter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: e4s75best

Free Fortinet NSE 6 - FortiSIEM 7.4 Analyst Practice Questions

Question # 1

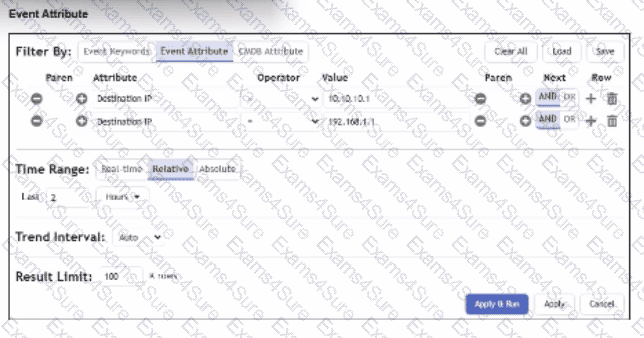
Refer to the exhibit.
Question # 1

A FortiSIEM analyst is investigating an issue by examining events to two destination IP addresses. However, the analyst is not getting any results from the search.

Based on the selected filter shown in the exhibit, why is the search returning no results?

Options:

A.  

Parentheses are missing between the two items.

B.  

The wrong Boolean operator is selected in the Next column.

C.  

The wrong option is selected in the Operator column.

D.  

An invalid IP address is typed in the Value column.

Discussion 0
Question # 2

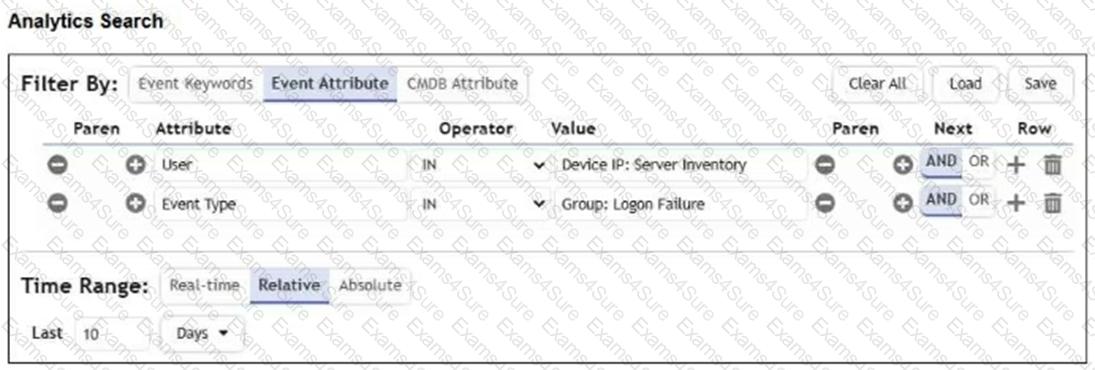
Refer to the exhibit.

Question # 2

The analyst is troubleshooting the analytics query shown in the exhibit.

Why is this search not producing any results?

Options:

A.  

The Time Range is set incorrectly.

B.  

The inner and outer nested query attribute types do not match.

C.  

You cannot reference User and Event Type attributes in the same search.

D.  

The Boolean operator is wrong between the attributes.

Discussion 0
Question # 3

How can you query the configuration management database (CMDB) in an analytics search?

Options:

A.  

Click Value > Select from CMD

B.  

B.  

On the CMDB tab, select an entry, and then click Create Search.

C.  

On the Admin tab, click CMDB Search.

D.  

Click Attribute > Select from CMD

B.  

Discussion 0
Question # 4

Refer to the exhibit.

Question # 4

If a rule containing the automation policy shown in the exhibit triggers, what will happen?

Options:

A.  

Associated source IP addresses will be blocked on devices in the Aviation organization.

B.  

Associated source IP addresses will be blocked on all FortiGate firewalls.

C.  

Associated source IP addresses will be blocked on devices in the Network CMDB group.

D.  

Associated source IP addresses will be blocked on two FortiGate firewalls.

Discussion 0
Question # 5

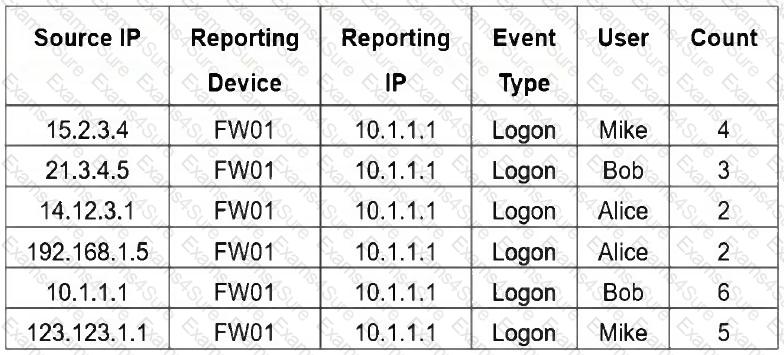
Refer to the exhibit.

Question # 5

If you group the events by User , Source IP , and Count attributes, how many results will FortiSIEM display?

Options:

A.  

Two

B.  

Six

C.  

Three

D.  

Five

E.  

Four

Discussion 0
Question # 6

Refer to the exhibit.

Question # 6

Which section contains the subpattern configuration that determines how many matching events are needed to trigger the rule?

Options:

A.  

Aggregate

B.  

Group By

C.  

Actions

D.  

Filters

Discussion 0
Question # 7

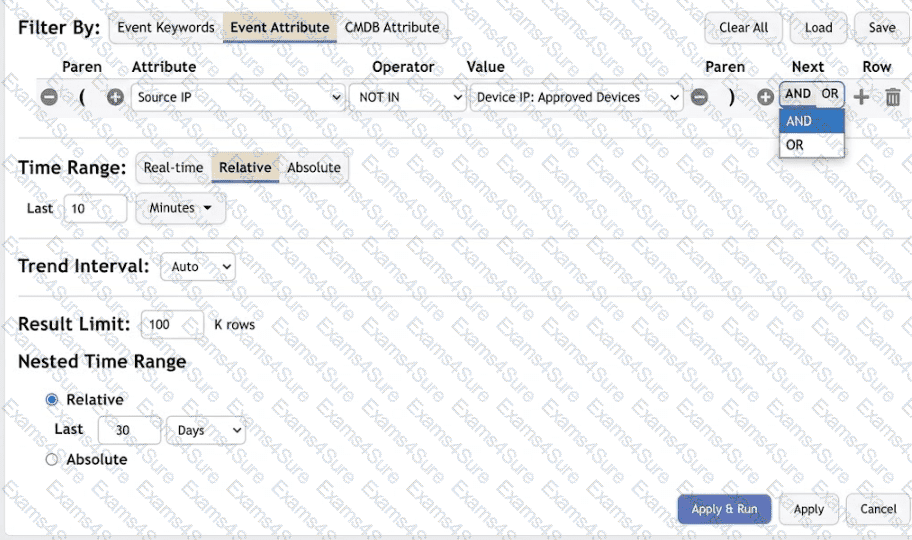
Refer to the exhibit.

Question # 7

Which statement about the time range settings defined in the nested query is accurate? (Choose one answer)

Options:

A.  

FortiSIEM will list source IP addresses found in the last 10 minutes of events from each day in the Approved Devices report from the last 30 days.

B.  

FortiSIEM will search in real time using 10-minute blocks for a source IP address that is not in the Approved Devices report from the last 30 days.

C.  

FortiSIEM will search the last 30 days of events for a source IP address that is not in the Approved Devices report.

D.  

FortiSIEM will search the last 10 minutes of events for a source IP address that is not in the Approved Devices report from the last 30 days.

Discussion 0
Question # 8

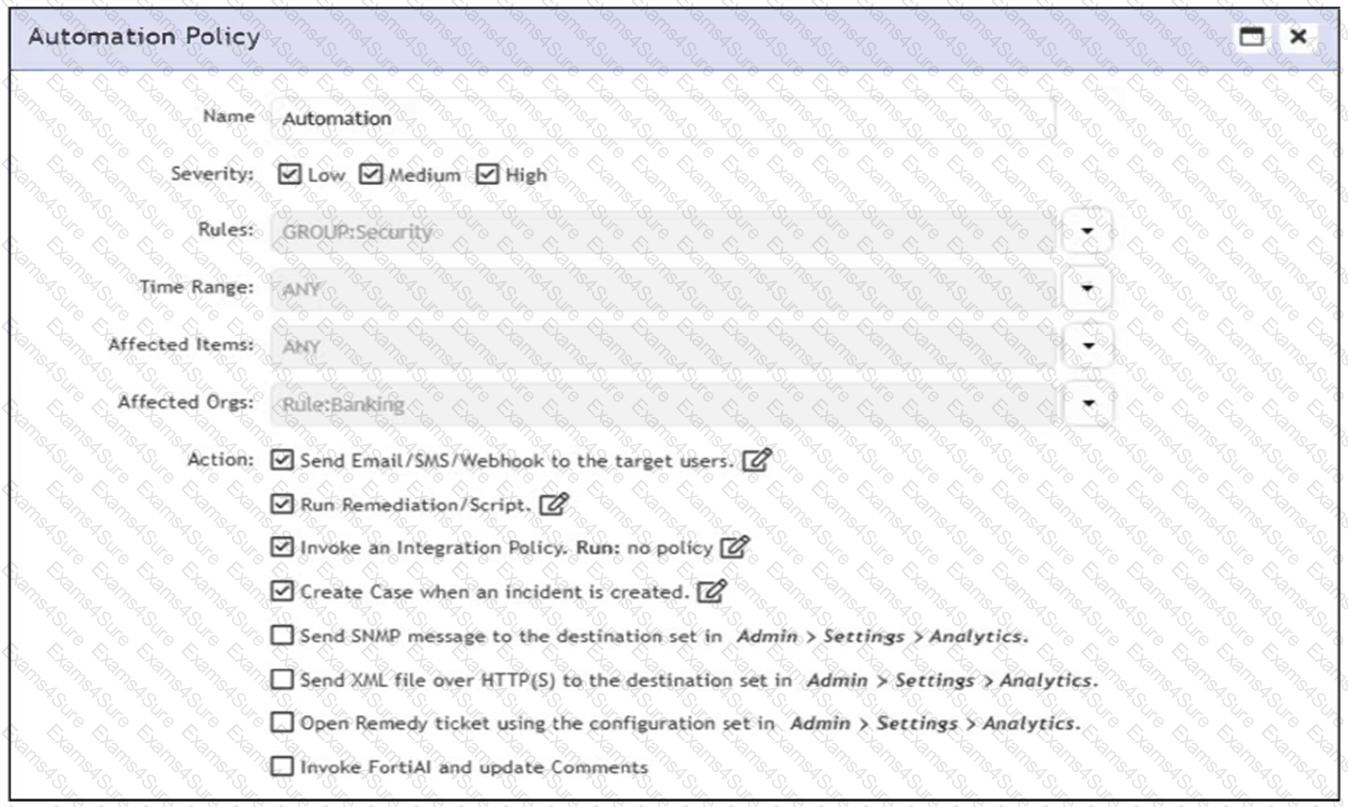
Refer to the exhibit.

Question # 8

According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?

Options:

A.  

FortiSIEM runs the remediation script, because that takes precedence over all other options.

B.  

FortiSIEM performs all selected actions.

C.  

FortiSIEM fails to the integration policy, because no policy is defined.

D.  

FortiSIEM sends an email, because that is first on the list.

Discussion 0
Question # 9

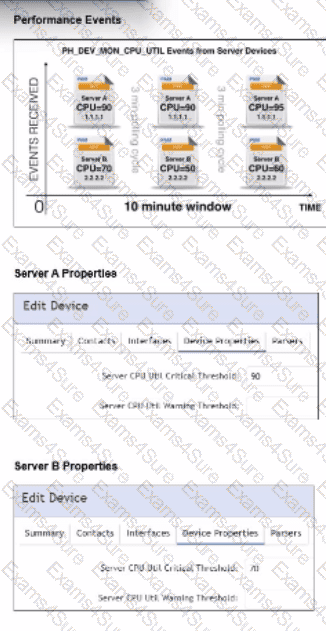
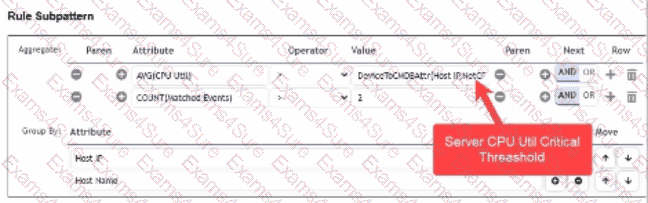
Refer to the exhibits.

Question # 9

Question # 9

Three events are collected over 10 minutes from two servers: Server A and Server

B.  

Based on the settings for the rule subpattern and a 10-minute condition window, how many incidents will the servers generate?

Options:

A.  

Server A will generate one incident and Server B will generate one incident.

B.  

Server A will not generate any incidents and server B will generate one incident.

C.  

Server A will not generate any incidents and Server B will not generate any incidents.

D.  

Server A will generate one incident and Server B will not generate any incidents.

Discussion 0
Question # 10

Refer to the exhibit.

Question # 10

An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.

What is wrong with the rule conditions?

Options:

A.  

The Event Type refers to a CMDB lookup and should be an Event lookup.

B.  

The Destination Host Name value is not fully qualified.

C.  

The Group By attributes restricts which events are counted.

D.  

The Aggregate attribute is too restrictive.

Discussion 0

NSE6_FSM_AN-7.4 PDF

NSE6_FSM_AN-7.4 PDF (Printable)
$38.75
$154.99

NSE6_FSM_AN-7.4 Testing Engine

NSE6_FSM_AN-7.4 PDF (Printable)
$42.5
$169.99

NSE6_FSM_AN-7.4 PDF + Testing Engine

NSE6_FSM_AN-7.4 PDF (Printable)
$53.25
$212.99
Exams4sure Dumps

Exam style questions across every NSE6_FSM_AN-7.4 domain

Last Update 16 hours ago
Total Questions : 48

Start with our free NSE6_FSM_AN-7.4 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real NSE 6 Network Security Specialist exam. Each NSE6_FSM_AN-7.4 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.


Free Exams Sample Questions