Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 7 - FortiSASE 26 Architect Practice Questions

Question # 11

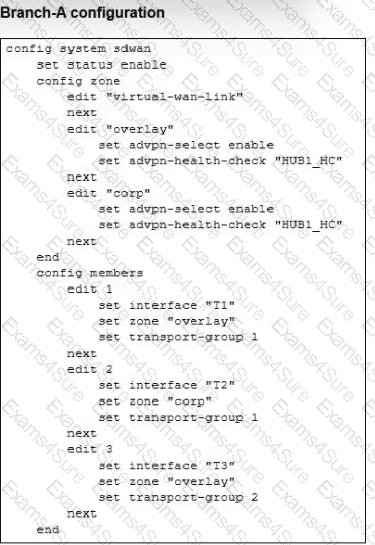
Refer to the exhibits.

The SD-WAN zones and members configuration of two branch devices are shown.

The two branch devices are part of the same hub-and-spoke topology and connect to the same hub. The devices are configured to allow auto-discovery VPN (ADVPN). The configuration on the hub allows the initial communication between the two spokes.

When traffic flows require it, between which interfaces can the devices establish shortcuts?
Question # 11

Exhibit — Branch-A SD-WAN zone and transport group

The visible recording shows the Branch-A configuration; the Branch-B configuration is not displayed in the captured video frame.

Options:

A.  

Any interface in the overlay zones

B.  

Between T2 on Branch-A and TB on Branch-B

C.  

Between T1 on Branch-A and TA on Branch-B

D.  

Any interface that belongs to the same zone

Discussion 0
Question # 12

What are three characteristics of the provisioning templates available on FortiManager? (Choose three.)

Options:

A.  

A CLI template can be of type CLI script or Perl script.

B.  

Each template group can contain up to three IPsec tunnel templates.

C.  

A template group can include a system template and an SD-WAN template.

D.  

A CLI template group can contain CLI templates of different types.

E.  

CLI templates are applied in order, from top to bottom.

Discussion 0
Question # 13

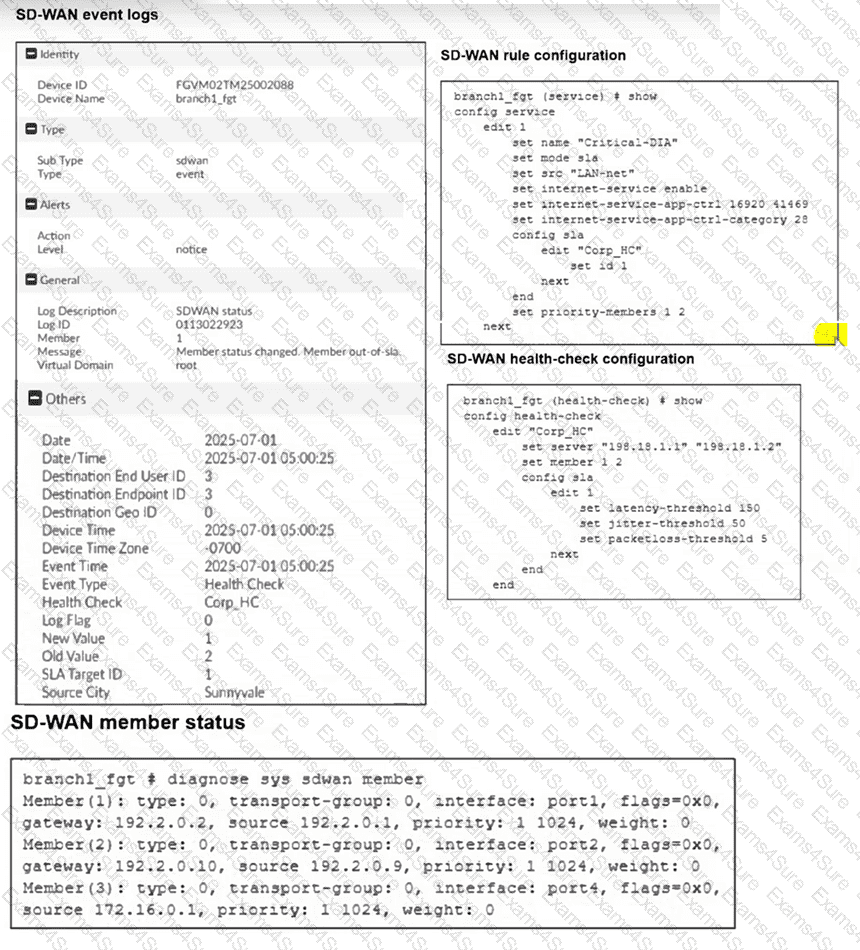
Refer to the exhibits. Two SD-WAN event logs, the member status, the SD-WAN rule configuration, and the health-check configuration for a FortiGate device are shown. Immediately after the log messages are displayed, how will the FortiGate steer the traffic based on the information shown in the exhibits? Choose one answer.
Question # 13

Exhibit 1

Options:

A.  

FortiGate skips SD-WAN rule ID 1.

B.  

FortiGate uses port2 to steer the traffic for SD-WAN rule ID 1.

C.  

FortiGate uses port1 to steer the traffic for SD-WAN rule ID 1.

D.  

FortiGate uses port1 or port2 to steer the traffic for SD-WAN rule ID 1.

Discussion 0
Question # 14

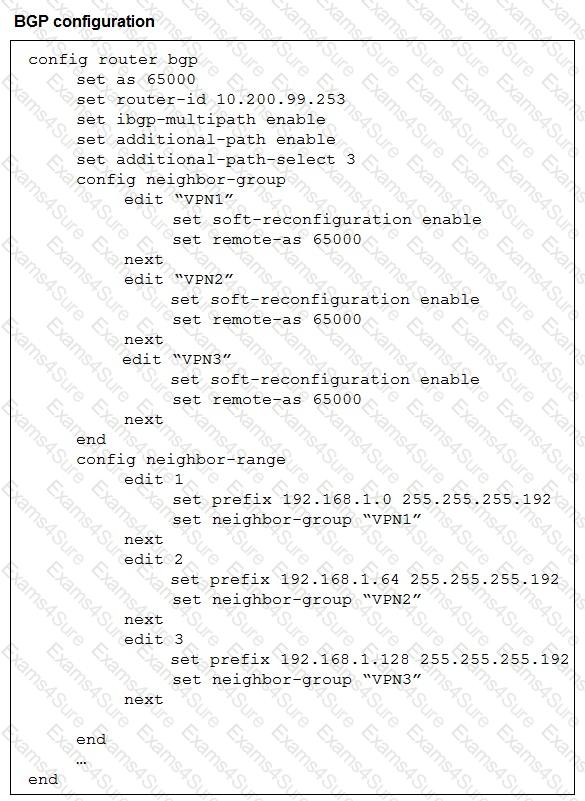
Refer to the exhibit. The exhibit shows the BGP configuration on the hub in a hub-and-spoke topology. The administrator wants BGP to advertise prefixes from spokes to other spokes over the IPsec overlays, including additional paths. However, when looking at the spoke routing table, the administrator does not see the prefixes from other spokes and the additional paths Which three settings must the administrator configure inside each BGP neighbor group so spokes can learn the prefixes of other spokes and their additional paths? (Choose three.)
Question # 14

Exhibit 1

Options:

A.  

Set additional-path to send

B.  

Set additional-path to forward

C.  

Enable route-reflector-server

D.  

Enable route-reflector-client.

E.  

Set adv-additional-path to the number of additional paths to advertise.

Discussion 0
Question # 15

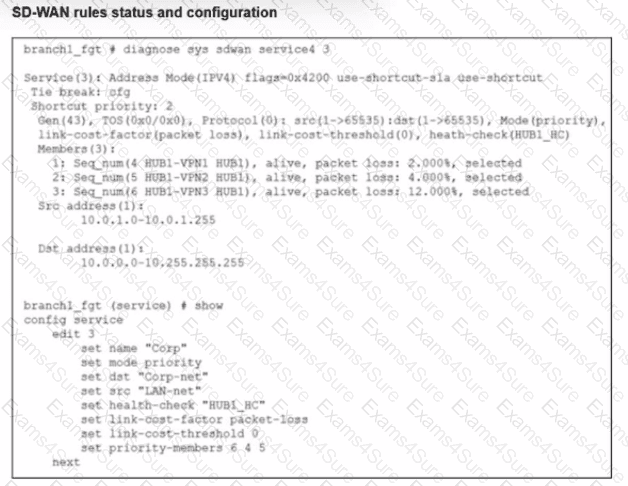
Refer to the exhibit, which shows the SD-WAN rule status and configuration. Based on the exhibit, which change in the measured packet loss will make HUB1-VPN3 the new preferred member?
Question # 15

Exhibit 1

Options:

A.  

When HUB1-VPN1 has 4% packet loss

B.  

When HUB1-VPN1 has 12% packet loss

C.  

When HUB1-VPN3 has 4% packet loss

D.  

When all three members have the same packet loss

Discussion 0
Question # 16

Refer to the exhibits. You use FortiManager to manage the branch devices and configure the SD-WAN template. You have configured direct internet access (DIA) for the IT department users. Now. you must configure secure internet access (SIA) for all local LAN users and have set the firewall policies as shown in the second exhibit. Then, when you use the install wizard to install the configuration and the policy package on the branch devices, FortiManager reports an error as shown in the third exhibit. Which statement describes why FortiManager could not install the configuration on the branches?
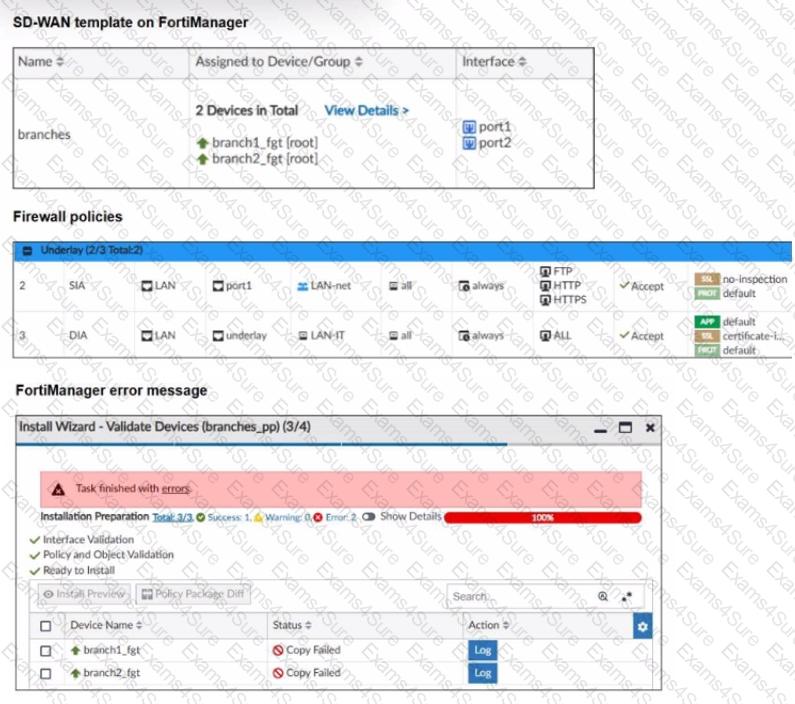
Question # 16

Exhibit 1

Options:

A.  

You must direct SIA traffic to a VPN tunnel.

B.  

You cannot install firewall policies that reference an SD-WAN zone.

C.  

You cannot install firewall policies that reference an SD-WAN member.

D.  

You cannot install SIA and DIA rules on the same device.

Discussion 0
Question # 17

Refer to the exhibits.

The administrator increases the member priority on port2 to 20.

Assuming the route egressing port2 is still valid, upon configuration changes and the receipt of new packets.

Which two actions does FortiGate perform on existing sessions established over port2? (Choose two.)
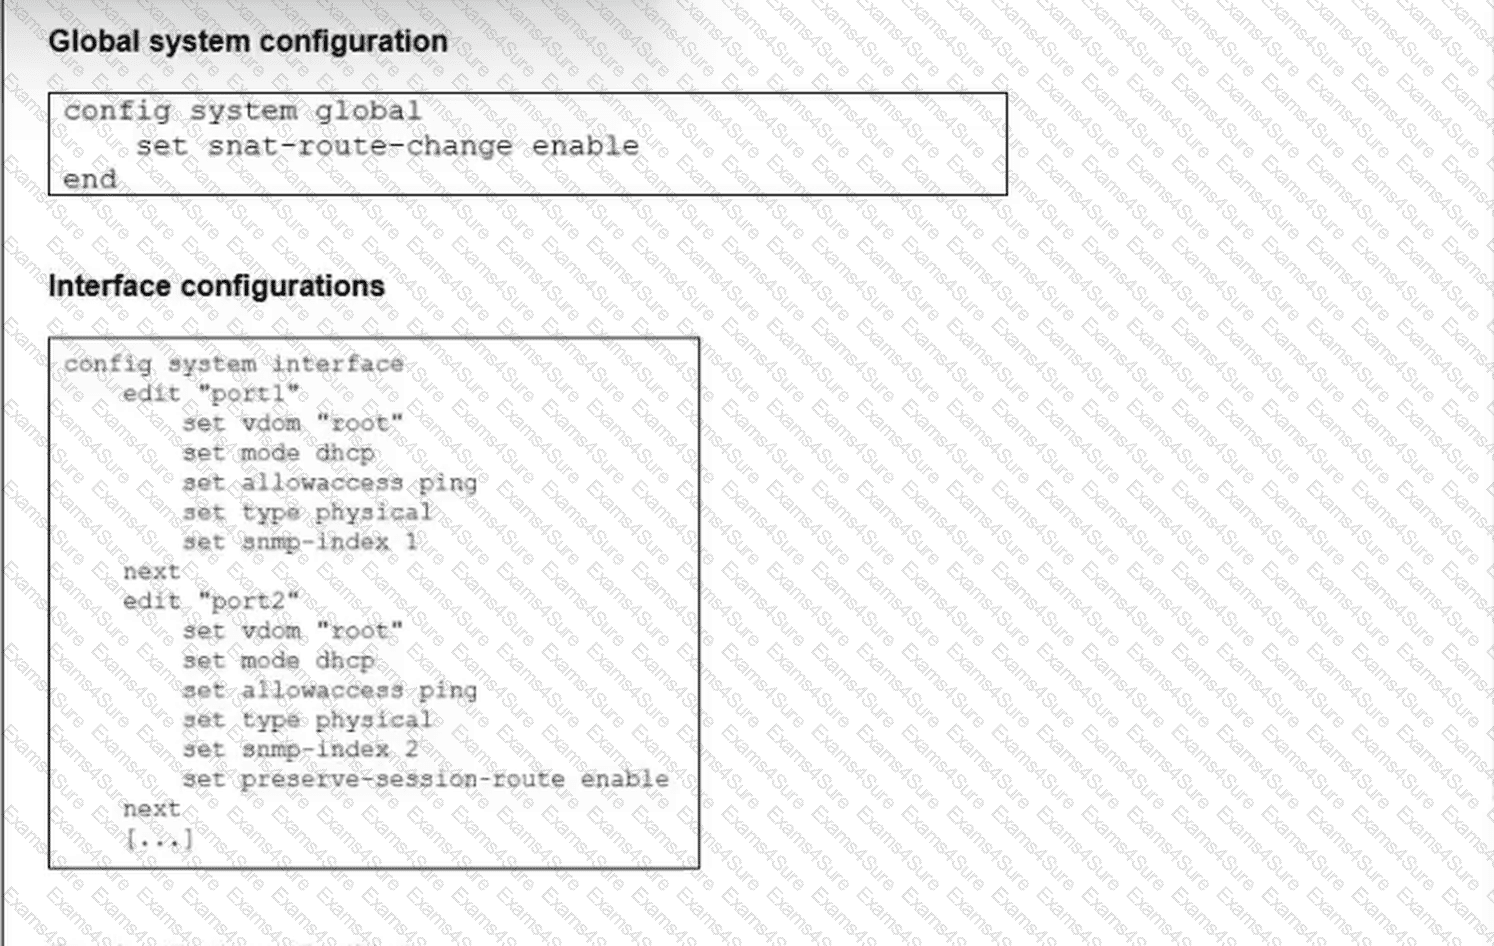
Question # 17

Exhibit 1 — Global system and interface configuration
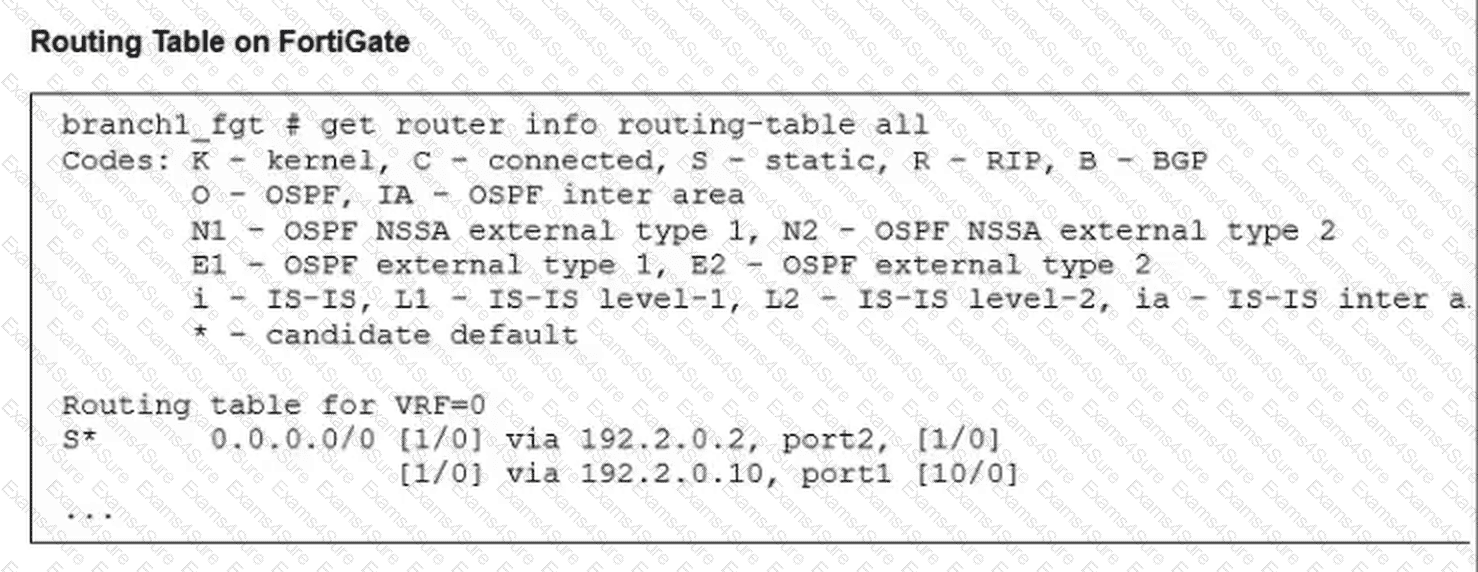
Question # 17

Exhibit 2 — FortiGate routing table

Options:

A.  

FortiGate updates the gateway information of the sessions with SNAT so that they use port1 instead of port2.

B.  

FortiGate flags all source network address translation (SNAT) sessions as dirty only if the administrator has assigned an IP pool to the firewall policies with NAT.

C.  

FortiGate routes new sessions over port1.

D.  

FortiGate flags all sessions as dirty.

E.  

FortiGate continues routing all existing sessions over port2.

Discussion 0
Question # 18

Which two statements about on-ramp tunnels on FortiSASE are correct? (Choose two.)

Options:

A.  

A branch device can connect to two or more on-ramp locations.

B.  

SSL deep inspection for site-based users is fully functional without installing the FortiSASE certificate authority certificate.

C.  

Only FortiExtender and FortiAP devices are supported for on-ramp tunnels.

D.  

The branch on-ramp and secure private access (SPA) features share the same BGP configuration.

Discussion 0
Question # 19

SD-WAN interacts with many other FortiGate features. Some of them are required to allow SD-WAN to steer the traffic. Which three configuration elements that you must configure before FortiGate can steer traffic according to SD-WAN rules? (Choose three.)

Options:

A.  

Firewall policies

B.  

Interfaces

C.  

Security profiles

D.  

Traffic shaping

E.  

Routing

Discussion 0
Question # 20

Refer to the exhibit. The administrator configured the SD-WAN rule ID 4 with two members (port1 and port2) and strategy lowest cost (SLA). What are the two characteristics of the session shown in the exhibit? (Choose two.)
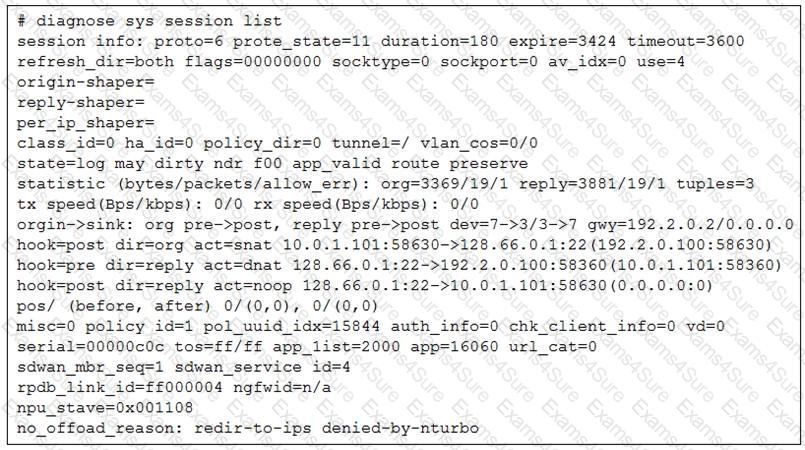
Question # 20

Exhibit 1

Options:

A.  

FortiGate steered this flow according to an SD-WAN rule 4.

B.  

FortiGate will never re-evaluate this session.

C.  

FortiGate steered this flow according to the application detected and the outgoing interface is port3.

D.  

FortiGate will re-evaluate this session if the outgoing interface goes down.

Discussion 0

NSE7_SSE_AR-26 PDF

NSE7_SSE_AR-26 PDF (Printable)
$46.5
$154.99

NSE7_SSE_AR-26 Testing Engine

NSE7_SSE_AR-26 PDF (Printable)
$51
$169.99

NSE7_SSE_AR-26 PDF + Testing Engine

NSE7_SSE_AR-26 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions