Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Fortinet NSE 7 - FortiSASE 26 Architect Practice Questions

Question # 1

Which three factors about SLA targets and SD-WAN rules should you consider when configuring SD-WAN rules? (Choose three.)

Options:

A.  

Member metrics are measured only if a rule uses the SLA target.

B.  

SLA targets are used only by SD-WAN rules that are configured with a Lowest Cost (SLA) strategy.

C.  

SD-WAN rules can use SLA targets to check whether the preferred members meet the SLA requirements.

D.  

When configuring an SD-WAN rule, you can select multiple SLA targets if they are from the same performance SL

A.  

E.  

When configuring an SD-WAN rule, you can select multiple SLA targets from different performance SLAs.

Discussion 0
Question # 2

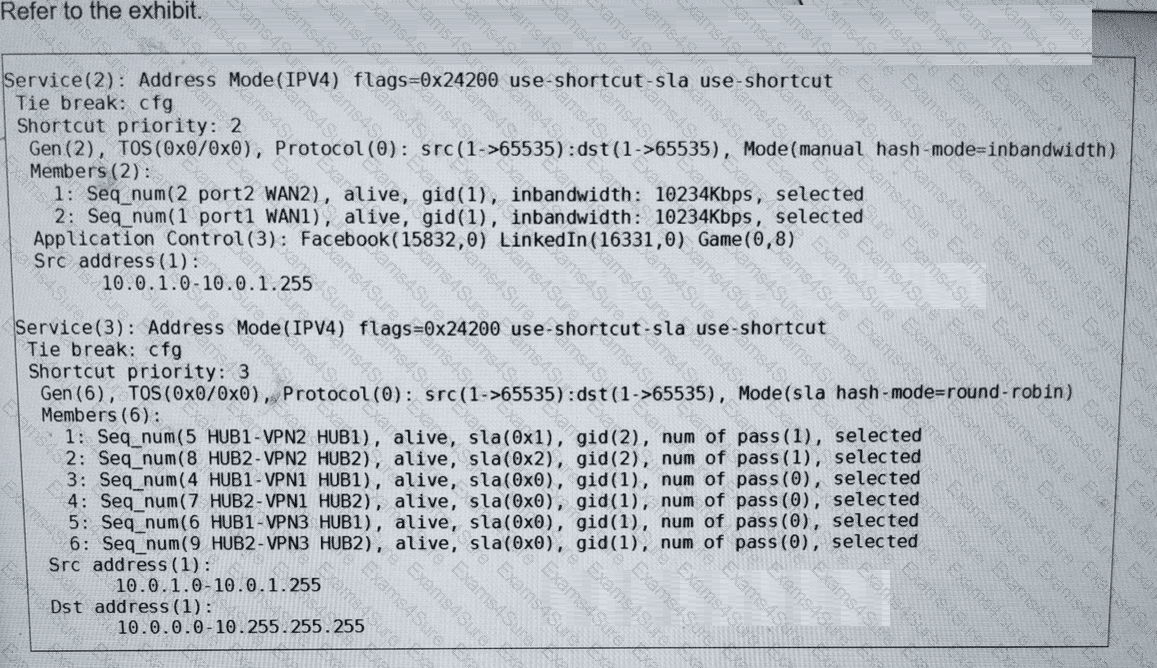
Refer to the exhibit. The administrator configured two SD-WAN rules to load balance the traffic. Which interfaces does FortiGate use to steer the traffic from 10.0.1.124 to 10.0.0.254? Choose one answer.
Question # 2

Exhibit 1

Options:

A.  

HUB2-VPN2

B.  

HUB1-VPN2 or HUB2-VPN2

C.  

port1 or port2

D.  

Any interface in the HUB1 or HUB2 zones

Discussion 0
Question # 3

An SD-WAN member is no longer used to steer SD-WAN traffic. The administrator updated the SD-WAN configuration and deleted the unused member. After the configuration update, users report that some destinations are unreachable. You confirm that the affected flow does not match an SD-WAN rule. What could be a possible cause of the traffic interruption?

Options:

A.  

FortiGate, with SD-WAN enabled, cannot route traffic through interfaces that are not SD-WAN members.

B.  

FortiGate can remove some static routes associated with an interface when the member is removed from SD-WAN.

C.  

FortiGate removes the layer 3 settings for interfaces that are removed from the SD-WAN configuration.

D.  

FortiGate administratively brings down interfaces when they are removed from the SD-WAN configuration.

Discussion 0
Question # 4

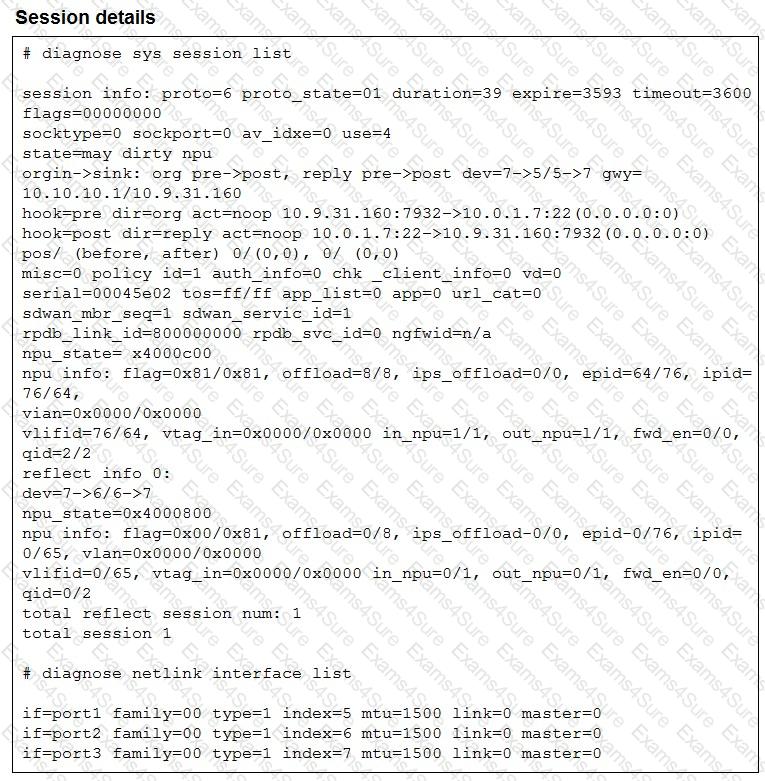
Refer to the exhibit. The exhibit shows the details of a session and the index numbers of some relevant interfaces on a FortiGate device that supports hardware offloading. Based on the information shown in the exhibits, which two conclusions can you draw? (Choose two.)
Question # 4

Exhibit 1

Options:

A.  

By default, FortiGate offloads symmetric and asymmetric flows.

B.  

The original direction of the symmetric traffic flows from port3 to port2.

C.  

The reply direction of the asymmetric traffic flows from port2 to port3.

D.  

The auxiliary session can be offloaded to hardware.

Discussion 0
Question # 5

What is the benefit of branch on-ramp deployment with FortiSASE? (Choose one answer.)

Options:

A.  

To secure internet traffic for small remote offices.

B.  

To provide access to private applications using the bookmark portal.

C.  

To manage branch location endpoints.

D.  

To provide device compliance checks using zero trust network access (ZTNA) tags.

Discussion 0
Question # 6

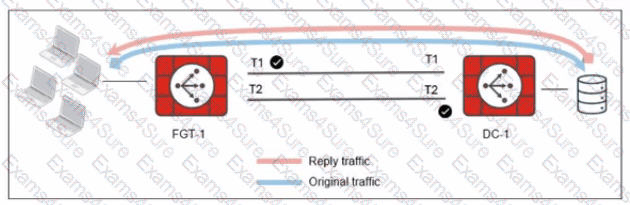
Refer to the exhibit. The administrator analyzed the traffic between a branch FortiGate and the server located in the data center, and noticed the behavior shown in the diagram. When the LAN clients located behind FGT1 establish a session to a server behind DC-1, the administrator observes that, on DC-1, the reply traffic is routed overT2. even though T1 is the preferred member in the matching SD-WAN rule. What can the administrator do to instruct DC-1 to route the reply traffic through the member with the best performance?
Question # 6

Exhibit 1

Options:

A.  

Enable snat-route-change under config system global.

B.  

Enable reply-session under config system sdwan.

C.  

Enable auxiliary-session under config system settings.

D.  

FortiGate route lookup for reply traffic only considers routes over the original ingress interface.

Discussion 0
Question # 7

Refer to the exhibit.

Question # 7

How does FortiGate handle the ICMP traffic with the source IP address 10.0.1.125 and the destination IP address 128.66.0.125?

Options:

A.  

FortiGate drops the traffic flow.

B.  

FortiGate load balances the traffic flow through port7 and port8.

C.  

FortiGate steers the traffic flow through port2.

D.  

FortiGate routes the traffic flow according to the forwarding information base (FIB).

Discussion 0
Question # 8

You configure the overlay tunnels for an SD-WAN hub-and-spoke topology defined with IPsec tunnels, BGP on loopback, and dynamic BGP.

Which are two recommended IPsec settings for this topology? (Choose two.)

Options:

A.  

On the spoke, set the parameter net-device to enable.

B.  

On the hub, set the tunnel type to static.

C.  

On the spoke, configure the parameter localid .

D.  

On the hub, set the parameter mode-cfg to enable.

Discussion 0
Question # 9

When you use the command diagnose sys session list, how do you identify the sessions that correspond to traffic steered according to SD-WAN rules?

Options:

A.  

You identify sessions steered according to SD-WAN rules with the flag vwl.

B.  

You cannot identify SD-WAN sessions. You must use the sdwar. session filter.

C.  

You identify sessions steered according to SD-WAN rules with the data vwl_mbr_seq.

D.  

You identify sessions steered according to SD-WAN rules with the data 3dwan_service_id.

Discussion 0
Question # 10

You manage an SD-WAN topology. You will soon deploy 50 new branches. Which three tasks can you do in advance to simplify this deployment? (Choose three.)
Options:

A.  

Update the DHCP server configuration.

B.  

Create model devices.

C.  

Create a ZTP template.

D.  

Define metadata variables value for each device.

E.  

Create policy blueprint.

Discussion 0

NSE7_SSE_AR-26 PDF

NSE7_SSE_AR-26 PDF (Printable)
$46.5
$154.99

NSE7_SSE_AR-26 Testing Engine

NSE7_SSE_AR-26 PDF (Printable)
$51
$169.99

NSE7_SSE_AR-26 PDF + Testing Engine

NSE7_SSE_AR-26 PDF (Printable)
$63.9
$212.99
Exams4sure Dumps

Exam style questions across every NSE7_SSE_AR-26 domain

Last Update 1 hour ago
Total Questions : 110

Start with our free NSE7_SSE_AR-26 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real NSE 7 Network Security Architect exam. Each NSE7_SSE_AR-26 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.
Free Exams Sample Questions