

Exam style questions across every SY0-701 domain
Last Update 3 days ago
Total Questions : 907
Start with our free SY0-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CompTIA Security+ exam. Each SY0-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your CompTIA weak domains, see where you're losing marks, and build a focused study plan in minutes.

Which of the following security threats aims to compromise a website that multiple employees frequently visit?
A systems administrator receives an alert that a company ' s internal file server is very slow and is only working intermittently. The systems administrator reviews the server management software and finds the following information about the server:
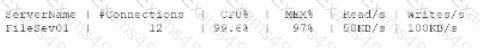
Which of the following indicators most likely triggered this alert?
A vendor needs to remotely and securely transfer files from one server to another using the command line. Which of the following protocols should be Implemented to allow for this type of access? (Select two).
After a security incident, a systems administrator asks the company to buy a NAC platform. Which of the following attack surfaces is the systems administrator trying to protect?
A security engineer needs to quickly identify a signature from a known malicious file. Which of the following analysis methods would the security engineer most likely use?
An external security assessment report indicates a high click rate on suspicious emails. The Chief Intelligence Security Officer (CISO) must reduce this behavior. Which of the following should the CISO do first?
A security analyst wants to automate a task that shares data between systems. Which of the following is the best option for the analyst to use?
An organization authorizes system deployment on the network after reducing the number of Category 1 vulnerabilities to zero. Which of the following is this scenario an example of?
A company is required to use certified hardware when building networks. Which of the following best addresses the risks associated with procuring counterfeit hardware?



