

Exam style questions across every CS0-004 domain
Last Update 2 days ago
Total Questions : 82
Start with our free CS0-004 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CompTIA CySA+ exam. Each CS0-004 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your CompTIA weak domains, see where you're losing marks, and build a focused study plan in minutes.

A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
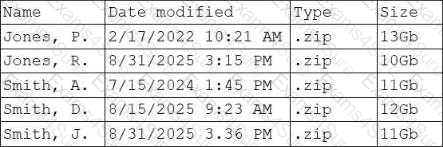
Which of the following actions should the analyst take first?
A security analyst responds to an alert regarding identity and access management activity within the cloud environment. The attacker is currently trying to gain access from one isolated cloud subscription to another via a compromised user role.
Which of the following aspects of the MITRE ATT & CK framework is the attacker trying to perform?
A security analyst analyzes the output of a web application access log for a company based in the United States.
Given the following output:
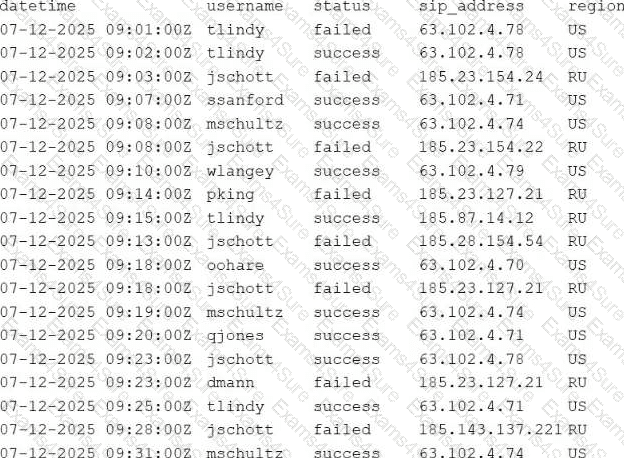
Which of the following users should be investigated first?
Which of the following best explains the purpose of the Pyramid of Pain in threat intelligence?
A security analyst reruns infrastructure as code (IaC) to tear down and rebuild a new environment after a ransomware attack.
Which of the following describes this phase?
Which of the following contains stakeholder contact information for incident response reporting?
Which of the following network architectures would best implement a perimeter-less network topology?
Which of the following phases of the incident response process will permanently remove an attacker’s access to corporate resources?
A security operations center analyst is using the command line to display specific traffic.
The analyst uses the following command:
$tshark -r file.pcap -Y "http or udp"
Which of the following will the command line display?
A new security operations center (SOC) manager joins a team that struggles to meet service-level agreements (SLAs). The alert backlog continues to increase daily.
Which of the following will the manager most likely need to do?



