

Exam style questions across every CS0-004 domain
Last Update 2 days ago
Total Questions : 82
Start with our free CS0-004 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CompTIA CySA+ exam. Each CS0-004 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your CompTIA weak domains, see where you're losing marks, and build a focused study plan in minutes.

Which of the following is the most comprehensive type of report associated with a closed incident?
A vulnerability analyst runs a credentialed vulnerability scan covering all addressable enterprise assets. After running the scan, the analyst discovers a large number of critical vulnerabilities that cannot be immediately remediated.
Which of the following are the most likely reasons why the vulnerabilities cannot be immediately addressed?
Based on recent alerts, a security analyst thinks a web application server was compromised. The analyst reviews the following server output:
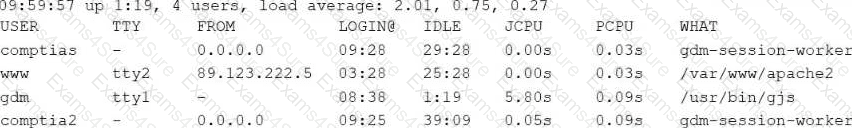
Which of the following best describes what has occurred?
The vulnerability management team must scan the cloud environment to establish security baselines.
Which of the following assessment tools should the team use to perform this task?



