

Exam style questions across every CS0-004 domain
Last Update 2 days ago
Total Questions : 82
Start with our free CS0-004 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CompTIA CySA+ exam. Each CS0-004 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your CompTIA weak domains, see where you're losing marks, and build a focused study plan in minutes.

Which of the following is the main concept behind the use of an attack methodology framework?
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network.
Which of the following artifacts should the analyst collect first?
The Chief Information Security Officer wants to improve internal security measures by continuously validating and verifying access to the production environment.
Which of the following concepts best describes this practice?
An analyst performs Nmap scans to determine which hosts may need to be targeted to deploy a critical Windows patch. The patch for the vulnerability is to address a critical security flaw that targets open Server Message Block (SMB) ports on Windows systems only.
The analyst scans with the following command:
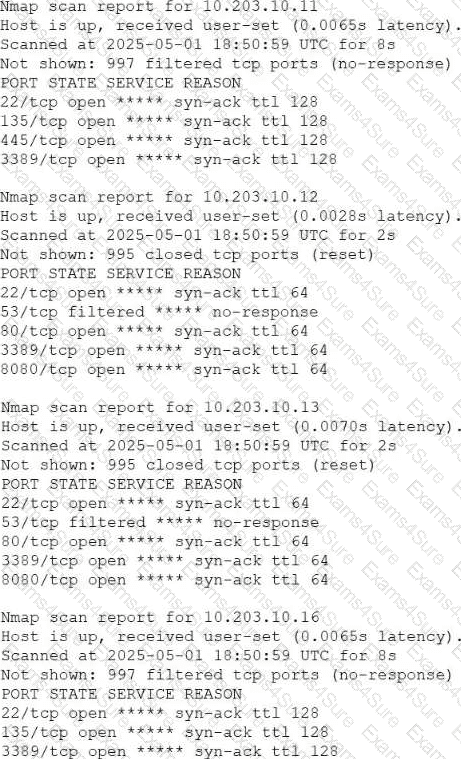
$sudo nmap -Pn 10.203.10.0/24
The analyst then receives the following output:
Which of the following hosts should the analyst prioritize for patching?
Multiple users report unexpected mouse movements and terminal windows opening.
An analyst reviewing the network traffic logs observes the following:
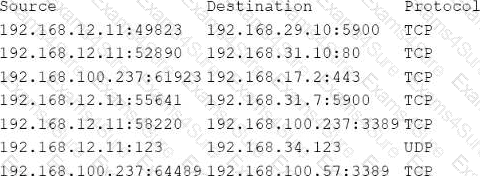
Which of the following is the most likely reason for the reported symptoms?
Which of the following is the most difficult for threat actors to change according to the Pyramid of Pain model?
A security operations center (SOC) manager reviews a document signed by the Chief Financial Officer (CFO), the sales director, and a customer to decide whether a contract breach occurred.
Which of the following best describes the document that includes key performance indicators (KPIs)?
An analyst needs to perform a baseline security evaluation of the company's cloud infrastructure.
Which of the following tools is most appropriate for this task?
Despite removing malware from some of the affected hosts, several of an organization's internal resources are still unavailable two weeks after the discovery of a major incident.
Which of the following best describes this phase?
An analyst reviews a summarized vulnerability report through a governance, risk, and compliance (GRC) reporting tool.
The following report correlates asset information from the configuration management database (CMDB) against detected vulnerabilities:
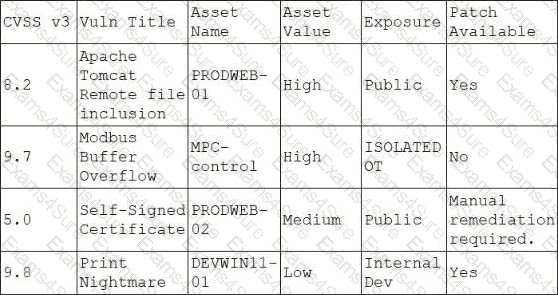
Which of the following servers should the analyst prioritize based on the target value, the risk, and the likelihood of exploitation?



