Exclusive Black Friday Deal: 70% Off All Exam Bundles! Use coupon code below to unlock your savings! - Ends in 0d 00h 00m 00s - Coupon code: Friday70

Free Fortinet NSE 7 - Security Operations 7.6 Architect Practice Questions

Question # 21

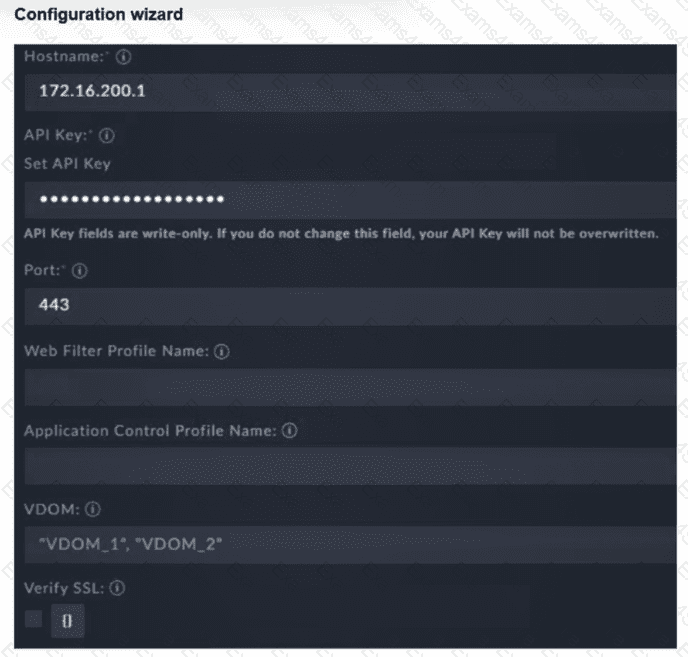
Refer to the exhibit.
Question # 21

You must configure the FortiGate connector to allow FortiSOAR to perform actions on a firewall. However, the connection fails. Which two configurations are required? (Choose two answers)

Options:

A.  

Trusted hosts must be enabled and the FortiSOAR IP address must be permitted.

B.  

The VDOM name must be specified, or set to VDOM_1, if VDOMs are not enabled on FortiGate.

C.  

HTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.

D.  

An API administrator must be created on FortiGate with the appropriate profile, along with a generated API key to configure on the connector.

Discussion 0
Question # 22

A very long FortiSOAR playbook failed at step 30 because of an intermittent networking issue, which has now been resolved. You want to finish executing the playbook without repeating earlier steps or losing prior context. Which action should you take? Choose one answer.

Options:

A.  

Use mock input for step 30 and re-run the playbook.

B.  

Use the Load ENV JSON option in the Jinja Editor and then render the output.

C.  

Use the Rerun From Last Failed Step option from the executed playbook logs.

D.  

Add a connector from the trigger to step 30 directly and re-run the playbook.

Discussion 0
Question # 23

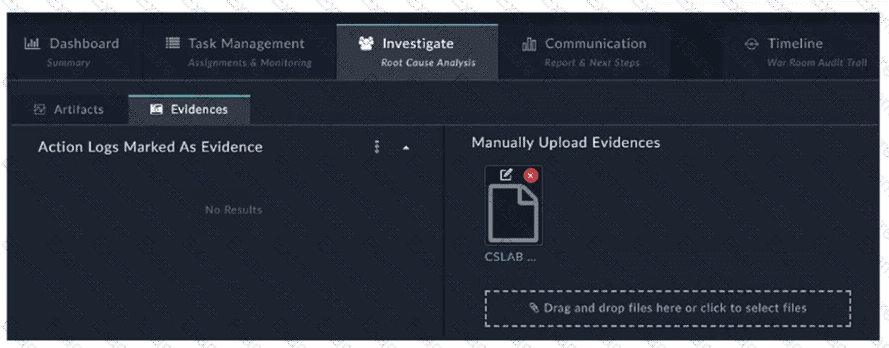
Refer to the exhibit.

Question # 23

How do you add a piece of evidence to the Action Logs Marked As Evidence area? (Choose one answer)

Options:

A.  

By tagging output or a workspace comment with the keyword Evidence

B.  

By linking an indicator to the war room

C.  

By creating an evidence collection task and attaching a file

D.  

By executing a playbook with the Save Execution Logs option enabled

Discussion 0
Question # 24

Refer to the exhibits.

You configured a custom event handler and an associated rule to generate events whenever FortiMail detects spam emails. However, you notice that the event handler is generating events for both spam emails and clean emails.

Which change must you make in the rule so that it detects only spam emails?

Options:

A.  

In the Log Type field, select Anti-Spam Log (spam)

B.  

In the Log filter by Text field, type type==spam.

C.  

Disable the rule to use the filter in the data selector to create the event.

D.  

In the Trigger an event when field, select Within a group, the log field Spam Name (snane) has 2 or more unique values.

Discussion 0
Question # 25

Review the incident report. Shortly after being compromised, an infected host collected its own network configuration and connection details, then began sending low-volume connection attempts to multiple internal addresses to identify responding hosts. Which two MITRE ATT & CK techniques best describe this activity? Choose two answers.

Options:

A.  

System Network Connections Discovery

B.  

Network Sniffing

C.  

Lateral Movement

D.  

Active Scanning

Discussion 0
Question # 26

Review the incident report. A fake HR login page was sent to several employees through email. The page copied the company’s branding and captured usernames and passwords. The attacker later used the stolen credentials to sign in through the company’s web VPN. Which two MITRE ATT & CK tactics best characterize this report? Choose two answers.

Options:

A.  

Initial Access

B.  

Command and Control

C.  

Credential Access

D.  

Defense Evasion

Discussion 0
Question # 27

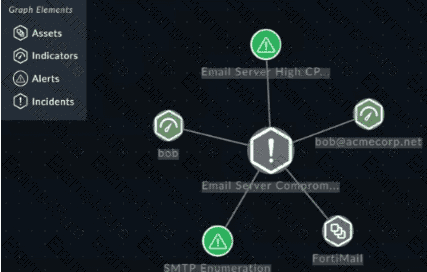
You are investigating an open incident and want to add records from the Tickets module, a custom module, to the visual correlation widget. Assume there are already linked ticket records to the incident.
Question # 27

How do you accomplish this? Choose one answer.

Options:

A.  

Ingest ticket records through a custom connector.

B.  

Tag ticket records with the incident I

D.  

C.  

Edit the incident template and add the Tickets module to the graph.

D.  

Define more module relationships under Correlation Settings.

Discussion 0
Question # 28

You are designing a FortiSOAR hybrid multi-tenant deployment. The architecture must support remote tenant execution and automation inside segmented networks. Which three elements are true for this design? Choose three answers.
Options:

A.  

The secure message exchange must be a dedicated instance instead of an embedded one.

B.  

The FortiSOAR master cluster can host shared tenants, with strict data isolation between them.

C.  

Each tenant or agent has a dedicated, access-controlled space on a secure message exchange for message routing.

D.  

FortiSOAR tenant nodes or agents use TCP port 5671 to communicate with the secure message exchange.

E.  

FortiSOAR agents are deployed on the master cluster to improve high availability (HA) performance.

Discussion 0

NSE7_SOC_AR-7.6 PDF

NSE7_SOC_AR-7.6 PDF (Printable)
$46.5
$154.99

NSE7_SOC_AR-7.6 Testing Engine

NSE7_SOC_AR-7.6 PDF (Printable)
$51
$169.99

NSE7_SOC_AR-7.6 PDF + Testing Engine

NSE7_SOC_AR-7.6 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions