Refer to the exhibits.
The FortiMail Sender Blocklist playbook is configured to take manual input and add those entries to the FortiMail abc. com domain-level block list. The playbook is configured to use a FortiMail connector and the ADD_SENDER_TO_BLOCKLIST action.
Why is the FortiMail Sender Blocklist playbook execution failing7
Refer to the exhibit.
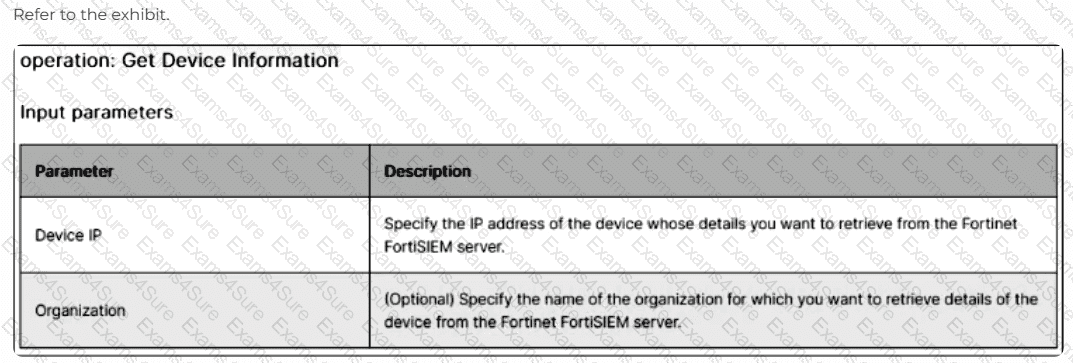
The input of a FortiSIEM connector action is shown.
You want to create a playbook on FortiSOAR that allows you to accomplish the following:
Manually input an IP address.
Use the connector action in the exhibit to retrieve a device from the FortiSIEM configuration management database (CMDB) with that IP address.
Ask the SOC manager to review the information pulled from FortiSIEM about that device.
If the manager approves, an asset record is created.
Which combination and order of step operations fulfills the requirements with the fewest required playbook steps?
Refer to the exhibit.
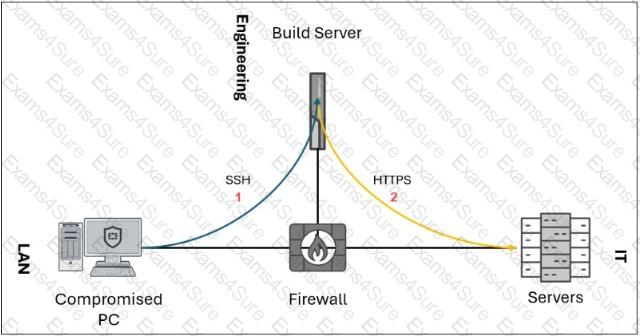
A compromised PC establishes an SSH connection to an engineering build server, which then relays HTTPS traffic to reach servers that would otherwise have blocked access from the LAN. Which technique is used for this attack?
Review the following incident report:
Attackers leveraged a phishing email campaign targeting your employees.
The email likely impersonated a trusted source, such as the IT department, and requested login credentials.
An unsuspecting employee clicked a malicious link in the email, leading to the download and execution of a Remote Access Trojan (RAT).
The RAT provided the attackers with remote access and a foothold in the compromised system.
Which two MITRE ATT & CK tactics does this incident report capture? (Choose two.)
Which statement describes automation stitch integration between FortiGate and FortiAnalyzer?
You configured a queue called L1 Analysts and generated shifts to cover morning, evening, and overnight shifts, with two members covering each shift.
However, you noticed that all members of the queue are assigned ingested alerts in a round-robin fashion, instead of only users who are currently on shift.
What is the problem?
While monitoring your network, you discover that one FortiGate device is sending significantly more logs to FortiAnalyzer than all of the other FortiGate devices in the topology.
Additionally, the ADOM that the FortiGate devices are registered to consistently exceeds its quota.
What are two possible solutions? (Choose two.)
Review the incident report:
An attacker identified employee names, roles, and email patterns from public press releases, which were then used to craft tailored emails.
The emails were directed to recipients to review an attached agenda using a link hosted off the corporate domain.
Which two MITRE ATT & CK tactics best fit this report? (Choose two answers)
What are three capabilities of the built-in FortiSOAR Jinja editor? (Choose three answers)
Which two playbook triggers enable the use of trigger events in later tasks as trigger variables? (Choose two.)
Exam style questions across every NSE7_SOC_AR-7.6 domain
Last Update 2 days ago
Total Questions : 96
Start with our free NSE7_SOC_AR-7.6 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real Fortinet Certified Professional Security Operations exam. Each NSE7_SOC_AR-7.6 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Fortinet weak domains, see where you're losing marks, and build a focused study plan in minutes.