Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Practice Questions

Question # 121

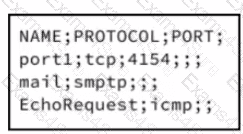
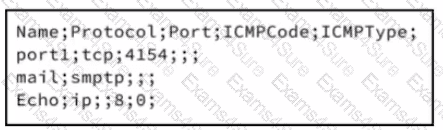
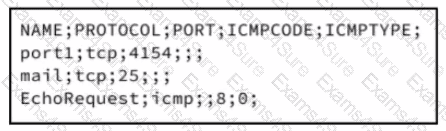
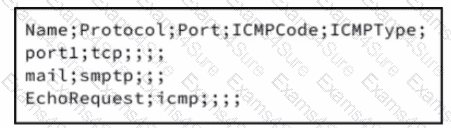
An engineer must import three port objects into the Cisco Secure Firewall Management Center by using a CSV file. Which file content must be imported to meet the requirement?

A)
Question # 121

B)

Question # 121

C)

Question # 121

D)

Question # 121

Options:

A.  

Option

B.  

Option

C.  

Option

D.  

Option

Discussion 0
Question # 122

An engineer is troubleshooting connectivity to the DNS servers from hosts behind a new Cisco FTD device. The hosts cannot send DNS queries to servers in the DMZ. Which action should the engineer take to troubleshoot this issue using the real DNS packets?

Options:

A.  

Use the Connection Events dashboard to check the block reason and adjust the inspection policy as needed.

B.  

Use the packet capture tool to check where the traffic is being blocked and adjust the access control or intrusion policy as needed.

C.  

Use the packet tracer tool to determine at which hop the packet is being dropped.

D.  

Use the show blocks command in the Threat Defense CLI tool and create a policy to allow the blocked traffic.

Discussion 0
Question # 123

While configuring FTD, a network engineer wants to ensure that traffic passing through the appliance does not require routing or Vlan rewriting. Which interface mode should the engineer implement to accomplish this task?

Options:

A.  

passive

B.  

transparent

C.  

Inline tap

D.  

Inline set

Discussion 0
Question # 124

A cisco Secure firewall Threat Defence device is configured in inline IPS mode to inspect all traffic that passes through the interfaces in the inline set. Which setting in the inline set configuration must be connected to allow traffic to pass through uninterrupted when VDB updates are being applied?

Options:

A.  

Propagate Link State

B.  

Short Fall Open

C.  

Strict TCP Enforcement

D.  

Tap Mode

Discussion 0
Question # 125

A network administrator is concerned about (he high number of malware files affecting users ' machines. What must be done within the access control policy in Cisco FMC to address this concern?

Options:

A.  

Create an intrusion policy and set the access control policy to block.

B.  

Create an intrusion policy and set the access control policy to allow.

C.  

Create a file policy and set the access control policy to allow.

D.  

Create a file policy and set the access control policy to block.

Discussion 0
Question # 126

A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FM

C.  

An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?

Options:

A.  

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.

B.  

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.

C.  

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.

D.  

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.

Discussion 0
Question # 127

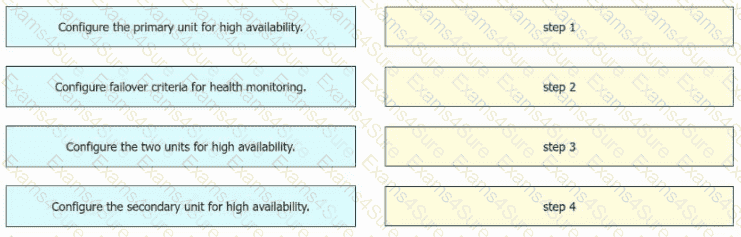
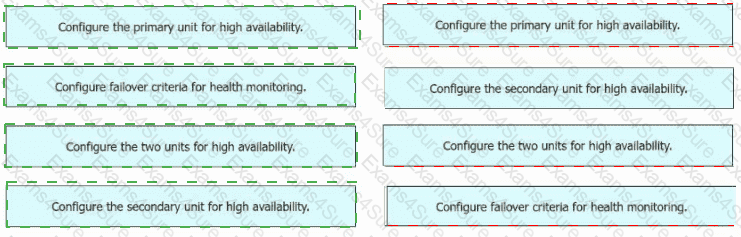
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
Question # 127

Options:

Discussion 0
Question # 128

An engineer is configuring a file policy on a Cisco Secure Firewall Management Center appliance. Files with an Unknown disposition must be analyzed by Cisco Secure Malware Analytics. What must be configured on the Secure Firewall Management Center appliance?

Options:

A.  

Sandbox Analysis

B.  

Spero Analysis

C.  

Malware Analysis

D.  

Dynamic Analysis

Discussion 0
Question # 129

An engineer must configure a new identity policy in Cisco Firepower Management Center. Active authentication must be configured by using a Kerberos connection. Which two realms must be configured? (Choose two.)

Options:

A.  

Directory password

B.  

Active directory join password

C.  

Active directory primary domain

D.  

Active directory join username

E.  

Directory username

Discussion 0
Question # 130

With a recent summer time change, system logs are showing activity that occurred to be an hour behind real time Which action should be taken to resolve this issue?


Options:

A.  

Manually adjust the time to the correct hour on all managed devices

B.  

Configure the system clock settings to use NTP with Daylight Savings checked

C.  

Manually adjust the time to the correct hour on the Cisco FM

C.  

D.  

Configure the system clock settings to use NTP

Discussion 0

300-710 PDF

300-710 PDF (Printable)
$54.25
$154.99

300-710 Testing Engine

300-710 PDF (Printable)
$59.5
$169.99

300-710 PDF + Testing Engine

300-710 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions