
An organization has implemented Cisco Firepower without IPS capabilities and now wants to enable inspection for their traffic. They need to be able to detect protocol anomalies and utilize the Snort rule sets to detect malicious behaviour. How is this accomplished?
An engineer is attempting to create a new dashboard within the Cisco FMC to have a single view with widgets from many of the other dashboards. The goal is to have a mixture of threat and security related widgets along with Cisco Firepower device health information. Which two widgets must be configured to provide this information? (Choose two).
What is the maximum SHA level of filtering that Threat Intelligence Director supports?
Refer to the exhibit.
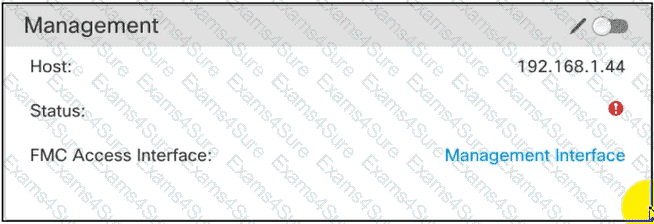
What is the effect of the existing Cisco FMC configuration?
An engineer must configure a SPAN session to monitor traffic by using a Cisco Secure IPS device in passive mode. Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst switch interface Gi0/3. Which SPAN configuration meets the requirement?
A network administrator is configuring a Cisco AMP public cloud instance and wants to capture infections and polymorphic variants of a threat to help detect families of malware. Which detection engine meets this requirement?
An engineer configures a network discovery policy on Cisco FM
C.
Upon configuration, it is noticed that excessive and misleading events filing the database and overloading the Cisco FMC.
A monitored NAT device is executing multiple updates of its operating system in a short period of time. What configurationchange must be made to alleviate this issue?An engineer must deploy a high-availability that includes two Cisco Secure Firewall Threat Defense devices configured as cluster. The deployment must have a mechanism that protects synchronization between cluster members Which action must the engineer take to meet the requirements?
An engineer must deploy a Cisco FTD device. Management wants to examine traffic without requiring network changes that will disrupt end users. Corporate security policy requires the separation of management traffic from data traffic and the use of SSH over Telnet for remote administration. How must the device be deployed to meet these requirements?
Refer to the exhibit.
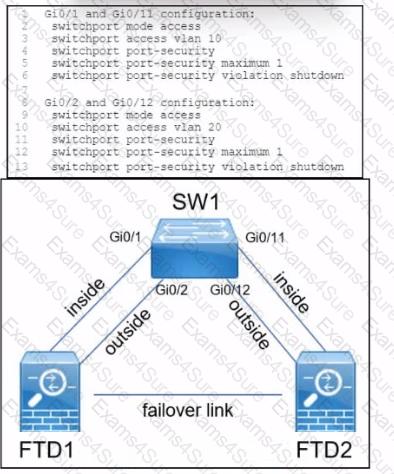
A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?




