Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Practice Questions

Question # 41

A connectivity issue is occurring between a client and a server which are communicating through a Cisco Firepower device While troubleshooting, a network administrator sees that traffic is reaching the server, but the client is not getting a response Which step must be taken to resolve this issue without initiating traffic from the client?

Options:

A.  

Use packet-tracer to ensure that traffic is not being blocked by an access list.

B.  

Use packet capture to ensure that traffic is not being blocked by an access list.

C.  

Use packet capture to validate that the packet passes through the firewall and is NATed to the corrected IP address.

D.  

Use packet-tracer to validate that the packet passes through the firewall and is NATed to the corrected IP address.

Discussion 0
Question # 42

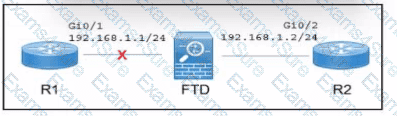
Refer to the exhibit.

Question # 42

A Cisco Secure Firewall Threat Defense (FTD) device is deployed in inline mode with an inline set. The network engineer wants router R2 to remove the directly connected route M 68.1.0/24 from its routing table when the cable between routed R1 and the Secure FTD device Is disconnected. Which action must the engineer take?

1

Options:

A.  

Implement the Propagate Link Stale option on the Secure FTD device

B.  

Establish a routing protocol between R1 and R2.

C.  

Disable hardware bypass on the Secure FTD device.

D.  

Implement autostate functionality on the Gi0/2 interface of R2

Discussion 0
Question # 43

Network traffic coining from an organization ' s CEO must never be denied. Which access control policy configuration option should be used if the deployment engineer is not permitted to create a rule to allow all traffic?

Options:

A.  

Configure firewall bypass.

B.  

Change the intrusion policy from security to balance.

C.  

Configure a trust policy for the CEO.

D.  

Create a NAT policy just for the CEO.

Discussion 0
Question # 44

A network administrator manages a network with multiple firewalls in a datacenter using Cisco Secure Firepower Management Center. The administrator must change a next-generation firewall from routed to transparent mode. Which action must the administrator take next to meet the requirement?
Options:

A.  

Deregister the firewall in Cisco Secure Firewall Management Center.

B.  

Enter the configure transparent firewall command from the CLI.

C.  

Create one or more bridge groups from the CLI.

D.  

Manually delete the interface configuration from the CLI.

Discussion 0
Question # 45

Question # 45

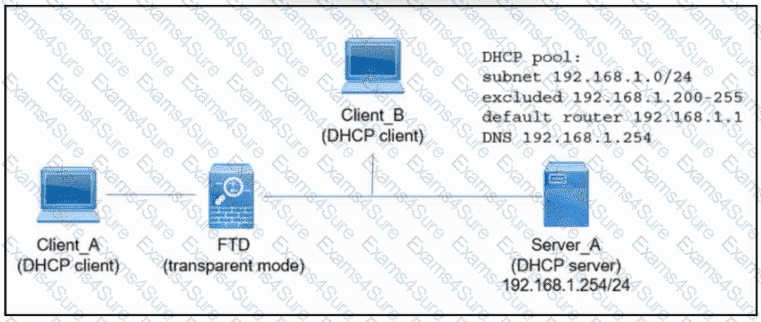
Refer to the exhibit. An engineer is deploying a new instance of Cisco Secure Firewall Threat Defense. Which action must the engineer take next so that Client_A and Client_B receive an IP address via DHCP from Server_A?
Options:

A.  

Disable Option 82 in the DHCP relay configuration properties using Secure Firewall Management Center.

B.  

Add access rules that allow DHCP traffic by using Cisco Secure Firewall Management Center.

C.  

Add another DHCP pool on Server_A with DHCP relay on Secure Firewall Threat Defense.

D.  

Disable all the DHCP Snort rules by using Secure Firewall Device Manager.

Discussion 0
Question # 46

Question # 46

Question # 46

Question # 46

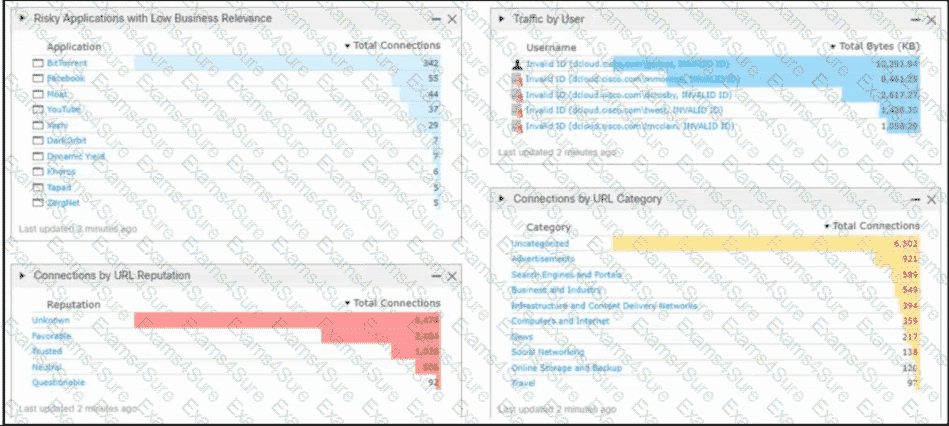
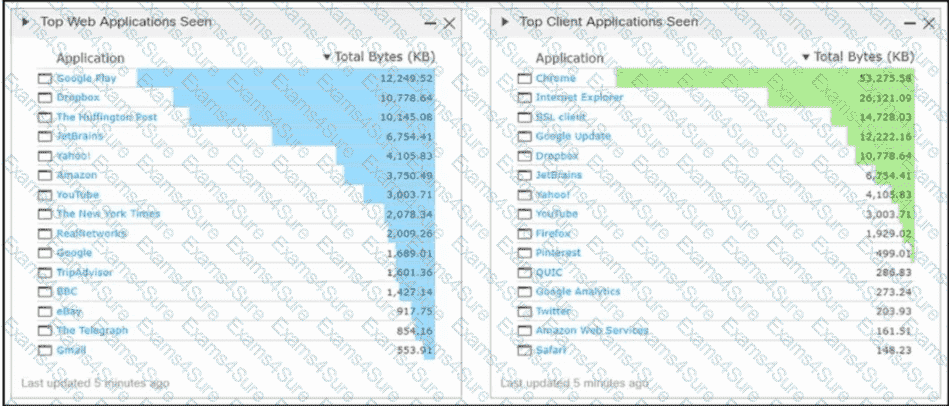
Refer to the exhibit. An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must be taken by the user to decrease the risk of data loss?

Options:

A.  

Stop all URLs that have an unknown reputation.

B.  

Block the use of Dropbox.

C.  

Stop all the URLs that are uncategorized.

D.  

Block all the BitTorrent applications.

Discussion 0
Question # 47

A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)

Options:

A.  

outbound port TCP/443

B.  

inbound port TCP/80

C.  

outbound port TCP/8080

D.  

inbound port TCP/443

E.  

outbound port TCP/80

Discussion 0
Question # 48

A network administrator configured an access control rule named WEB05405_SRV06798_ALLOW that allows any source on the Internet to reach the public IP address of a web server on port 8080. The administrator also configured a NAT policy that translates the public IP address to the internal web server IP address. During testing, the web server is not reachable from the Internet on port 8080. Which configuration must the administrator apply to resolve the issue?

Options:

A.  

Configure the access control rule with the Trust action.

B.  

Disable intrusion inspection for port 8080.

C.  

Modify the NAT policy to translate the source IP address as well as the destination IP address.

D.  

Replace the web server’s public IP address with its internal IP address in the access control rule.

Discussion 0
Question # 49

A network engineer must configure an existing firewall to have a NAT configuration. The now configuration must support more than two interlaces per context. The firewall has previously boon operating transparent mode. The Cisco Secure Firewall Throat Defense (FTD) device has been deregistered from Cisco Secure Firewall Management Center (FMC). Which set of configuration actions must the network engineer take next to meet the requirements?

Options:

A.  

Run the configure manager add routed command from the Secure FTD device CL1, and reregister with Secure FM

C.  

B.  

Run the configure firewall routed command from the Secure FTD device CD, and reregister with Secure FM

C.  

C.  

Run the configure manager add routed command from the Secure FMC CLI. and reregister with Secure FM

C.  

D.  

Run the configure firewall routed command from the Secure FMC CLI. and reregister with Secure FM

C.  

Discussion 0
Question # 50

Which protocol establishes network redundancy in a switched Firepower device deployment?

Options:

A.  

STP

B.  

HSRP

C.  

GLBP

D.  

VRRP

Discussion 0

300-710 PDF

300-710 PDF (Printable)
$54.25
$154.99

300-710 Testing Engine

300-710 PDF (Printable)
$59.5
$169.99

300-710 PDF + Testing Engine

300-710 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions