
Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Practice Questions

Question # 11

An administrator is configuring their transparent Cisco FTD device to receive ERSPAN traffic from multiple switches on a passive port, but the Cisco FTD is not processing the traffic. What is the problem?

Options:

A.  

The switches do not have Layer 3 connectivity to the FTD device for GRE traffic transmission.

B.  

The switches were not set up with a monitor session ID that matches the flow ID defined on the CiscoFT

D.  

C.  

The Cisco FTD must be in routed mode to process ERSPAN traffic.

D.  

The Cisco FTD must be configured with an ERSPAN port not a passive port.

Discussion 0
Question # 12

A network administrator must create an EtherChannel Interface on a new Cisco Firepower 9300 appliance registered with an FMC tor high availability. Where must the administrator create the EtherChannel interface?

Options:

A.  

FMC CLI

B.  

FTD CLI

C.  

FXOS CLI

D.  

FMC GUI

Discussion 0
Question # 13

A security engineer must configure a Cisco Secure Firewall Threat Defense device to inspect only executable files. A lightweight method of detecting whether a file is an executable must be used. Which configuration for Malware Cloud Lookup must be selected in Cisco Secure Firewall Management Center?
Options:

A.  

capacity handling

B.  

Local Malware Analysis

C.  

dynamic analysis

D.  

Spero analysis for MSEXE

Discussion 0
Question # 14

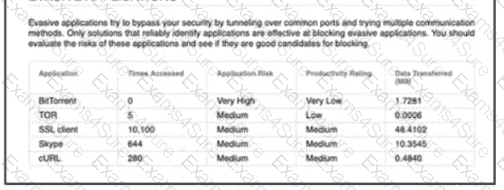
Question # 14

Refertothe exhibit. An engineer is analyzing a Network Risk Report from Cisco FM

C.  

Which application must the engineer take immediate action against to prevent unauthorized network use?

Options:

A.  

Kerberos

B.  

YouTube

C.  

Chrome

D.  

TOR

Discussion 0
Question # 15

A network administrator is deploying a Cisco IPS appliance and needs it to operate initially without affecting traffic flows.

It must also collect data to provide a baseline of unwanted traffic before being reconfigured to drop it. Which Cisco IPS mode meets these requirements?

Options:

A.  

failsafe

B.  

inline tap

C.  

promiscuous

D.  

bypass

Discussion 0
Question # 16

A security engineer wants to add the Interface Traffic widget to the Summary Dashboard in Cisco Secure Firewall Management Center. The engineer clicks Add Widgets and enters edit mode. Which set of actions must the security engineer take to complete the configuration?

Options:

A.  

Click All Categories, open the Analysis & Reporting tab, and then click the Add widget button.

B.  

Click All Categories, open the New tab, and then click the Add widget button.

C.  

Click All Categories, open the Operations tab, and then click the Add widget button.

D.  

Click All Categories, open the Miscellaneous tab, and then click the Add widget button.

Discussion 0
Question # 17

An engineer is implementing Cisco FTD in the network and is determining which Firepower mode to use. The organization needs to have multiple virtual Firepower devices working separately inside of the FTD appliance to provide traffic segmentation Which deployment mode should be configured in the Cisco Firepower Management Console to support these requirements?

Options:

A.  

multiple deployment

B.  

single-context

C.  

single deployment

D.  

multi-instance

Discussion 0
Question # 18

What is a functionality of port objects in Cisco FMC?

Options:

A.  

to mix transport protocols when setting both source and destination port conditions in a rule

B.  

to represent protocols other than TCP, UDP, and ICMP

C.  

to represent all protocols in the same way

D.  

to add any protocol other than TCP or UDP for source port conditions in access control rules.

Discussion 0
Question # 19

When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?

Options:

A.  

retry

B.  

replace

C.  

block

D.  

blocfcflow

Discussion 0
Question # 20

An engineer is investigating connectivity problems on Cisco Firepower for a specific SGT. Which command allows the engineer to capture real packets that pass through the firewall using an SGT of 64?


Options:

A.  

capture CAP type inline-tag 64 match ip any any

B.  

capture CAP match 64 type inline-tag ip any any

C.  

capture CAP headers-only type inline-tag 64 match ip any any

D.  

capture CAP buffer 64 match ip any any

Discussion 0

300-710 PDF

300-710 PDF (Printable)
$54.25
$154.99

300-710 Testing Engine

300-710 PDF (Printable)
$59.5
$169.99

300-710 PDF + Testing Engine

300-710 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions

