
Within an organization ' s high availability environment where both firewalls are passing traffic, traffic must be segmented based on which department it is destined for. Each department is situated on a different LAN. What must be configured to meet these requirements?
An engineer is setting up a new Cisco Secure Firewall Threat Defense appliance to replace the current firewall. The company requests that inline sets be used and that when one interface in
an inline set goes down, the second interface in the inline set goes down. What must the engineer configure to meet the deployment requirements?
Which two actions can be used in an access control policy rule? (Choose two.)
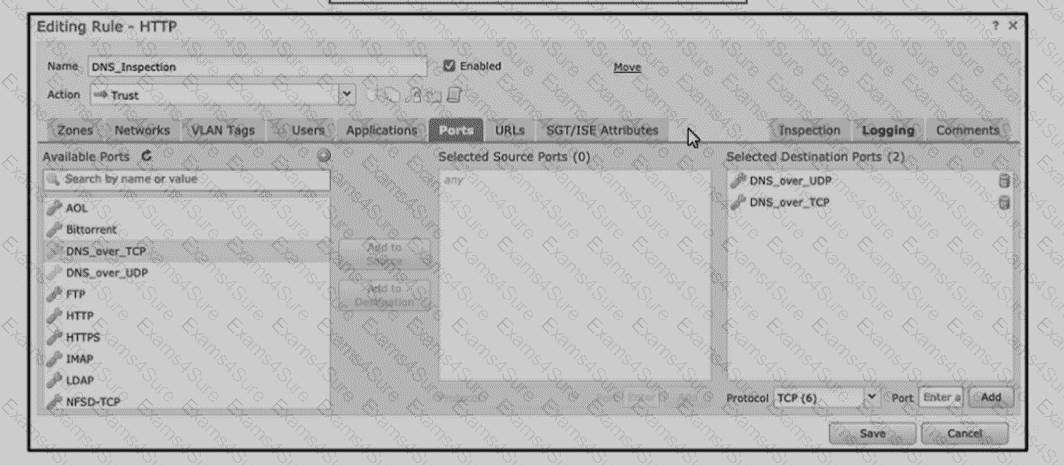
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying thepokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?
A security engineer is deploying a Cisco Secure Firewall Threat Defense device through Cisco Secure Firewall Management Center. The Threat license is installed, the Encrypted Visibility Engine is enabled in the access control policy Decryption policy is configured with the Decrypt - Resign action to inspect outbound TLS/SSL traffic. Users report that a banking applications repeatedly fails to load. The engineer confirms the endpoint performs certificate pinning to validate the server certificate. Engineer must allow the traffic to pass while all other outbound traffic continues to be inspected. The engineer created a rule that matches banking category and placed the rule above Decrypt - Resign policy. Which decryption rule action must be configured to meet the requirement?
A network engineer wants to add a third-party threat feed into the Cisco FMC for enhanced threat detectionWhich action should be taken to accomplish this goal?
A security engineer must configure policies tor a recently deployed Cisco FT
D.
The security policy for the company dictates that when five or more connections from external sources are initiated within 2 minutes, there is cause for concern. Which type of policy must be configured in Cisco FMC \z generate an alert when this condition is triggered?An administrator is attempting to remotely log into a switch in the data centre using SSH and is unable to connect. How does the administrator confirm that traffic is reaching the firewall?
An administrator is creating interface objects to better segment their network but is having trouble adding interfaces to the objects. What is the reason for this failure?
Refer to the exhibit.
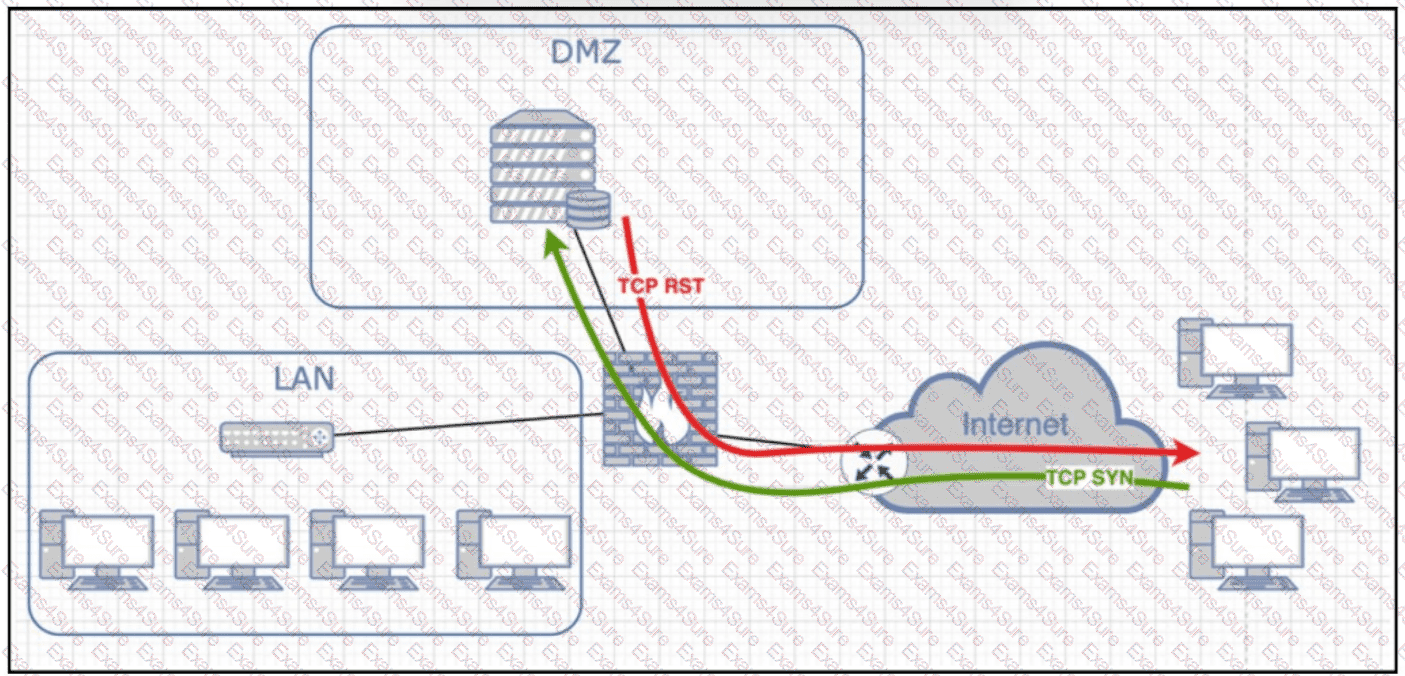
Following a critical incident, an engineer must determine why a server in the DMZ is sending TCP RST responses. Internet users can access the application but cannot view its main webpage. Where must the engineer capture the traffic to identify and resolve the issue?




