
On the advanced tab under inline set properties, which allows interfaces to emulate a passive interface?
A network administrator wants to block traffictoa known malware site athttps://www.badsite.comand all subdomains while ensuring no packets from any internal client are sent to that site. Which type of policy must the network administrator use to accomplish this goal?
The event dashboard within the Cisco FMC has been inundated with low priority intrusion drop events, which are overshadowing high priority events. An engineer has been tasked with reviewing the policies and reducing the low priority events. Which action should be configured to accomplish this task?
Which firewall design allows a firewall to forward traffic at layer 2 and layer 3 for the same subnet?
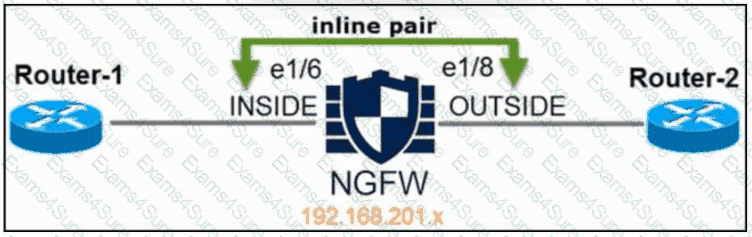
Refer to the exhibit. An engineer is configuring an instance of Cisco Secure Firewall Threat Defense with interfaces in IPS Inline Pair mode. What must be configured on interface e1/6 to accomplish the requirement?
An engineer is implementing a new Cisco Secure Firewall. The firewall must filler traffic between the three subnets:
• LAN 192.168.101.0724
• DMZ 192.168 200.0/24
• WAN 10.0.0.0/30
Which firewall mode must the engineer implement?
An engineer is troubleshooting a file that is being blocked by a Cisco FTD device on the network.
The user is reporting that the file is not malicious.
Which action does the engineer take to identify the file and validate whether or not it is malicious?
Which license type is required on Cisco ISE to integrate with Cisco FMC pxGrid?
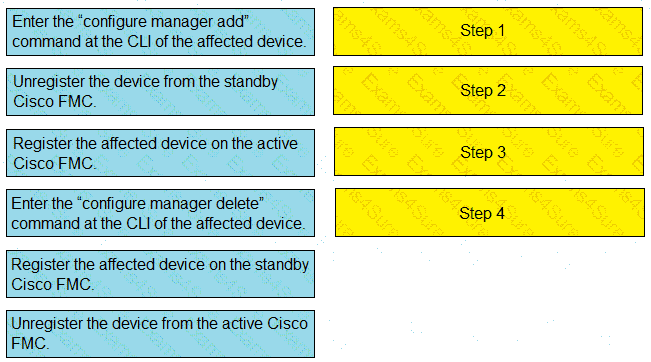
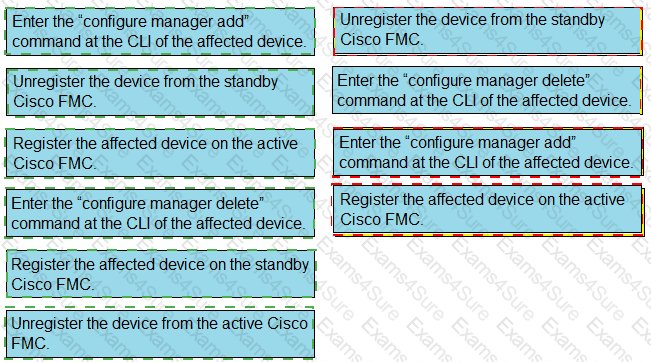
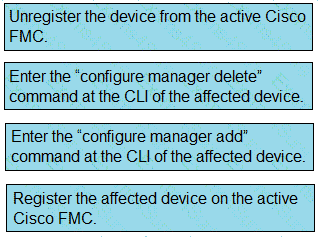
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
An engineer must deploy a Cisco FTD appliance via Cisco FMC to span a network segment to detect malware and threats. When setting the Cisco FTD interface mode, which sequence of actions meets this requirement?

Exam style questions across every 300-710 domain
Last Update 14 hours ago
Total Questions : 444
Start with our free 300-710 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 300-710 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.



