Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Practice Questions

Question # 101

An engineer has been tasked with performing an audit of network projects to determine which objects are duplicated across the various firewall models (Cisco Secure Firewall Threat Defense Cisco Secure firewall ASA, and Meraki MX Series) deployed throughout the company Which tool will assist the engineer in performing that audit?

Options:

A.  

Cisco Firepower Device Manager

B.  

Cisco SecureX

C.  

Cisco Defense Orchestrator

D.  

Cisco Secure Firewall Management Center

Discussion 0
Question # 102

An analyst is investigating a potentially compromised endpoint within the network and pulls a host report for the endpoint in question to collect metrics and documentation. What information should be taken from this report for the investigation?

Options:

A.  

client applications by user, web applications, and user connections

B.  

number of attacked machines, sources of the attack, and traffic patterns

C.  

intrusion events, host connections, and user sessions

D.  

threat detections over time and application protocols transferring malware

Discussion 0
Question # 103

Network users are experiencing Intermittent issues with internet access. An engineer ident med mat the issue Is being caused by NAT exhaustion. How must the engineer change the dynamic NAT configuration to provide internet access for more users without running out of resources?

Options:

A.  

Define an additional static NAT for the network object in use.

B.  

Configure fallthrough to interface PAT on ' he Advanced tab.

C.  

Convert the dynamic auto NAT rule to dynamic manual NAT.

D.  

Add an identity NAT rule to handle the overflow of users.

Discussion 0
Question # 104

An engineer is configuring a cisco FTD appliance in IPS-only mode and needs to utilize fail-to-wire interfaces. Which interface mode should be used to meet these requirements?

Options:

A.  

transparent

B.  

routed

C.  

passive

D.  

inline set

Discussion 0
Question # 105

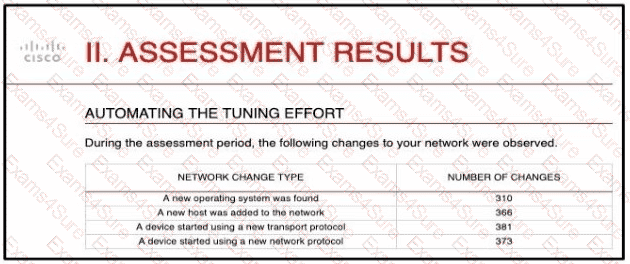
Refer to the exhibit.

Question # 105

And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?

Options:

A.  

Cisco Firepower automatically updates the policies.

B.  

The administrator requests a Remediation Recommendation Report from Cisco Firepower

C.  

Cisco Firepower gives recommendations to update the policies.

D.  

The administrator manually updates the policies.

Discussion 0
Question # 106

A company has many Cisco FTD devices managed by a Cisco FM

C.  

The security model requires that access control rule logs be collected for analysis. The security engineer is concerned that the Cisco FMC will not be able to process the volume of logging that will be generated. Which configuration addresses this concern?

Options:

A.  

Send Cisco FTD connection events and security events directly to SIEM system for storage and analysis.

B.  

Send Cisco FTD connection events and security events to a cluster of Cisco FMC devices for storage and analysis.

C.  

Send Cisco FTD connection events and security events to Cisco FMC and configure it to forward logs to SIEM for storage and analysis.

D.  

Send Cisco FTD connection events directly to a SIEM system and forward security events from Cisco FMC to the SIEM system for storage and analysis.

Discussion 0
Question # 107

What are the minimum requirements to deploy a managed device inline?

Options:

A.  

inline interfaces, security zones, MTU, and mode

B.  

passive interface, MTU, and mode

C.  

inline interfaces, MTU, and mode

D.  

passive interface, security zone, MTU, and mode

Discussion 0
Question # 108

An engineer is integrating Cisco Secure Endpoint with Cisco Secure Firewall Management Center in high availability mode. Malware events detected by Secure Endpoint must also be

received by Secure Firewall Management Center and public cloud services are used. Which two configurations must be selected on both high availability peers independently? (Choose two.)

Options:

A.  

internet connection

B.  

Smart Software Manager Satellite

C.  

Cisco Success Network

D.  

security group tag

E.  

Secure Endpoint Cloud Connection

Discussion 0
Question # 109

A network administrator is configuring a site-to-site IPsec VPN to a router sitting behind a Cisco FT

D.  

The administrator has configured an access policy to allow traffic to this device on UDP 500, 4500, and ESP VPN traffic is not working. Which action resolves this issue?

Options:

A.  

Set the allow action in the access policy to trust.

B.  

Enable IPsec inspection on the access policy.

C.  

Modify the NAT policy to use the interface PAT.

D.  

Change the access policy to allow all ports.

Discussion 0
Question # 110

How should a high-availability pair of Cisco Secure Firewall Threat Defense Virtual appliances be deployed to Cisco Secure Firewall Management Center?


Options:

A.  

Configure high availability first, then add only the primary Cisco Secure Firewall Threat Defense Virtual appliance to Cisco Secure Firewall Management Center.

B.  

Add the primary and secondary Cisco Secure Firewall Threat Defense Virtual appliances to Cisco Secure Firewall Management Center first, then configure high availability.

C.  

Add the primary appliance to Cisco Secure Firewall Management Center first, then configure high availability.

D.  

Configure high availability first, then add the primary and secondary appliances to Cisco Secure Firewall Management Center.

Discussion 0

300-710 PDF

300-710 PDF (Printable)
$54.25
$154.99

300-710 Testing Engine

300-710 PDF (Printable)
$59.5
$169.99

300-710 PDF + Testing Engine

300-710 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions