
Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Certified Ethical Hacker (CEH) Practice Questions

Question # 11

Which method can provide a better return on IT security investment and provide a thorough and comprehensive assessment of organizational security covering policy, procedure design, and implementation?

Options:

A.  

Penetration testing

B.  

Social engineering

C.  

Vulnerability scanning

D.  

Access control list reviews

Discussion 0
Question # 12

The intrusion detection system at a software development company suddenly generates multiple alerts regarding attacks against the company's external webserver, VPN concentrator, and DNS servers. What should the security team do to determine which alerts to check first?

Options:

A.  

Investigate based on the maintenance schedule of the affected systems.

B.  

Investigate based on the service level agreements of the systems.

C.  

Investigate based on the potential effect of the incident.

D.  

Investigate based on the order that the alerts arrived in.

Discussion 0
Question # 13

Which of the statements concerning proxy firewalls is correct?

Options:

A.  

Proxy firewalls increase the speed and functionality of a network.

B.  

Firewall proxy servers decentralize all activity for an application.

C.  

Proxy firewalls block network packets from passing to and from a protected network.

D.  

Computers establish a connection with a proxy firewall which initiates a new network connection for the client.

Discussion 0
Question # 14

Which of the following tools will scan a network to perform vulnerability checks and compliance auditing?

Options:

A.  

NMAP

B.  

Metasploit

C.  

Nessus

D.  

BeEF

Discussion 0
Question # 15

What type of OS fingerprinting technique sends specially crafted packets to the remote OS and analyzes the received response?

Options:

A.  

Passive

B.  

Reflective

C.  

Active

D.  

Distributive

Discussion 0
Question # 16

Which type of access control is used on a router or firewall to limit network activity?

Options:

A.  

Mandatory

B.  

Discretionary

C.  

Rule-based

D.  

Role-based

Discussion 0
Question # 17

What is the correct PCAP filter to capture all TCP traffic going to or from host 192.168.0.125 on port 25?

Options:

A.  

tcp.src == 25 and ip.host == 192.168.0.125

B.  

host 192.168.0.125:25

C.  

port 25 and host 192.168.0.125

D.  

tcp.port == 25 and ip.host == 192.168.0.125

Discussion 0
Question # 18

Jake works as a system administrator at Acme Corp. Jason, an accountant of the firm befriends him at the canteen and tags along with him on the pretext of appraising him about potential tax benefits. Jason waits for Jake to swipe his access card and follows him through the open door into the secure systems area. How would you describe Jason's behavior within a security context?

Options:

A.  

Smooth Talking

B.  

Swipe Gating

C.  

Tailgating

D.  

Trailing

Discussion 0
Question # 19

What is a sniffing performed on a switched network called?

Options:

A.  

Spoofed sniffing

B.  

Passive sniffing

C.  

Direct sniffing

D.  

Active sniffing

Discussion 0
Question # 20

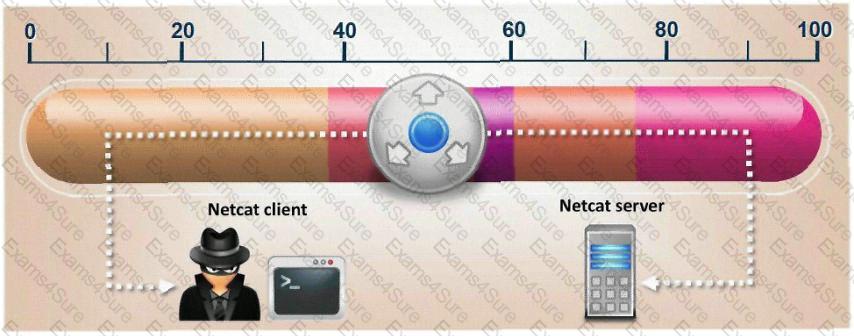
What is the correct command to run Netcat on a server using port 56 that spawns command shell when connected?

Question # 20

Options:

A.  

nc -port 56 -s cmd.exe

B.  

nc -p 56 -p -e shell.exe

C.  

nc -r 56 -c cmd.exe

D.  

nc -L 56 -t -e cmd.exe

Discussion 0

CEH-001 PDF

CEH-001 PDF (Printable)
$54.25
$154.99

CEH-001 Testing Engine

CEH-001 PDF (Printable)
$59.5
$169.99

CEH-001 PDF + Testing Engine

CEH-001 PDF (Printable)
$74.55
$212.99

Free Exams Sample Questions


