
Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free CompTIA SecurityX Certification Exam Practice Questions

Question # 91

A security engineer wants to propose an MDM solution to mitigate certain risks. The MDM solution should meet the following requirements:

• Mobile devices should be disabled if they leave the trusted zone.

• If the mobile device is lost, data is not accessible.

Which of the following options should the security engineer enable on the MDM solution? (Select two).

Options:

A.  

Geofencing

B.  

Patch management

C.  

Containerization

D.  

Full disk encryption

E.  

Allow/blocklist

F.  

Geotagging

Discussion 0
Question # 92

A company recently experienced an incident in which an advanced threat actor was able to shim malicious code against the hardware static of a domain controller The forensic team cryptographically validated that com the underlying firmware of the box and the operating system had not been compromised. However, the attacker was able to exfiltrate information from the server using a steganographic technique within LOAP Which of the following is me b»« way to reduce the risk oi reoccurrence?

Options:

A.  

Enforcing allow lists for authorized network pons and protocols

B.  

Measuring and attesting to the entire boot chum

C.  

Rolling the cryptographic keys used for hardware security modules

D.  

Using code signing to verify the source of OS updates

Discussion 0
Question # 93

A company has the following requirements for a cloud-based web application:

• Must authenticate customers

• Must prevent data exposure

• Must allow customer access to data throughout the cloud environment

• Must restrict access by specific regions

Which of the following solutions best addresses these security requirements?

Options:

A.  

Applying role-based access controls and configuring geolocation policies

B.  

Replicating the data in each customer environment

C.  

Hosting the data regionally and providing each customer with a unique link

D.  

Moving to a cloud provider that operates only in one specific region

Discussion 0
Question # 94

Due to locality and budget constraints, an organization’s satellite office has a lower bandwidth allocation than other offices. As a result, the local securityinfrastructure staff is assessing architectural options that will help preserve network bandwidth and increase speed to both internal and external resources while not sacrificing threat visibility. Which of the following would be the best option to implement?

Options:

A.  

Distributed connection allocation

B.  

Local caching

C.  

Content delivery network

D.  

SD-WAN vertical heterogeneity

Discussion 0
Question # 95

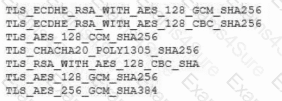
A vulnerability scan was performed on a website, and the following encryption suites were found:
Question # 95

Which of the following actions will remediate the vulnerability?

Options:

A.  

Removing any ciphers utilizing cipher block chaining

B.  

Rearranging the order of the ciphers from strongest to weakest

C.  

Deploying a WAF to monitor web traffic

D.  

Reissuing new SSL certificates for the website

Discussion 0
Question # 96

A security engineer is implementing a code signing requirement for all code developed by the organization. Currently, the PKI only generates website certificates. Which of the following steps should the engineer perform first?

Options:

A.  

Add a new template on the internal CA with the correct attributes.

B.  

Generate a wildcard certificate for the internal domain.

C.  

Recalculate a public/private key pair for the root C

A.  

D.  

Implement a SAN for all internal web applications.

Discussion 0
Question # 97

A security engineer must ensure that sensitive corporate information is not exposed if a company laptop is stolen. Which of the following actions best addresses this requirement?


Options:

A.  

Utilizing desktop as a service for all company data and multifactor authentication

B.  

Using explicit allow lists of specific IP addresses and deploying single sign-on

C.  

Deploying mobile device management and requiring stronger passwords

D.  

Updating security mobile reporting policies and monitoring data breaches

Discussion 0

CAS-005 PDF

CAS-005 PDF (Printable)
$46.5
$154.99

CAS-005 Testing Engine

CAS-005 PDF (Printable)
$51
$169.99

CAS-005 PDF + Testing Engine

CAS-005 PDF (Printable)
$63.9
$212.99

Free Exams Sample Questions

