
Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) Practice Questions

Question # 1

Which security model assumes an attacker within and outside of the network and enforces strict verification before connecting to any system or resource within the organization?

Options:

A.  

Biba

B.  

Object-capability

C.  

Take-Grant

D.  

Zero Trust

Discussion 0
Question # 2

What describes the defense-m-depth principle?

Options:

A.  

defining precise guidelines for new workstation installations

B.  

categorizing critical assets within the organization

C.  

isolating guest Wi-Fi from the focal network

D.  

implementing alerts for unexpected asset malfunctions

Discussion 0
Question # 3

What is the impact of false negative alerts when compared to true negative alerts?

Options:

A.  

A true negative is a legitimate attack that triggers a brute force alert, and a false negative is when no alert and no attack is occurring.

B.  

A true negative is an alert for an exploit attempt when no attack was detected, and a false negative is when no attack happens and an alert is still raised.

C.  

A false negative is an event that alerts for injection attack when no attack is happening, and a true negative is an attack that happens and an alert that is appropriately raised.

D.  

A false negative is someone trying to hack into the system and no alert is raised, and a true negative is an event that never happened and an alert was not raised.

Discussion 0
Question # 4

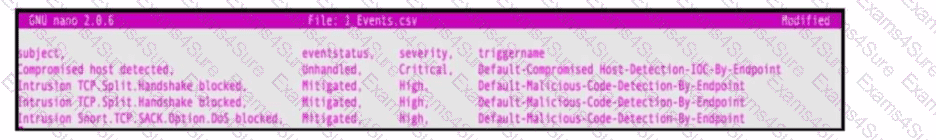
An engineer needs to fetch logs from a proxy server and generate actual events according to the data received. Which technology should the engineer use to accomplish this task?
Options:

A.  

Firepower

B.  

Email Security Appliance

C.  

Web Security Appliance

D.  

Stealthwatch

Discussion 0
Question # 5

Which statement describes patch management?

Options:

A.  

scanning servers and workstations for missing patches and vulnerabilities

B.  

managing and keeping previous patches lists documented for audit purposes

C.  

process of appropriate distribution of system or software updates

D.  

workflow of distributing mitigations of newly found vulnerabilities

Discussion 0
Question # 6

Question # 6

Refer to the exhibit. An engineer must map these events to the source technology that generated the event logs. To which technology do the generated logs belong?

Options:

A.  

proxy

B.  

antivirus

C.  

IPS

D.  

firewall

Discussion 0
Question # 7

A data privacy officer at a marketing firm has received a request from a former client to delete all personally sensitive information held by the company. The firm operates globally and follows international data protection standards. The only information retained about the client is a unique customer ID, "051473912", which is not directly tied to the name, address, or any other identifiable details. Which action should the data privacy officer take?

Options:

A.  

Delete the data immediately to comply with all global privacy regulations.

B.  

Retain the data, as a customer ID by itself does not qualify as PSI under international standards.

C.  

Consult the legal team, as customer IDs are always considered PSI and cannot be retained.

D.  

Delete the data if the customer ID is stored alongside additional information that can identify the client.

Discussion 0
Question # 8

A large load of data is being transferred to an external destination via UDP 53 port. Which obfuscation technique is used?

Options:

A.  

proxied traffic

B.  

C&C connection

C.  

data masking

D.  

DNS tunneling

Discussion 0
Question # 9

Which tool provides a full packet capture from network traffic?

Options:

A.  

Nagios

B.  

CAINE

C.  

Hydra

D.  

Wireshark

Discussion 0
Question # 10

What is the difference between attack surface and vulnerability?

Options:

A.  

An attack surface is a way of taking advantage of a system or resource, and a vulnerability is a specific technique utilized by the vulnerability.

B.  

A vulnerability describes how software or a system is exposed to potential attacks, and an attack surface is an actual weakness that exposes the potential risk.

C.  

A vulnerability is a way of taking advantage of a system or resource, and an attack surface is a specific technique utilized by the vulnerability.

D.  

An attack surface describes how software or a system is exposed to potential attacks, and a vulnerability is an actual weakness that exposes the potential risk.

Discussion 0

200-201 PDF

200-201 PDF (Printable)
$54.25
$154.99

200-201 Testing Engine

200-201 PDF (Printable)
$59.5
$169.99

200-201 PDF + Testing Engine

200-201 PDF (Printable)
$74.55
$212.99
Exams4sure Dumps

Exam style questions across every 200-201 domain

Last Update 14 hours ago
Total Questions : 476

Start with our free 200-201 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CyberOps Associate exam. Each 200-201 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.


Free Exams Sample Questions
