Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) Practice Questions

Exams4sure Dumps

Exam style questions across every 200-201 domain

Last Update 3 days ago
Total Questions : 476

Start with our free 200-201 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CyberOps Associate exam. Each 200-201 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

200-201 PDF

200-201 PDF (Printable)
$46.5
$154.99

200-201 Testing Engine

200-201 PDF (Printable)
$51
$169.99

200-201 PDF + Testing Engine

200-201 PDF (Printable)
$63.9
$212.99
Question # 121

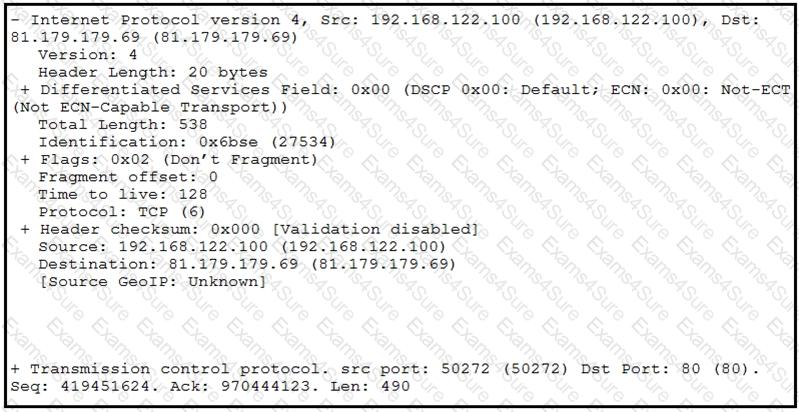
Refer to the exhibit.

Question # 121

What should be interpreted from this packet capture?

Options:

A.  

81.179.179.69 is sending a packet from port 80 to port 50272 of IP address 192.168.122.100 using UDP protocol.

B.  

192.168.122.100 is sending a packet from port 50272 to port 80 of IP address 81.179.179.69 using TCP protocol.

C.  

192.168.122.100 is sending a packet from port 80 to port 50272 of IP address 81.179.179.69 using UDP protocol.

D.  

81.179.179.69 is sending a packet from port 50272 to port 80 of IP address 192.168.122.100 using TCP UDP protocol.

Discussion 0
Question # 122

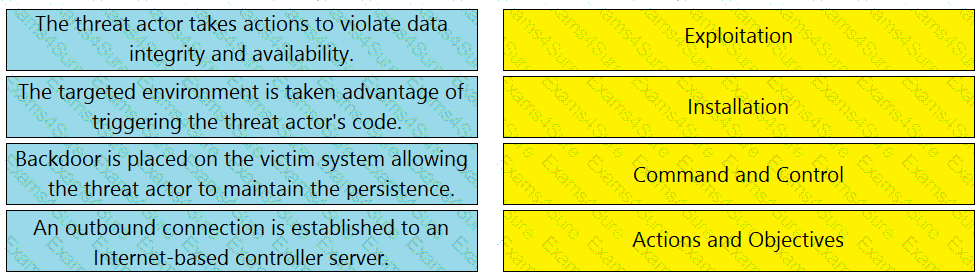
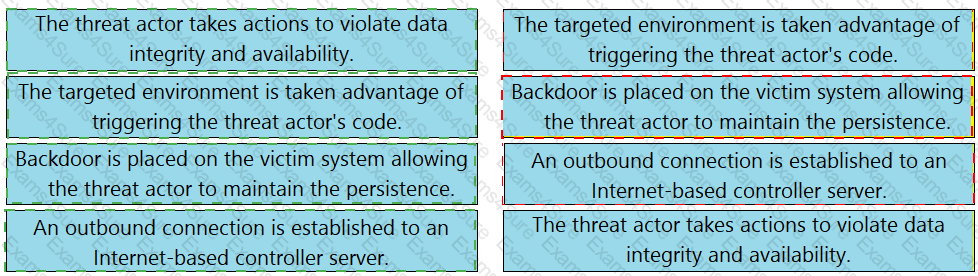
Drag and drop the definition from the left onto the phase on the right to classify intrusion events according to the Cyber Kill Chain model.
Question # 122

Options:

Discussion 0
Question # 123

A company receptionist received a threatening call referencing stealing assets and did not take any action assuming it was a social engineering attempt. Within 48 hours, multiple assets were breached, affecting the confidentiality of sensitive information. What is the threat actor in this incident?

Options:

A.  

companyassets that are threatened

B.  

customer assets that are threatened

C.  

perpetrators of the attack

D.  

victims of the attack

Discussion 0
Question # 124

Why should an engineer use a full packet capture to investigate a security breach?

Options:

A.  

It captures the TCP flags set within each packet for the engineer to focus on suspicious packets to identify malicious activity

B.  

It collects metadata for the engineer to analyze, including IP traffic packet data that is sorted, parsed, and indexed.

C.  

It provides the full TCP streams for the engineer to follow the metadata to identify the incoming threat.

D.  

It reconstructs the event allowing the engineer to identify the root cause by seeing what took place during the breach

Discussion 0
Question # 125

What is a description of a social engineering attack?

Options:

A.  

fake offer for free music download to trick the user into providing sensitive data

B.  

package deliberately sent to the wrong receiver to advertise a new product

C.  

mistakenly received valuable order destined for another person and hidden on purpose

D.  

email offering last-minute deals on various vacations around the world with a due date and a counter

Discussion 0
Question # 126

A security engineer must implement an Intrusion Prevention System (IPS) inside an organization’s DMZ. One of the requirements is the ability to block suspicious traffic in real time based on a triggered signature. The IPS will be connected behind the DMZ firewalls directly to the core switches. Which traffic integration method must be implemented to complete this project?

Options:

A.  

mirroring

B.  

tap

C.  

inline

D.  

passive

Discussion 0
Question # 127

What are two differences between tampered disk images and untampered disk images'? (Choose two.)

Options:

A.  

Tampered Images are used in a security investigation process

B.  

Untampered images can be used as law enforcement evidence.

C.  

The image is untampered if the existing stored hash matches the computed one

D.  

The image is tampered if the stored hash and the computed hash are identical

E.  

Tampered images are used as an element for the root cause analysis report

Discussion 0
Question # 128

Which type of attack uses a botnet to reflect requests off of an NTP server to overwhelm a target?

Options:

A.  

Display

B.  

Man-in-the-middle

C.  

Distributed denial of service

D.  

Denial of service

Discussion 0
Question # 129

What is obtained using NetFlow?

Options:

A.  

session data

B.  

application logs

C.  

network downtime report

D.  

full packet capture

Discussion 0
Question # 130

Which metric in CVSS indicates an attack that takes a destination bank account number and replaces it with a different bank account number?


Options:

A.  

integrity

B.  

confidentiality

C.  

availability

D.  

scope

Discussion 0

Free Exams Sample Questions