Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) Practice Questions

Exams4sure Dumps

Exam style questions across every 200-201 domain

Last Update 3 days ago
Total Questions : 476

Start with our free 200-201 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CyberOps Associate exam. Each 200-201 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

200-201 PDF

200-201 PDF (Printable)
$46.5
$154.99

200-201 Testing Engine

200-201 PDF (Printable)
$51
$169.99

200-201 PDF + Testing Engine

200-201 PDF (Printable)
$63.9
$212.99
Question # 91

What is data tunneling?

Options:

A.  

Encrypted information is returned to its original format.

B.  

Data is split into packets and transported to the destination.

C.  

Packets are transformed into bytes and assembled by a receiver.

D.  

Malicious data is hidden within legitimate system processes.

Discussion 0
Question # 92

What is the impact of encapsulation on the network?

Options:

A.  

Something significant is concealed from virtually separate networks.

B.  

Logically separate functions in the network are abstracted from their underlying structures.

C.  

Numerous local private addresses are mapped to a public one before the data is moved.

D.  

Web requests are taken on behalf of users and the response is collected from the web.

Discussion 0
Question # 93

Which security technology guarantees the integrity and authenticity of all messages transferred to and from a web application?

Options:

A.  

Hypertext Transfer Protocol

B.  

SSL Certificate

C.  

Tunneling

D.  

VPN

Discussion 0
Question # 94

What ate two categories of DDoS attacks? (Choose two.)

Options:

A.  

split brain

B.  

scanning

C.  

phishing

D.  

reflected

E.  

direct

Discussion 0
Question # 95

Which statement describes indicators of attack?

Options:

A.  

internal hosts communicate with countries outside of the business range.

B.  

Phishing attempts on an organization are blocked by mall AV.

C.  

Critical patches are missing.

D.  

A malicious file is detected by the AV software.

Discussion 0
Question # 96

An employee reports that someone has logged into their system and made unapproved changes, files are out of order, and several documents have been placed in the recycle bin. The security specialist reviewed the system logs, found nothing suspicious, and was not able to determine what occurred. The software is up to date; there are no alerts from antivirus and no failed login attempts. What is causing the lack of data visibility needed to detect the attack?

Options:

A.  

The threat actor used a dictionary-based password attack to obtain credentials.

B.  

The threat actor gained access to the system by known credentials.

C.  

The threat actor used the teardrop technique to confuse and crash login services.

D.  

The threat actor used an unknown vulnerability of the operating system that went undetected.

Discussion 0
Question # 97

A compliance analyst receives a complaint from a customer regarding personal data being unlawfully retained despite a deletion request. The company is based in Europe and must comply with GDPR. The only data collected is the email address 0524l9i75@gmail.com. How should the compliance analyst act?

Options:

A.  

Do not delete the data — the email address is not considered PII

B.  

Delete the data regardless of where the customer is from

C.  

Delete the data if the customer is from the EU

D.  

Notify the legal team about a data compliance breach

Discussion 0
Question # 98

An engineer is investigating a case of the unauthorized usage of the “Tcpdump” tool. The analysis revealed that a malicious insider attempted to sniff traffic on a specific interface. What type of information did the malicious insider attempt to obtain?

Options:

A.  

tagged protocols being used on the network

B.  

all firewall alerts and resulting mitigations

C.  

tagged ports being used on the network

D.  

all information and data within the datagram

Discussion 0
Question # 99

According to the September 2020 threat intelligence feeds a new malware called Egregor was introduced and used in many attacks. Distnbution of Egregor is pnmanly through a Cobalt Strike that has been installed on victim's workstations using RDP exploits Malware exfiltrates the victim's data to a command and control server. The data is used to force victims pay or lose it by publicly releasing it. Which type of attack is described?

Options:

A.  

malware attack

B.  

ransomware attack

C.  

whale-phishing

D.  

insider threat

Discussion 0
Question # 100

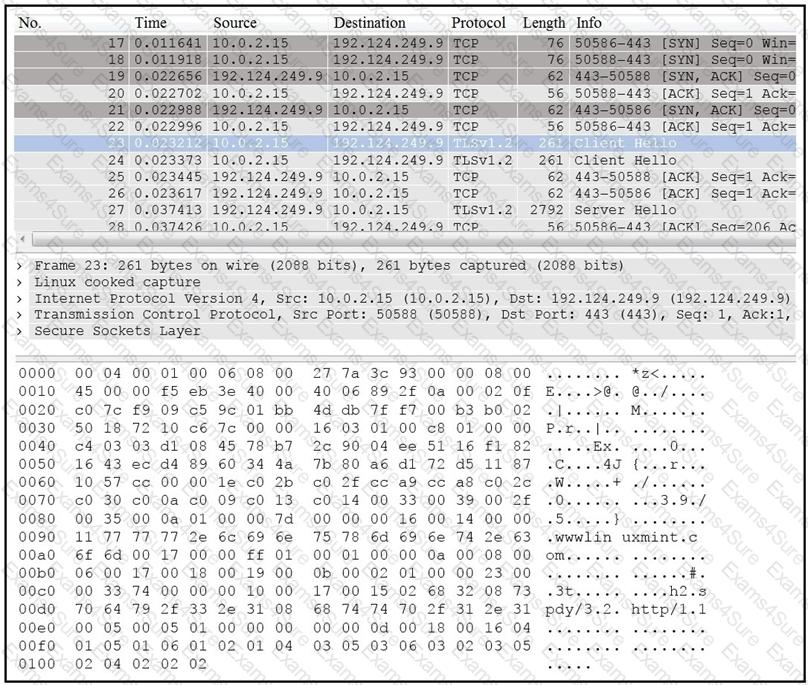
Refer to the exhibit.

Question # 100

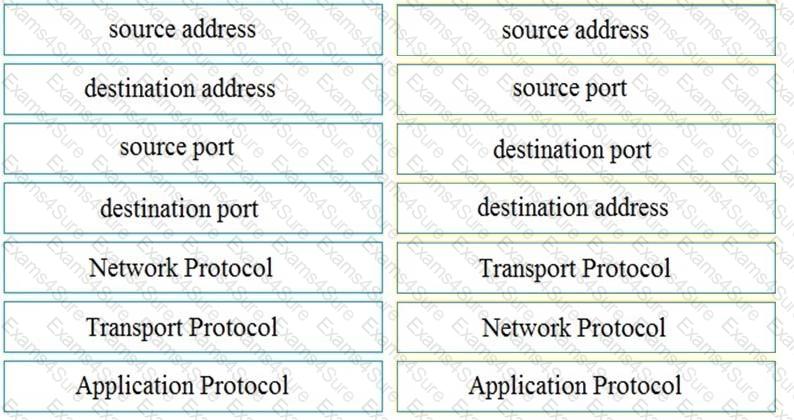
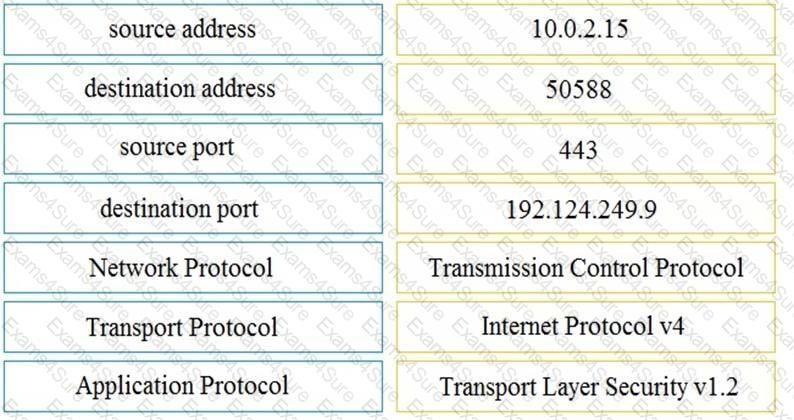
Drag and drop the element name from the left onto the correct piece of the PCAP file on the right.
Question # 100

Options:

Discussion 0

Free Exams Sample Questions