

Exam style questions across every 200-201 domain
Last Update 3 days ago
Total Questions : 476
Start with our free 200-201 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CyberOps Associate exam. Each 200-201 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

Refer to the exhibit.
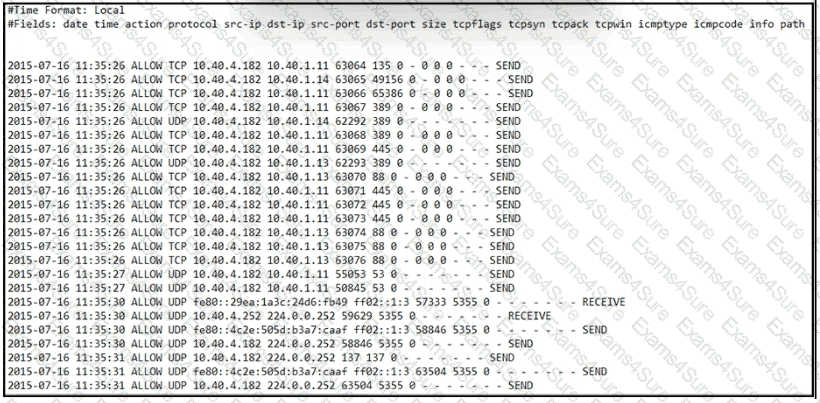
An engineer received an event log file to review. Which technology generated the log?
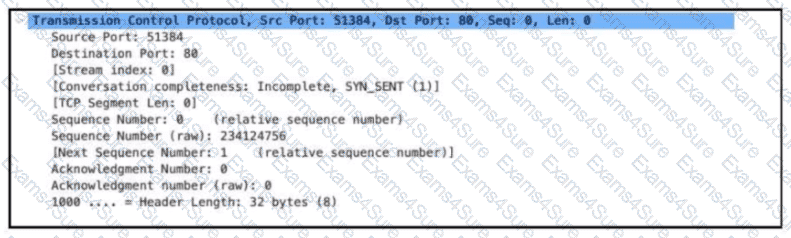
An engineer must configure network systems to detect command-and-control communications by decrypting ingress and egress perimeter traffic and allowing network security devices to detect malicious outbound communications. Which technology must be used to accomplish this task?
An investigator is examining a copy of an ISO file that is stored in CDFS format. What type of evidence is this file?
Endpoint logs indicate that a machine has obtained an unusual gateway address and unusual DNS servers via DHCP Which type of attack is occurring?
An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap. Which command will accomplish this goal?



