Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: merry71

Free Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) Practice Questions

Exams4sure Dumps

Exam style questions across every 200-201 domain

Last Update 3 days ago
Total Questions : 476

Start with our free 200-201 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CyberOps Associate exam. Each 200-201 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

200-201 PDF

200-201 PDF (Printable)
$46.5
$154.99

200-201 Testing Engine

200-201 PDF (Printable)
$51
$169.99

200-201 PDF + Testing Engine

200-201 PDF (Printable)
$63.9
$212.99
Question # 61

What is a difference between SOAR and SIEM?

Options:

A.  

SOAR platforms are used for threat and vulnerability management, but SIEM applications are not

B.  

SIEM applications are used for threat and vulnerability management, but SOAR platforms are not

C.  

SOAR receives information from a single platform and delivers it to a SIEM

D.  

SIEM receives information from a single platform and delivers it to a SOAR

Discussion 0
Question # 62

What should an engineer use to aid the trusted exchange of public keys between user tom0411976943 and dan1968754032?

Options:

A.  

central key management server

B.  

web of trust

C.  

trusted certificate authorities

D.  

registration authority data

Discussion 0
Question # 63

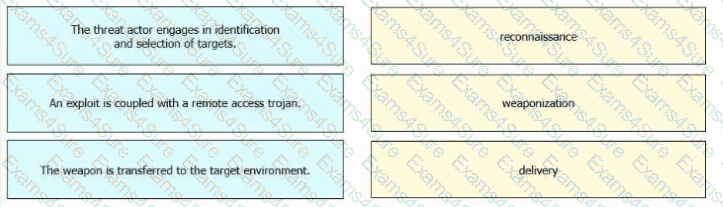
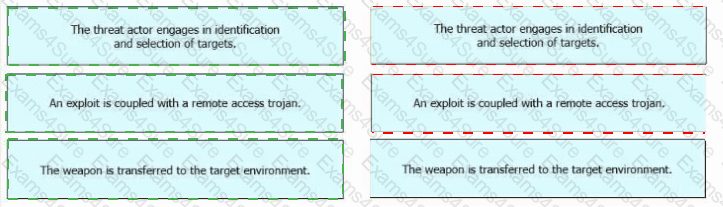
Drag and drop the definitions from the left onto the phases on the right to classify intrusion events according to the Cyber Kill Chain model.
Question # 63

Options:

Discussion 0
Question # 64

Question # 64

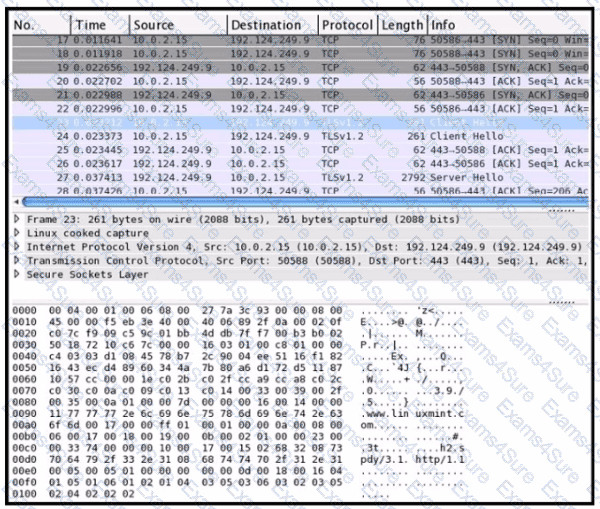
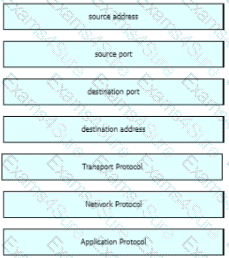
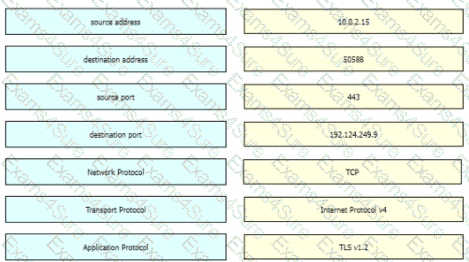
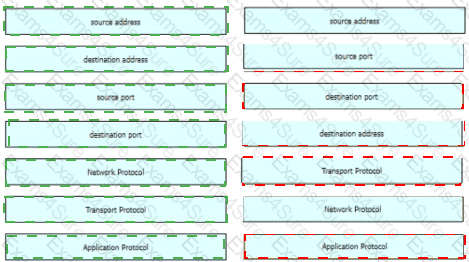
Refer to the exhibit Drag and drop the element names from the left onto the corresponding pieces of the PCAP file on the right.
Question # 64

Options:

Discussion 0
Question # 65

Which attack is the network vulnerable to when a stream cipher like RC4 is used twice with the same key?

Options:

A.  

forgery attack

B.  

plaintext-only attack

C.  

ciphertext-only attack

D.  

meet-in-the-middle attack

Discussion 0
Question # 66

Which access control should a chief information security officer select to protect extremely sensitive data categorized at various levels of confidentiality?

Options:

A.  

MAC; each object owner is responsible to provide access only to authorized users.

B.  

MAC; access control decisions are centrally managed and minimize the human error probability.

C.  

DAC; access control decisions are centrally managed and minimize the human error probability.

D.  

DAC; each object owner is responsible to provide access only to authorized users.

Discussion 0
Question # 67

Which category relates to improper use or disclosure of PII data?

Options:

A.  

legal

B.  

compliance

C.  

regulated

D.  

contractual

Discussion 0
Question # 68

What are the two differences between stateful and deep packet inspection? (Choose two )

Options:

A.  

Stateful inspection is capable of TCP state tracking, and deep packet filtering checks only TCP source and destination ports

B.  

Deep packet inspection is capable of malware blocking, and stateful inspection is not

C.  

Deep packet inspection operates on Layer 3 and 4. and stateful inspection operates on Layer 3 of the OSI model

D.  

Deep packet inspection is capable of TCP state monitoring only, and stateful inspection can inspect TCP and UDP.

E.  

Stateful inspection is capable of packet data inspections, and deep packet inspection is not

Discussion 0
Question # 69

What is a benefit of agent-based protection when compared to agentless protection?

Options:

A.  

It lowers maintenance costs

B.  

It provides a centralized platform

C.  

It collects and detects all traffic locally

D.  

It manages numerous devices simultaneously

Discussion 0
Question # 70

An organization's security team detected network spikes coming from the internal network. An investigation concluded that the spike in traffic was from intensive network scanning. How must the analyst collect the traffic to isolate the suspicious host?


Options:

A.  

Based on the protocols used

B.  

Based on the most used applications

C.  

By most used ports

D.  

By most active source IP

Discussion 0

Free Exams Sample Questions