Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 4 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 31

A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?

Options:

A.  

DHCP snooping has not been enabled on all VLANs.

B.  

The ip arp inspection limit command is applied on all interfaces and is blocking the traffic of all users.

C.  

Dynamic ARP Inspection has not been enabled on all VLANs

D.  

The no ip arp inspection trust command is applied on all user host interfaces

Discussion 0
Question # 32

For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)

Options:

A.  

Windows service

B.  

computer identity

C.  

user identity

D.  

Windows firewall

E.  

default browser

Discussion 0
Question # 33

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

Options:

A.  

Create an LDAP authentication realm and disable transparent user identification.

B.  

Create NTLM or Kerberos authentication realm and enable transparent user identification.

C.  

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

D.  

The eDirectory client must be installed on each client workstation.

E.  

Deploy a separate eDirectory server; the dent IP address is recorded in this server.

Discussion 0
Question # 34

Which Talos reputation center allows you to track the reputation of IP addresses for email and web traffic?

Options:

A.  

IP Blacklist Center

B.  

File Reputation Center

C.  

AMP Reputation Center

D.  

IP and Domain Reputation Center

Discussion 0
Question # 35

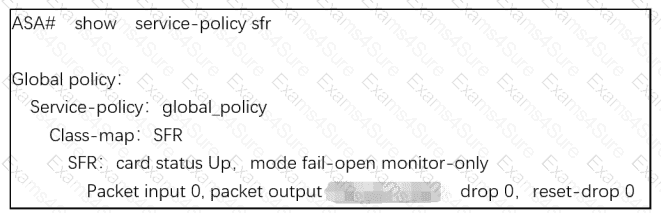
Refer to the exhibit.

Question # 35

What are two indications of the Cisco Firepower Services Module configuration?

(Choose two.)

Options:

A.  

The module is operating in IDS mode.

B.  

Traffic is blocked if the module fails.

C.  

The module fails to receive redirected traffic.

D.  

The module is operating in IPS mode.

E.  

Traffic continues to flow if the module fails.

Discussion 0
Question # 36

Which two actions does the Cisco identity Services Engine posture module provide that ensures endpoint security?(Choose two.)

Options:

A.  

The latest antivirus updates are applied before access is allowed.

B.  

Assignments to endpoint groups are made dynamically, based on endpoint attributes.

C.  

Patch management remediation is performed.

D.  

A centralized management solution is deployed.

E.  

Endpoint supplicant configuration is deployed.

Discussion 0
Question # 37

A network engineer is configuring a Cisco Catalyst switch. The network engineer must prevent traffic on the network from being interrupted by broadcast packets flooding the network using a predefined threshold. What must be configured on the switch?

Options:

A.  

DHCP Snooping

B.  

Embedded Event Monitoring

C.  

Storm Control

D.  

Loop Guard

Discussion 0
Question # 38

Refer to the exhibit.

aaa new-model

aaa authentication dot1x default group ISE-SERVERS

aaa authorization network default group ISE-SERVERS

aaa accounting dot1x default start-stop group ISE-SERVERS

!

radius server RADIUS_SRV

address ipv4 172.16.10.12 auth-port 1812 acct-port 1813

key shared-secret C1sc0123

!

aaa group server radius ISE-SERVERS

server name RADIUS_SRV

radius-server vsa send authentication

radius-server vsa send accounting

radius-server attribute 6 on-for-login-auth

radius-server attribute 8 include-in-access-req

radius-server attribute 25 access-request include

ip device tracking

!

interface range GigabitEthernet1/0/1 - 48

switchport

switchport host

authentication priority dot1x mab

authentication order dot1x mab

A security engineer is integrating a new Cisco Catalyst access switch with Cisco ISE to enforce port-based network access control using 802.1X. The AAA RADIUS server group and access interfaces are configured on the Cisco Catalyst switch. Cisco ISE has authentication and authorization policies, the workstation supplicants are configured as expected, and connectivity between the switch and ISE is working. During testing, the workstations fail to trigger authentication sessions, and no RADIUS requests appear in the ISE logs or on the switch interfaces. Which two configuration commands must be added to the Cisco Catalyst switch? (Choose two.)

Options:

A.  

Configure the dot1x system-auth-control command globally.

B.  

Implement the aaa server radius dynamic-author command globally.

C.  

Apply the dot1x pae authenticator command under interfaces that require 802.1X.

D.  

Configure the ip radius source-interface command globally.

E.  

Add the mab command under all switch interfaces.

Discussion 0
Question # 39

Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data

within a network perimeter?

Options:

A.  

cloud web services

B.  

network AMP

C.  

private cloud

D.  

public cloud

Discussion 0
Question # 40

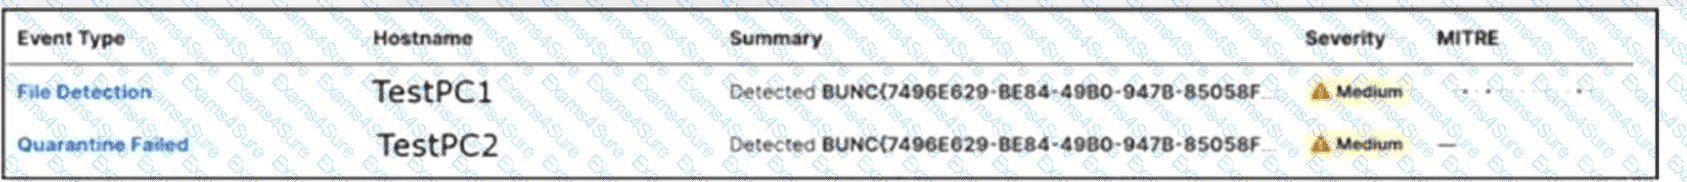
Refer to the exhibit.

Question # 40

A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?

Options:

A.  

The event data does not establish whether the threat remains present or was remediated through another mechanism.

B.  

The failed-quarantine status proves that the endpoint was unable to apply the configured remediation policy.

C.  

The failed-quarantine status proves that the file remained accessible to the operating system after the remediation attempt.

D.  

The failed-quarantine status proves that the threat continued executing after the remediation attempt.

Discussion 0
Question # 41

A mall provides security services to customers with a shared appliance. The mall wants separation of

management on the shared appliance. Which ASA deployment mode meets these needs?

Options:

A.  

routed mode

B.  

transparent mode

C.  

multiple context mode

D.  

multiple zone mode

Discussion 0
Question # 42

Which threat intelligence standard contains malware hashes?

Options:

A.  

structured threat information expression

B.  

advanced persistent threat

C.  

trusted automated exchange or indicator information

D.  

open command and control

Discussion 0
Question # 43

Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?

Options:

A.  

TLSv1.2

B.  

TLSv1.1

C.  

BJTLSv1

D.  

DTLSv1

Discussion 0
Question # 44

Where are individual sites specified to be blacklisted in Cisco Umbrella?

Options:

A.  

application settings

B.  

content categories

C.  

security settings

D.  

destination lists

Discussion 0
Question # 45

What is a benefit of using a multifactor authentication strategy?

Options:

A.  

It provides visibility into devices to establish device trust.

B.  

It provides secure remote access for applications.

C.  

It provides an easy, single sign-on experience against multiple applications

D.  

lt protects data by enabling the use of a second validation of identity.

Discussion 0

Free Exams Sample Questions