Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 4 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 76

What is the result of running the crypto isakmp key ciscXXXXXXXX address 172.16.0.0 command?
Options:

A.  

authenticates the IKEv2 peers in the 172.16.0.0/16 range by using the key ciscXXXXXXXX

B.  

authenticates the IP address of the 172.16.0.0/32 peer by using the key ciscXXXXXXXX

C.  

authenticates the IKEv1 peers in the 172.16.0.0/16 range by using the key ciscXXXXXXXX

D.  

secures all the certificates in the IKE exchange by using the key ciscXXXXXXXX

Discussion 0
Question # 77

Question # 77

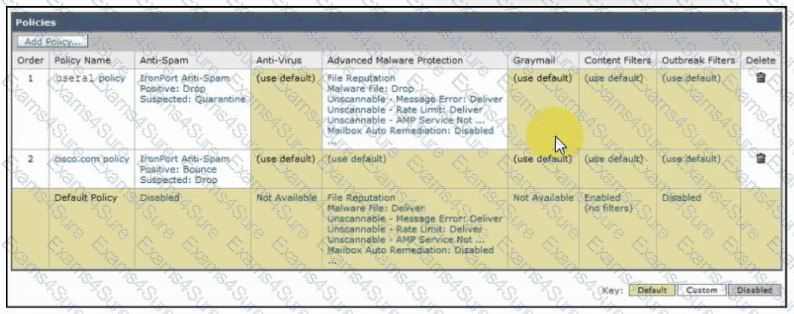
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?

Options:

A.  

Policy Name: Default Policy  Sender: usera1@example.com  Recipient: @cisco.com

B.  

Policy Name: usera1 policy  Sender: usera1@example.com  Recipient: @cisco.com

C.  

Policy Name: Anti-Malware policy  Sender: usera1@example.com  Recipient: @cisco.com

D.  

Policy Name: cisco.com policy  Sender: usera1@example.com  Recipient: @cisco.com

Discussion 0
Question # 78

Refer to the exhibit.

Question # 78

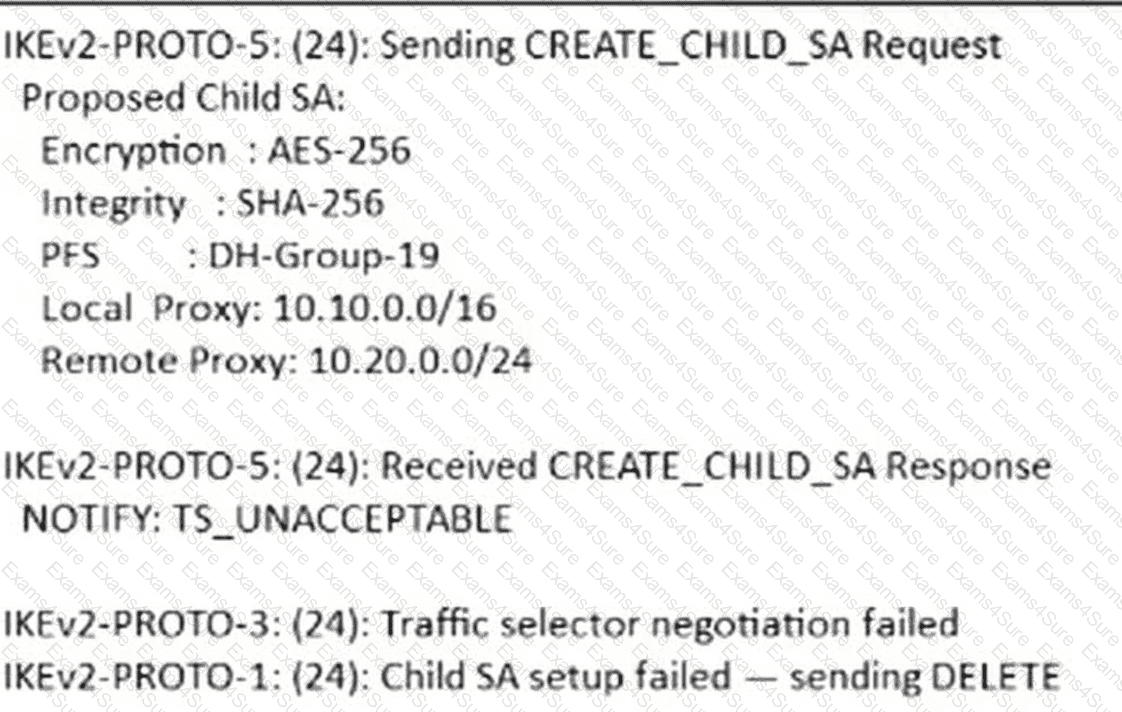
A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_S

A.  

The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?

Options:

A.  

Align the protected network definitions on both firewalls so that the local and remote traffic selectors proposed during CREATE_CHILD_SA match on both peers.

B.  

Change the IPsec encryption algorithm from AES-256 to AES-128 on the initiating firewall and redeploy the VPN policy.

C.  

Extend the IKE SA lifetime on both firewalls to give CREATE_CHILD_SA sufficient time to complete the negotiation before the Phase 1 SA expires.

D.  

Remove DH Group 19 from the IPsec proposal on the initiating FTD because the TS_UNACCEPTABLE notification indicates that the responder does not support the proposed PFS group.

Discussion 0
Question # 79

An organization is selecting a cloud architecture and does not want to be responsible for patch management of the operating systems. Why should the organization select either Platform as a Service or Infrastructure as a Service for this environment?

Options:

A.  

Platform as a Service because the customer manages the operating system

B.  

Infrastructure as a Service because the customer manages the operating system

C.  

Platform as a Service because the service provider manages the operating system

D.  

Infrastructure as a Service because the service provider manages the operating system

Discussion 0
Question # 80

What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?

Options:

A.  

It allows the administrator to quarantine malicious files so that the application can function, just notmaliciously.

B.  

It discovers and controls cloud apps that are connected to a company’s corporate environment.

C.  

It deletes any application that does not belong in the network.

D.  

It sends the application information to an administrator to act on.

Discussion 0
Question # 81

Which PKI enrollment method allows the user to separate authentication and enrollment actions and also

provides an option to specify HTTP/TFTP commands to perform file retrieval from the server?

Options:

A.  

url

B.  

terminal

C.  

profile

D.  

selfsigned

Discussion 0
Question # 82

What is the benefit of installing Cisco AMP for Endpoints on a network?

Options:

A.  

It provides operating system patches on the endpoints for security.

B.  

It provides flow-based visibility for the endpoints network connections.

C.  

It enables behavioral analysis to be used for the endpoints.

D.  

It protects endpoint systems through application control and real-time scanning

Discussion 0
Question # 83

An email administrator is setting up a new Cisco ES

A.  

The administrator wants to enable the blocking of greymail for the end user. Which feature must the administrator enable first?

Options:

A.  

File Analysis

B.  

IP Reputation Filtering

C.  

Intelligent Multi-Scan

D.  

Anti-Virus Filtering

Discussion 0
Question # 84

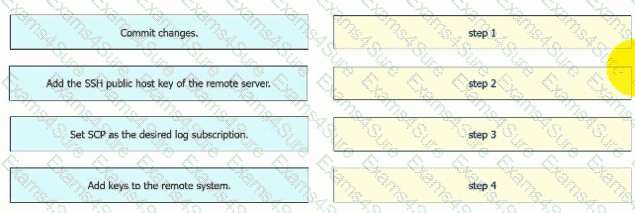
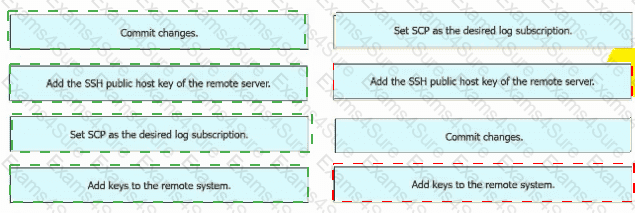
An engineer must configure AsyncOS for Cisco Secure Web Appliance to push log files to a syslog server using the SCP retrieval method. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
Question # 84

Options:

Discussion 0
Question # 85

Which component of Cisco umbrella architecture increases reliability of the service?

Options:

A.  

Anycast IP

B.  

AMP Threat grid

C.  

Cisco Talos

D.  

BGP route reflector

Discussion 0
Question # 86

Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?

Options:

A.  

AFL

B.  

Fuzzing Framework

C.  

Radamsa

D.  

OWASP

Discussion 0
Question # 87

Which cloud service model offers an environment for cloud consumers to develop and deploy applications

without needing to manage or maintain the underlying cloud infrastructure?

Options:

A.  

PaaS

B.  

XaaS

C.  

IaaS

D.  

SaaS

Discussion 0
Question # 88

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco Secure Email Gateway?

Options:

A.  

outbreakconfig

B.  

websecurityconfig

C.  

webadvancedconfig

D.  

websecurityadvancedconfig

Discussion 0
Question # 89

Which solution stops unauthorized access to the system if a user ' s password is compromised?

Options:

A.  

VPN

B.  

MFA

C.  

AMP

D.  

SSL

Discussion 0
Question # 90

Email security has become a high priority task for a security engineer at a large multi-national organization due to ongoing phishing campaigns. To help control this, the engineer has deployed an Incoming Content Filter with a URL reputation of (-10 00 to -6 00) on the Cisco ESA Which action will the system perform to disable any links in messages that match the filter?


Options:

A.  

Defang

B.  

Quarantine

C.  

FilterAction

D.  

ScreenAction

Discussion 0

Free Exams Sample Questions