An engineer is implementing NTP authentication within their network and has configured both the client and server devices with the command ntp authentication-key 1 md5 Cisc392368270. The server at 1.1.1.1 is attempting to authenticate to the client at 1.1.1.2, however it is unable to do so. Which command is required to enable the client to accept the server’s authentication key?
Which CoA response code is sent if an authorization state is changed successfully on a Cisco IOS device?
Which Cisco ASA deployment model is used to filter traffic between hosts in the same IP subnet using higher-level protocols without readdressing the network?
What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?
Which solution detects threats across a private network, public clouds, and encrypted traffic?
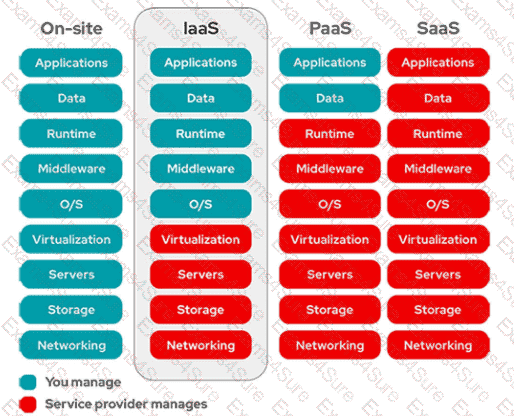
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)
What are two advantages of using Cisco Any connect over DMVPN? (Choose two)
Refer to the exhibit.
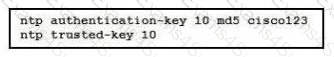
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
Which feature of a secure CI/CD pipeline defends container workloads against detected exploits, application flaws, configuration errors, and policy violations?
A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?
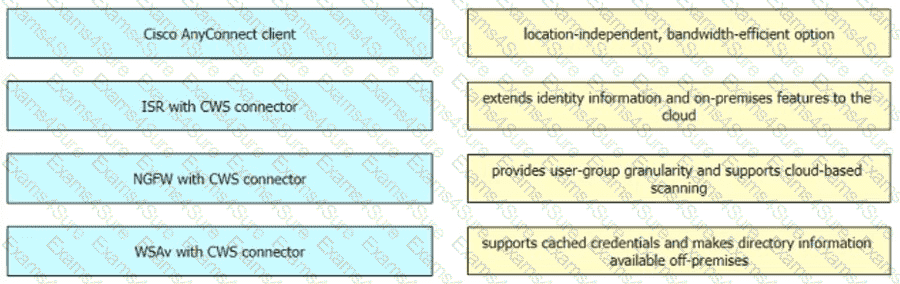
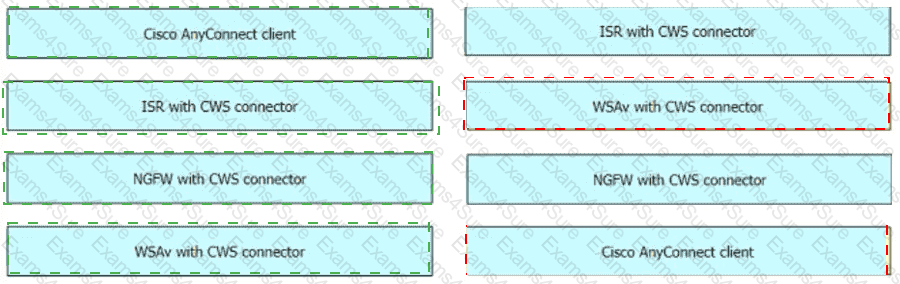
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which
vulnerability allows the attacker to see the passwords being transmitted in clear text?
Which type of algorithm provides the highest level of protection against brute-force attacks?