Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 65pass65

Free Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Practice Questions

Exams4sure Dumps

Exam style questions across every 350-701 domain

Last Update 5 hours ago
Total Questions : 801

Start with our free 350-701 practice questions, carefully crafted to mirror the domains, phrasing, and difficulty of the real CCNP Security exam. Each 350-701 exam question comes with a detailed rationale that explains not just which answer is correct but why the others fall short. That's how concepts stick. Use the free set to benchmark yourself: identify your Cisco weak domains, see where you're losing marks, and build a focused study plan in minutes.

350-701 PDF

350-701 PDF (Printable)
$54.25
$154.99

350-701 Testing Engine

350-701 PDF (Printable)
$59.5
$169.99

350-701 PDF + Testing Engine

350-701 PDF (Printable)
$74.55
$212.99
Question # 196

What is a difference between Cisco AMP for Endpoints and Cisco Umbrella?

Options:

A.  

Cisco AMP for Endpoints is a cloud-based service, and Cisco Umbrella is not.

B.  

Cisco AMP for Endpoints prevents connections to malicious destinations, and C malware.

C.  

Cisco AMP for Endpoints automatically researches indicators of compromise ..

D.  

Cisco AMP for Endpoints prevents, detects, and responds to attacks before and against Internet threats.

Discussion 0
Question # 197

What Cisco command shows you the status of an 802.1X connection on interface gi0/1?

Options:

A.  

show authorization status

B.  

show authen sess int gi0/1

C.  

show connection status gi0/1

D.  

show ver gi0/1

Discussion 0
Question # 198

When configuring ISAKMP for IKEv1 Phase1 on a Cisco IOS router, an administrator needs to input the

command crypto isakmp key cisco address 0.0.0.0. The administrator is not sure what the IP addressing in this command issued for. What would be the effect of changing the IP address from 0.0.0.0 to 1.2.3.4?

Options:

A.  

The key server that is managing the keys for the connection will be at 1.2.3.4

B.  

The remote connection will only be allowed from 1.2.3.4

C.  

The address that will be used as the crypto validation authority

D.  

All IP addresses other than 1.2.3.4 will be allowed

Discussion 0
Question # 199

Which feature is used in a push model to allow for session identification, host reauthentication, and session termination?

Options:

A.  

AAA attributes

B.  

CoA request

C.  

AV pair

D.  

carrier-grade NAT

Discussion 0
Question # 200

Which two prevention techniques are used to mitigate SQL injection attacks? (Choose two)

Options:

A.  

Check integer, float, or Boolean string parameters to ensure accurate values.

B.  

Use prepared statements and parameterized queries.

C.  

Secure the connection between the web and the app tier.

D.  

Write SQL code instead of using object-relational mapping libraries.

E.  

Block SQL code execution in the web application database login.

Discussion 0
Question # 201

Which two application layer preprocessors are used by Firepower Next Generation Intrusion Prevention

System? (Choose two)

Options:

A.  

packet decoder

B.  

SIP

C.  

modbus

D.  

inline normalization

E.  

SSL

Discussion 0
Question # 202

Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the

deployment?

Options:

A.  

NGFW

B.  

AMP

C.  

WSA

D.  

ESA

Discussion 0
Question # 203

When choosing an algorithm to us, what should be considered about Diffie Hellman and RSA for key

establishment?

Options:

A.  

RSA is an asymmetric key establishment algorithm intended to output symmetric keys

B.  

RSA is a symmetric key establishment algorithm intended to output asymmetric keys

C.  

DH is a symmetric key establishment algorithm intended to output asymmetric keys

D.  

DH is an asymmetric key establishment algorithm intended to output symmetric keys

Discussion 0
Question # 204

A company recently discovered an attack propagating throughout their Windows network via a file named abc428565580xyz exe The malicious file was uploaded to a Simple Custom Detection list in the AMP for Endpoints Portal and the currently applied policy for the Windows clients was updated to reference the detection list Verification testing scans on known infected systems shows that AMP for Endpoints is not detecting the presence of this file as an indicator of compromise What must be performed to ensure detection of the malicious file?

Options:

A.  

Upload the malicious file to the Blocked Application Control List

B.  

Use an Advanced Custom Detection List instead of a Simple Custom Detection List

C.  

Check the box in the policy configuration to send the file to Cisco Threat Grid for dynamic analysis

D.  

Upload the SHA-256 hash for the file to the Simple Custom Detection List

Discussion 0
Question # 205

What is the difference between EPP and EDR?

Options:

A.  

EPP focuses primarily on threats that have evaded front-line defenses that entered the environment.

B.  

Having an EPP solution allows an engineer to detect, investigate, and remediate modern threats.

C.  

EDR focuses solely on prevention at the perimeter.

D.  

Having an EDR solution gives an engineer the capability to flag offending files at the first sign of malicious behavior.

Discussion 0
Question # 206

An engineer needs to configure a Cisco Secure Email Gateway (SEG) to prompt users to enter multiple forms of identification before gaining access to the SE

G.  

The SEG must also join a cluster using the preshared key of cisc421555367. What steps must be taken to support this?

Options:

A.  

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG GUI.

B.  

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG CLI.

C.  

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG CLI

D.  

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG GUI.

Discussion 0
Question # 207

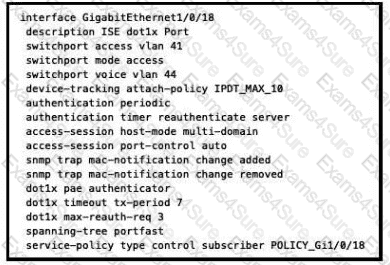
Refer to the exhibit.

Question # 207

What will occur when this device tries to connect to the port?

Options:

A.  

802.1X will not work, but MAB will start and allow the device on the network.

B.  

802.1X will not work and the device will not be allowed network access

C.  

802 1X will work and the device will be allowed on the network

D.  

802 1X and MAB will both be used and ISE can use policy to determine the access level

Discussion 0
Question # 208

When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?

Options:

A.  

It applies the next identification profile policy.

B.  

It applies the advanced policy.

C.  

It applies the global policy.

D.  

It blocks the request.

Discussion 0
Question # 209

Which OWASP LLM risk involves an attacker embedding hidden instructions in user input to manipulate the model’s behavior?


Options:

A.  

Output Truncation

B.  

Prompt Injection

C.  

System Prompt Leakage

D.  

Data Exfiltration

Discussion 0
Question # 210

How does Cisco Advanced Phishing Protection protect users?

Options:

A.  

It validates the sender by using DKIM.

B.  

It determines which identities are perceived by the sender

C.  

It utilizes sensors that send messages securely.

D.  

It uses machine learning and real-time behavior analytics.

Discussion 0

Free Exams Sample Questions